> [!WARNING]
> **v1.8.0-rc.1 is an opt-in test build.** Stop Drydock and back up the complete store directory before trying it. First startup imports JSON into SQLite. Downgrading requires restoring the pre-upgrade snapshot; changes made only in SQLite are not carried back. See [migration and deprecations](DEPRECATIONS.md).
> [!WARNING]
> **Updating from an older release? Read the upgrade notes first.** Three security-hardening fixes first shipped in **1.4.6** and run through the entire **1.5** line, so anyone updating from a release older than 1.4.6 is affected whatever version they land on (1.4.6, any 1.5.x, or later). They are not deprecations and have no grace period: OIDC now requires `authorization_endpoint` in your provider's discovery metadata, unauthenticated rate-limiting keys on the TCP peer address (shared bucket behind a reverse proxy), and HTTP-trigger proxy URLs must use `http(s)://`. See **[UPGRADE-NOTES.md](UPGRADE-NOTES.md)** before updating.
> [!WARNING]
> **Updating to 1.6.0-rc.3 or later?** More security-hardening fixes land with no grace period. An instance with no authentication configured — or with anonymous auth enabled but unconfirmed — now **fails closed** on upgrade, exactly like a fresh install: the container runs; protected API requests return `401`; authentication discovery/status routes remain public; and `/health` returns `503`. The SPA shell may still load, but it cannot read protected application data. Set `DD_ANONYMOUS_AUTH_CONFIRM=true` or configure `DD_AUTH_BASIC_*`/OIDC before upgrading. The session cookie is renamed `connect.sid` → `drydock.sid`, signing every existing user out once. HTTP notification triggers (plus the Hass webhook and registry icon fetches) now resolve hostnames through a guarded DNS lookup that blocks cloud-metadata/link-local targets and never follow redirects — set `allowmetadata=true` on a specific `DD_NOTIFICATION_HTTP_*` trigger if you legitimately need one. See **[DEPRECATIONS.md](DEPRECATIONS.md#enforced-security-changes-no-deprecation-window)** for full migration guidance.
**Recommended: use a socket proxy** to restrict which Docker API endpoints Drydock can access. This avoids giving the container full access to the Docker socket.
> **Note:** Compose treats `$` as variable interpolation syntax, so an argon2id hash pasted with single `$` reaches Drydock mangled. Double every `$` to `$$` when you paste the real hash, for example `$$argon2id$$v=19$$m=65536,t=3,p=4$$salt$$hash`.
```yaml
services:
drydock:
image: codeswhat/drydock
depends_on:
socket-proxy:
condition: service_healthy
volumes:
- drydock-store:/store
environment:
- DD_WATCHER_LOCAL_HOST=socket-proxy
- DD_WATCHER_LOCAL_PORT=2375
- DD_AUTH_BASIC_ADMIN_USER=admin
- "DD_AUTH_BASIC_ADMIN_HASH="
ports:
- 3000:3000
socket-proxy:
image: tecnativa/docker-socket-proxy
volumes:
- /var/run/docker.sock:/var/run/docker.sock
environment:
- CONTAINERS=1
- IMAGES=1
- EVENTS=1
- SERVICES=1
- INFO=1 # Required for daemon identity detection (notification prefixes)
# Add POST=1 and NETWORKS=1 for container actions and auto-updates
healthcheck:
test: wget --spider http://localhost:2375/version || exit 1
interval: 5s
timeout: 3s
retries: 3
start_period: 5s
restart: unless-stopped
volumes:
drydock-store:
```
Alternative: sockguard socket proxy
[sockguard](https://github.com/CodesWhat/sockguard) is a default-deny Docker socket filter from the same CodesWhat ecosystem, with a preset built for drydock:
> **Note:** Compose treats `$` as variable interpolation syntax, so an argon2id hash pasted with single `$` reaches Drydock mangled. Double every `$` to `$$` when you paste the real hash, for example `$$argon2id$$v=19$$m=65536,t=3,p=4$$salt$$hash`.
```yaml
services:
drydock:
image: codeswhat/drydock
depends_on:
sockguard:
condition: service_healthy
volumes:
- drydock-store:/store
environment:
- DD_WATCHER_LOCAL_HOST=sockguard
- DD_WATCHER_LOCAL_PORT=2375
- DD_AUTH_BASIC_ADMIN_USER=admin
- "DD_AUTH_BASIC_ADMIN_HASH="
ports:
- 3000:3000
sockguard:
image: codeswhat/sockguard
volumes:
- /var/run/docker.sock:/var/run/docker.sock
- ./sockguard.yaml:/etc/sockguard/config.yaml:ro
environment:
- SOCKGUARD_CONFIG_FILE=/etc/sockguard/config.yaml
healthcheck:
test: wget --spider http://localhost:2375/version || exit 1
interval: 5s
timeout: 3s
retries: 3
start_period: 5s
restart: unless-stopped
volumes:
drydock-store:
```
See sockguard's [`app/configs/portwing.yaml`](https://github.com/CodesWhat/sockguard/blob/dev/v1.5/app/configs/portwing.yaml) preset for a starting `sockguard.yaml` (the same preset portwing ships in its own examples).
Alternative: quick start with direct socket mount
```bash
docker run -d \
--name drydock \
-p 3000:3000 \
-v /var/run/docker.sock:/var/run/docker.sock \
-v drydock-store:/store \
-e DD_AUTH_BASIC_ADMIN_USER=admin \
-e 'DD_AUTH_BASIC_ADMIN_HASH=' \
codeswhat/drydock:latest
```
> **Warning:** Direct socket access grants the container full control over the Docker daemon. Use the socket proxy setup above for production deployments. See the [Docker Socket Security guide](https://getdrydock.com/docs/configuration/watchers#docker-socket-security) for all options including remote TLS and rootless Docker.
>
> Use single quotes around the hash value, as shown. Double quotes still let the shell expand `$` before docker ever sees it, mangling a real argon2id hash.
> Generate a password hash (`argon2` CLI — install via your package manager):
>
> ```bash
> echo -n "yourpassword" | argon2 $(openssl rand -base64 32) -id -m 16 -t 3 -p 4 -l 64 -e
> ```
>
> Or with Node.js 24.7+ (no extra packages needed):
>
> ```bash
> node -e 'const c=require("node:crypto");const s=c.randomBytes(32);const h=c.argon2Sync("argon2id",{message:process.argv[1],nonce:s,memory:65536,passes:3,parallelism:4,tagLength:64});console.log("argon2id$65536$3$4$"+s.toString("base64")+"$"+h.toString("base64"));' "yourpassword"
> ```
>
> Drydock v1.6 accepts only argon2id Basic auth hashes. Legacy `{SHA}`, `$apr1$`/`$1$`, `crypt`, and plain-text hashes are rejected; regenerate them before upgrading.
> Authentication is **required by default**. See the [auth docs](https://getdrydock.com/docs/configuration/authentications) for OIDC, anonymous access, and other options.
> Anonymous access must be explicitly confirmed with `DD_ANONYMOUS_AUTH_CONFIRM=true` on new and upgraded instances alike. Without it, an instance with no auth configured (or unconfirmed anonymous auth) starts fail-closed: protected API requests return `401`, public authentication discovery/status routes remain available, and `/health` returns `503`.
The image includes `trivy` and `cosign` binaries for local vulnerability scanning and image verification.
See the [Quick Start guide](https://getdrydock.com/docs/quickstart) for Docker Compose, socket security, reverse proxy, and alternative registries.
What changed in each release is in [`CHANGELOG.md`](CHANGELOG.md) and on the [GitHub Releases](https://github.com/CodesWhat/drydock/releases) page.
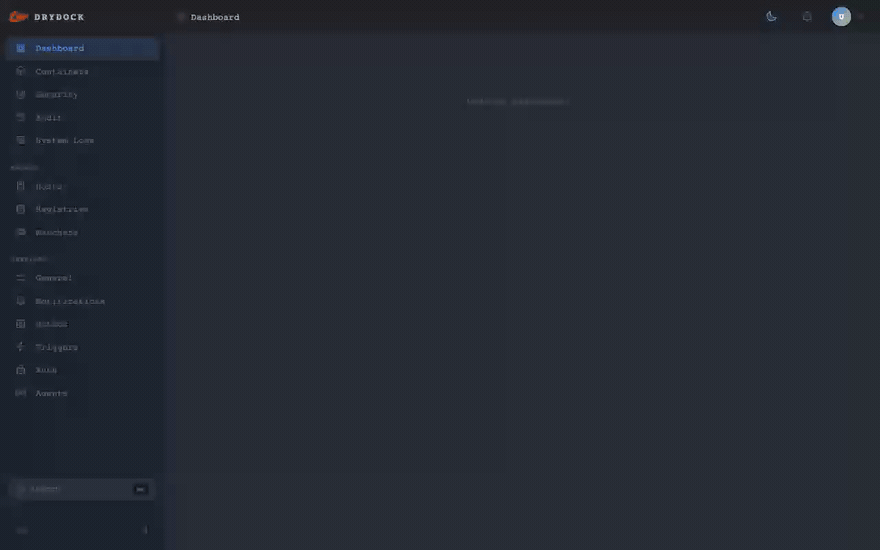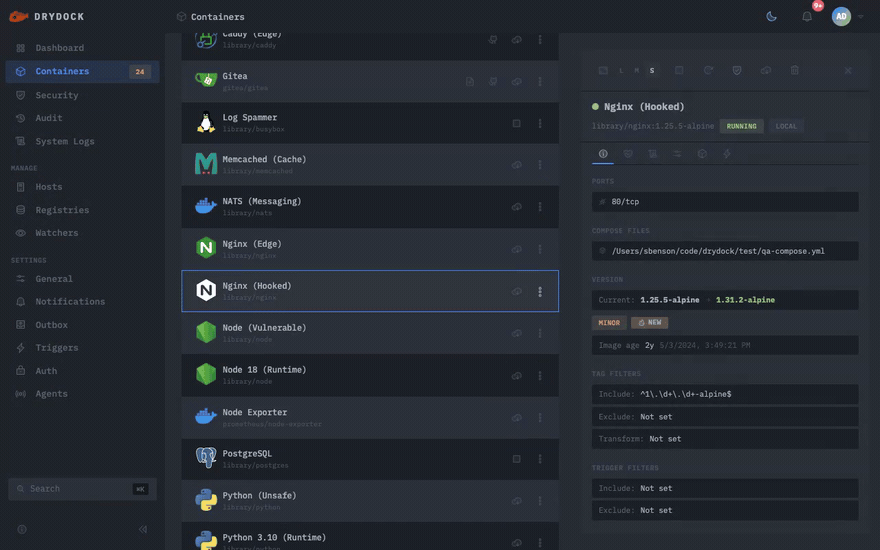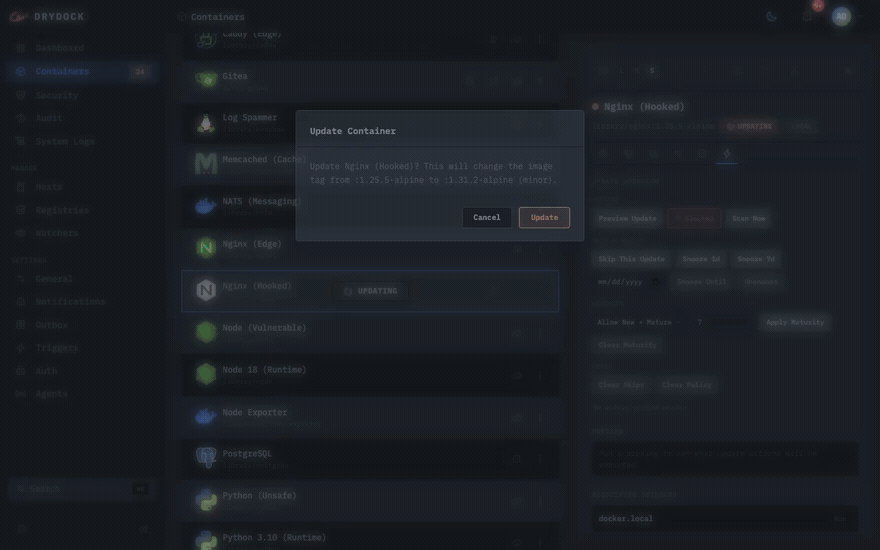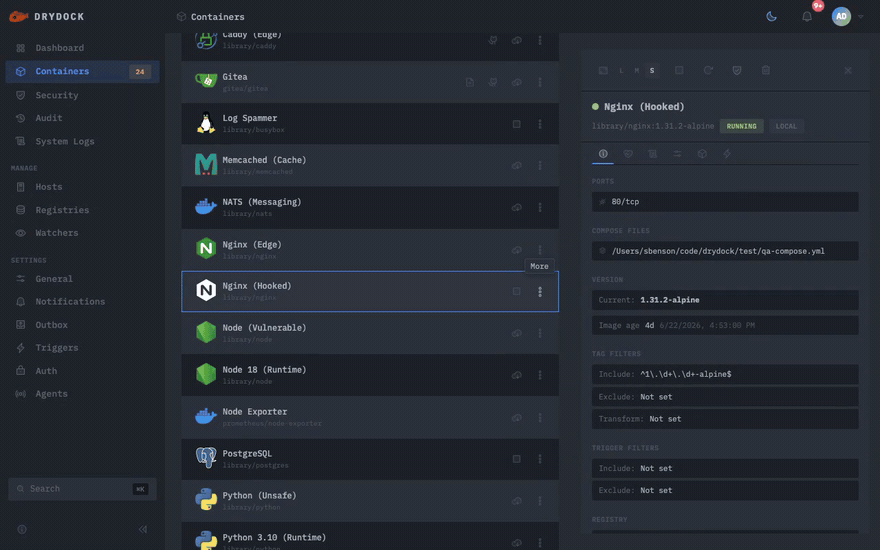
Screenshots & Live Demo
Spot an update, see exactly what changes, apply it. Backup, health check, and rollback handled.
Light
Dark
**Why look at screenshots when you can experience it yourself?**
Fully interactive — real UI, mock data, no install required. Runs entirely in-browser.
Why Drydock
Container images drift out of date silently. A base image patches a CVE, an app cuts a release, a tag moves. Unless you're watching every registry by hand, your running containers fall behind until something breaks or gets exploited.
Most tools force a tradeoff. The auto-updaters (Watchtower, Ouroboros) pull and restart with little visibility or control, and are now largely unmaintained. The dashboards (Portainer) manage containers but aren't built for update intelligence. Drydock is **monitor-first**: it watches 23 registries and tells you exactly what changed (major, minor, patch, or digest) before anything happens, then acts only when you let it. And it goes further than any of them. Trivy/Grype vulnerability scanning blocks unsafe updates, cosign verifies signatures, pre-update image backups roll back automatically on health-check failure, distributed agents cover remote hosts, and 21 notification and action integrations close the loop. The full update lifecycle, with a web UI and a REST API.
Features
| | Feature | Description |
|---|---|---|
| 🔭 | **Monitor-First Detection** | Watches every running container and classifies each available update as major, minor, patch, or digest before anything happens. Nothing changes until you say so. |
| 📦 | **23 Registry Providers** | Docker Hub, GHCR, ECR, ACR, GCR, GAR, GitLab, Quay, Harbor, Artifactory, Nexus, and 12 more. Public and private, cloud and self-hosted, with per-registry TLS and auth. |
| 🔔 | **21 Triggers** | 17 notification channels (Slack, Discord, Telegram, Teams, SMTP, MQTT, ntfy, and more) plus Docker, Docker Compose, Portainer, and Command actions, with per-event/provider templates, live preview, threshold filtering, and batch mode. |
| 🥊 | **Update Bouncer** | Trivy/Grype vulnerability scanning blocks unsafe updates before they deploy, with cosign signature verification and SBOM generation (CycloneDX and SPDX). |
| ↩️ | **Image Backup & Auto Rollback** | Pre-update image snapshots with configurable retention, automatic rollback on health-check failure, and one-click manual rollback from the UI. |
| 🪝 | **Lifecycle Hooks** | Pre and post-update shell commands via container labels, with per-hook timeouts and abort-on-failure control. |
| 🗂️ | **Docker Compose Updates** | Pull and recreate Compose services through the Docker Engine API with YAML-preserving image patching. |
| 🎛️ | **Per-Container Policy** | Regex tag rules and trigger routing use `dd.*` labels; maturity gates, skip/snooze/pin, and maintenance windows are stored via UI/API or watcher configuration. Persistent group policies set update-policy defaults and restrict-only action rules for every current and future member of a group. |
| 🛰️ | **Distributed Agents** | Monitor remote Docker hosts over SSE. Portwing 0.9.0+ agents work over inbound Standard HTTP or dial-out Edge WebSocket transport; Drydock 1.6.0-rc.11+ can run native registry checks and single/batch Docker updates controller-side through either authenticated path. Edge also carries continuous live logs with no inbound port required; `DD_EXPERIMENTAL_PORTWING=false` remains an emergency disable. |
| 🖥️ | **Web Dashboard** | Vue 3 UI with a zero-dependency customizable widget grid, responsive table/card views, live SSE updates, notification-bell controls, and per-container detail, logs, and stats. |
| 🔗 | **REST API & Webhooks** | Token-authenticated endpoints for CI/CD watch and update triggers, plus signed registry webhook ingestion for push events. |
| 🔐 | **OIDC Authentication** | Secure the dashboard with OpenID Connect (Authelia, Auth0, Authentik). All auth flows fail closed by default. |
| 📈 | **Prometheus Metrics** | Built-in `/metrics` endpoint with optional auth bypass for Prometheus and Grafana monitoring stacks. |
| 🌍 | **17 UI Locales** | Fully wired translation system with English complete and 16 community-maintained locales synced through Crowdin, switchable in Config. |
| 🔒 | **ReDoS-Immune Regex** | Every user-supplied tag pattern compiles via re2js (a pure-JS RE2 port) for linear-time matching that can't be stalled by a catastrophic-backtracking pattern. |
> Watchtower was archived in December 2025 and its last release was v1.7.1 (November 2023). An unofficial community fork, nicholas-fedor/watchtower, is still actively released.
> Compiled from each project's public documentation and repositories, 2026-08-29.
> Contributions welcome if any information is inaccurate.
Migration
Migrating from WUD (What's Up Docker?)
Drydock v1.6 no longer loads `WUD_*` environment variables or `wud.*` labels at runtime. Rewrite them before starting the upgraded service; persisted state still migrates automatically. Use `docker exec -it drydock node dist/index.js config migrate --dry-run` to preview, then `docker exec -it drydock node dist/index.js config migrate --file .env --file compose.yaml` to rewrite configuration to `DD_*` and `dd.*` naming.
Roadmap
Version themes & highlights
This direction covers at least the next twelve months, through August 2027.
High-level themes only; see [CHANGELOG.md](CHANGELOG.md) for per-release detail.
| Version | Theme | Highlights |
| --- | --- | --- |
| **v1.3.x** ✅ | Security & Stability | Trivy scanning, Update Bouncer, SBOM, 7 new registries, 4 new triggers, re2js regex engine |
| **v1.4.x** ✅ | UI Modernization & Hardening | Tailwind 4 + custom components, 6 themes, Cmd/K palette, OpenAPI 3.1, compose-native YAML updates, dual-slot scanning, OIDC hardening |
| **v1.5.0** ✅ | Observability & i18n | trigger taxonomy split (`DD_ACTION_*`/`DD_NOTIFICATION_*`), WebSocket log viewer, dashboard customization, resource monitoring, notification outbox + DLQ, security scan digest, 17 locales, SSE Last-Event-ID replay, edge agent dial-out with Ed25519 auth (experimental, `DD_EXPERIMENTAL_PORTWING=true`) |
| **v1.5.1** ✅ | Security & Maintenance | GCR/GAR pull-auth fix, registry TLS completion (M-2), hook env-var injection hardening, `DD_SESSION_SECRET__FILE` support, debug-dump credential redaction, secret-file permission check, maturity gate deadlock fix, full UI translatability + community translations, maintenance-window auto-apply gate, container uptime display, Tag/Version column split surfacing software version (OCI label, with `dd.inspect.tag.path` dual-write + opt-in `dd.inspect.tag.version-only` routing), opt-in compose mount-prefix matching, `${currentReleaseNotes}` template var |
| **v1.5.2** ✅ | Policy & Pinned-Tag Reliability | Recreation-safe maturity/skip/snooze policy retention, pinned-tag digest rebuild detection and informational same-family insights, rollback-candidate cleanup, rollback-cascade prevention, explicit-MAC preservation, and local-image registry-skip behavior |
| **v1.6.0** ✅ | Notifications, Policy & Release Intel | Per-rule/per-trigger notification templates with live preview, notification-bell preferences, cross-device preference sync, zero-dependency custom dashboard grid ([#281](https://github.com/CodesWhat/drydock/issues/281)), declarative update policy ([#320](https://github.com/CodesWhat/drydock/issues/320)), maturity stabilization countdown + immediate candidate visibility + manual override ([#406](https://github.com/CodesWhat/drydock/discussions/406)), actionable Update Status panel and global `notify` / `manual` / `auto` update mode ([#325](https://github.com/CodesWhat/drydock/discussions/325)), watcher/imgset/container tag-policy inheritance plus stacked current → newer pinned-tag visibility ([#498](https://github.com/CodesWhat/drydock/issues/498)), standardized 44px Source / release notes / registry resource actions across table, cards, and details ([#295](https://github.com/CodesWhat/drydock/discussions/295)), health-status event notifications ([#198](https://github.com/CodesWhat/drydock/discussions/198)), bidirectional Home Assistant MQTT, responsive table/card list views, Trivy/Grype/both scanning across command or pinned Docker-worker backends, scanner asset pull/warm controls, off-heap deduplicated SBOM storage, Trivy long-scan correctness ([#490](https://github.com/CodesWhat/drydock/issues/490)), trigger-taxonomy migration warnings, v1.6 compatibility removals, docs/API hygiene, and `/api` → `/api/v1` migration completion with an opt-in wud-card/Homepage compatibility shim (`DD_COMPAT_WUDCARD`). |
| **v1.7.0** | Smart Updates & UX | Dependency-aware update ordering ([#219](https://github.com/CodesWhat/drydock/discussions/219)), per-action update policy ([#511](https://github.com/CodesWhat/drydock/discussions/511)), unified maturity/update-age clock, clickable port links, keyboard shortcuts, PWA, dark-theme contrast pass (WCAG 2.2) ([#850](https://github.com/CodesWhat/drydock/issues/850), [#865](https://github.com/CodesWhat/drydock/discussions/865)), `DD_TRIGGER_*` removal (end of the v1.5.0 deprecation window), curl removed from the image |
| **v1.8.0** | Fleet Management & Live Config | **Available for testing in v1.8.0-rc.1; GA pending:** SQLite storage, approval queue, YAML config, scoped watcher/notification/action policy editors and security digest templates, concurrent updates, selective bulk updates ([#232](https://github.com/CodesWhat/drydock/discussions/232)), dependency-ordering UI, images inventory/prune, fleet health and inventory refresh, shareable label grouping, notification-only exact group routing ([#1251](https://github.com/CodesWhat/drydock/pull/1251)), persistent group policies with restrict-only action rules, an effective-policy view and a Settings editor, Drydock-side overrides for label-owned container settings, TOTP two-factor sign-in with recovery codes, install-only maintenance windows ([#946](https://github.com/CodesWhat/drydock/discussions/946)), first-party auth, scoped API keys ([#469](https://github.com/CodesWhat/drydock/discussions/469)), and Home Assistant update progress/devices ([#210](https://github.com/CodesWhat/drydock/discussions/210)). **Remaining:** broader live configuration needs ownership decisions; the static image list watcher is held until after GA. |
| **v2.0+** | Platform Expansion & Beyond | Swarm/Kubernetes watchers, GitOps sync, volume browser, locally-built images watched against a declared upstream base ([#897](https://github.com/CodesWhat/drydock/discussions/897)), health gates, canary deploys, web terminal, RBAC, LDAP/AD, basic Podman support over its Docker-compatible API, CLI, Wolfi hardened image, socket proxy |
**Release and upgrade status:** v1.6.1 remains the latest stable release. v1.7.0-rc.24 remains the 1.7 GA candidate. v1.8.0-rc.1 is for opt-in testing, with the published 1.7 docs preserved separately from the active 1.8 docs.
**Compatibility:** v1.7 removes legacy trigger inputs, curl and `/api/auth/methods`. v1.8 changes MQTT entity identity and the old `/auth/strategies` response. `PUT /api/v1/settings` remains available until API v2; its `Sunset` date does not authorize removing a method from the frozen v1 API. `/api/auth/status` remains supported.
**Portwing rotation:** the Drydock controller first supports staged rotation in v1.8.0-rc.1, with compatible Portwing development builds. Published Portwing v1.0.0-rc.1 does not include the companion feature, so no compatible published Portwing version is claimed. Edge `202` means awaiting reconnect, not completed rotation.
**Open community requirements:** Cross-host dependency updates/restarts ([#219](https://github.com/CodesWhat/drydock/discussions/219)) are not implemented. The version-family core of release-count maturity ([#558](https://github.com/CodesWhat/drydock/discussions/558)) is available for testing in v1.8.0-rc.1, including an optional age fallback and bounded digest proof for versioned aliases; historical digest counting for unversioned channels remains future work. Same-host dependency ordering and its new UI do not fulfill the remote-host request. Local-build detection and safe rebuild routing remain future work ([#897](https://github.com/CodesWhat/drydock/discussions/897)); none of these entries is a release-date commitment. A process-wide digest default ([#657](https://github.com/CodesWhat/drydock/discussions/657)) is available for testing in v1.8.0-rc.1 through `DD_DEFAULTS_WATCH_DIGEST`; configure each agent separately.
Real-time chat and early support: **[CodesWhat Discord](https://discord.gg/mWHCPJRzSx)**
Bugs and concrete feature requests go to **[GitHub Issues](https://github.com/CodesWhat/drydock/issues)**; open-ended questions, ideas, and show-and-tell go to **[GitHub Discussions](https://github.com/CodesWhat/drydock/discussions)**; real-time chat happens on the **[CodesWhat Discord](https://discord.gg/mWHCPJRzSx)**.
### Community QA
Thanks to the users who helped test v1.4.0 and v1.5.0 release candidates and reported bugs:
[@RK62](https://github.com/RK62) · [@flederohr](https://github.com/flederohr) · [@rj10rd](https://github.com/rj10rd) · [@larueli](https://github.com/larueli) · [@Waler](https://github.com/Waler) · [@ElVit](https://github.com/ElVit) · [@nchieffo](https://github.com/nchieffo) · [@begunfx](https://github.com/begunfx) · [@Ra72xx](https://github.com/Ra72xx)
CodesWhat Ecosystem
Tool
Role
drydock
Container update monitoring — web UI and notification engine
Docker socket proxy — default-deny allowlist filter protecting the socket
These three tools are designed to layer: sockguard filters the socket, portwing exposes it remotely, and drydock monitors and acts on container state.
See [portwing's COMPATIBILITY.md](https://github.com/CodesWhat/portwing/blob/main/COMPATIBILITY.md) for the full compatibility matrix across all three tools.
---
**[AGPL-3.0 License](LICENSE)**
Back to top








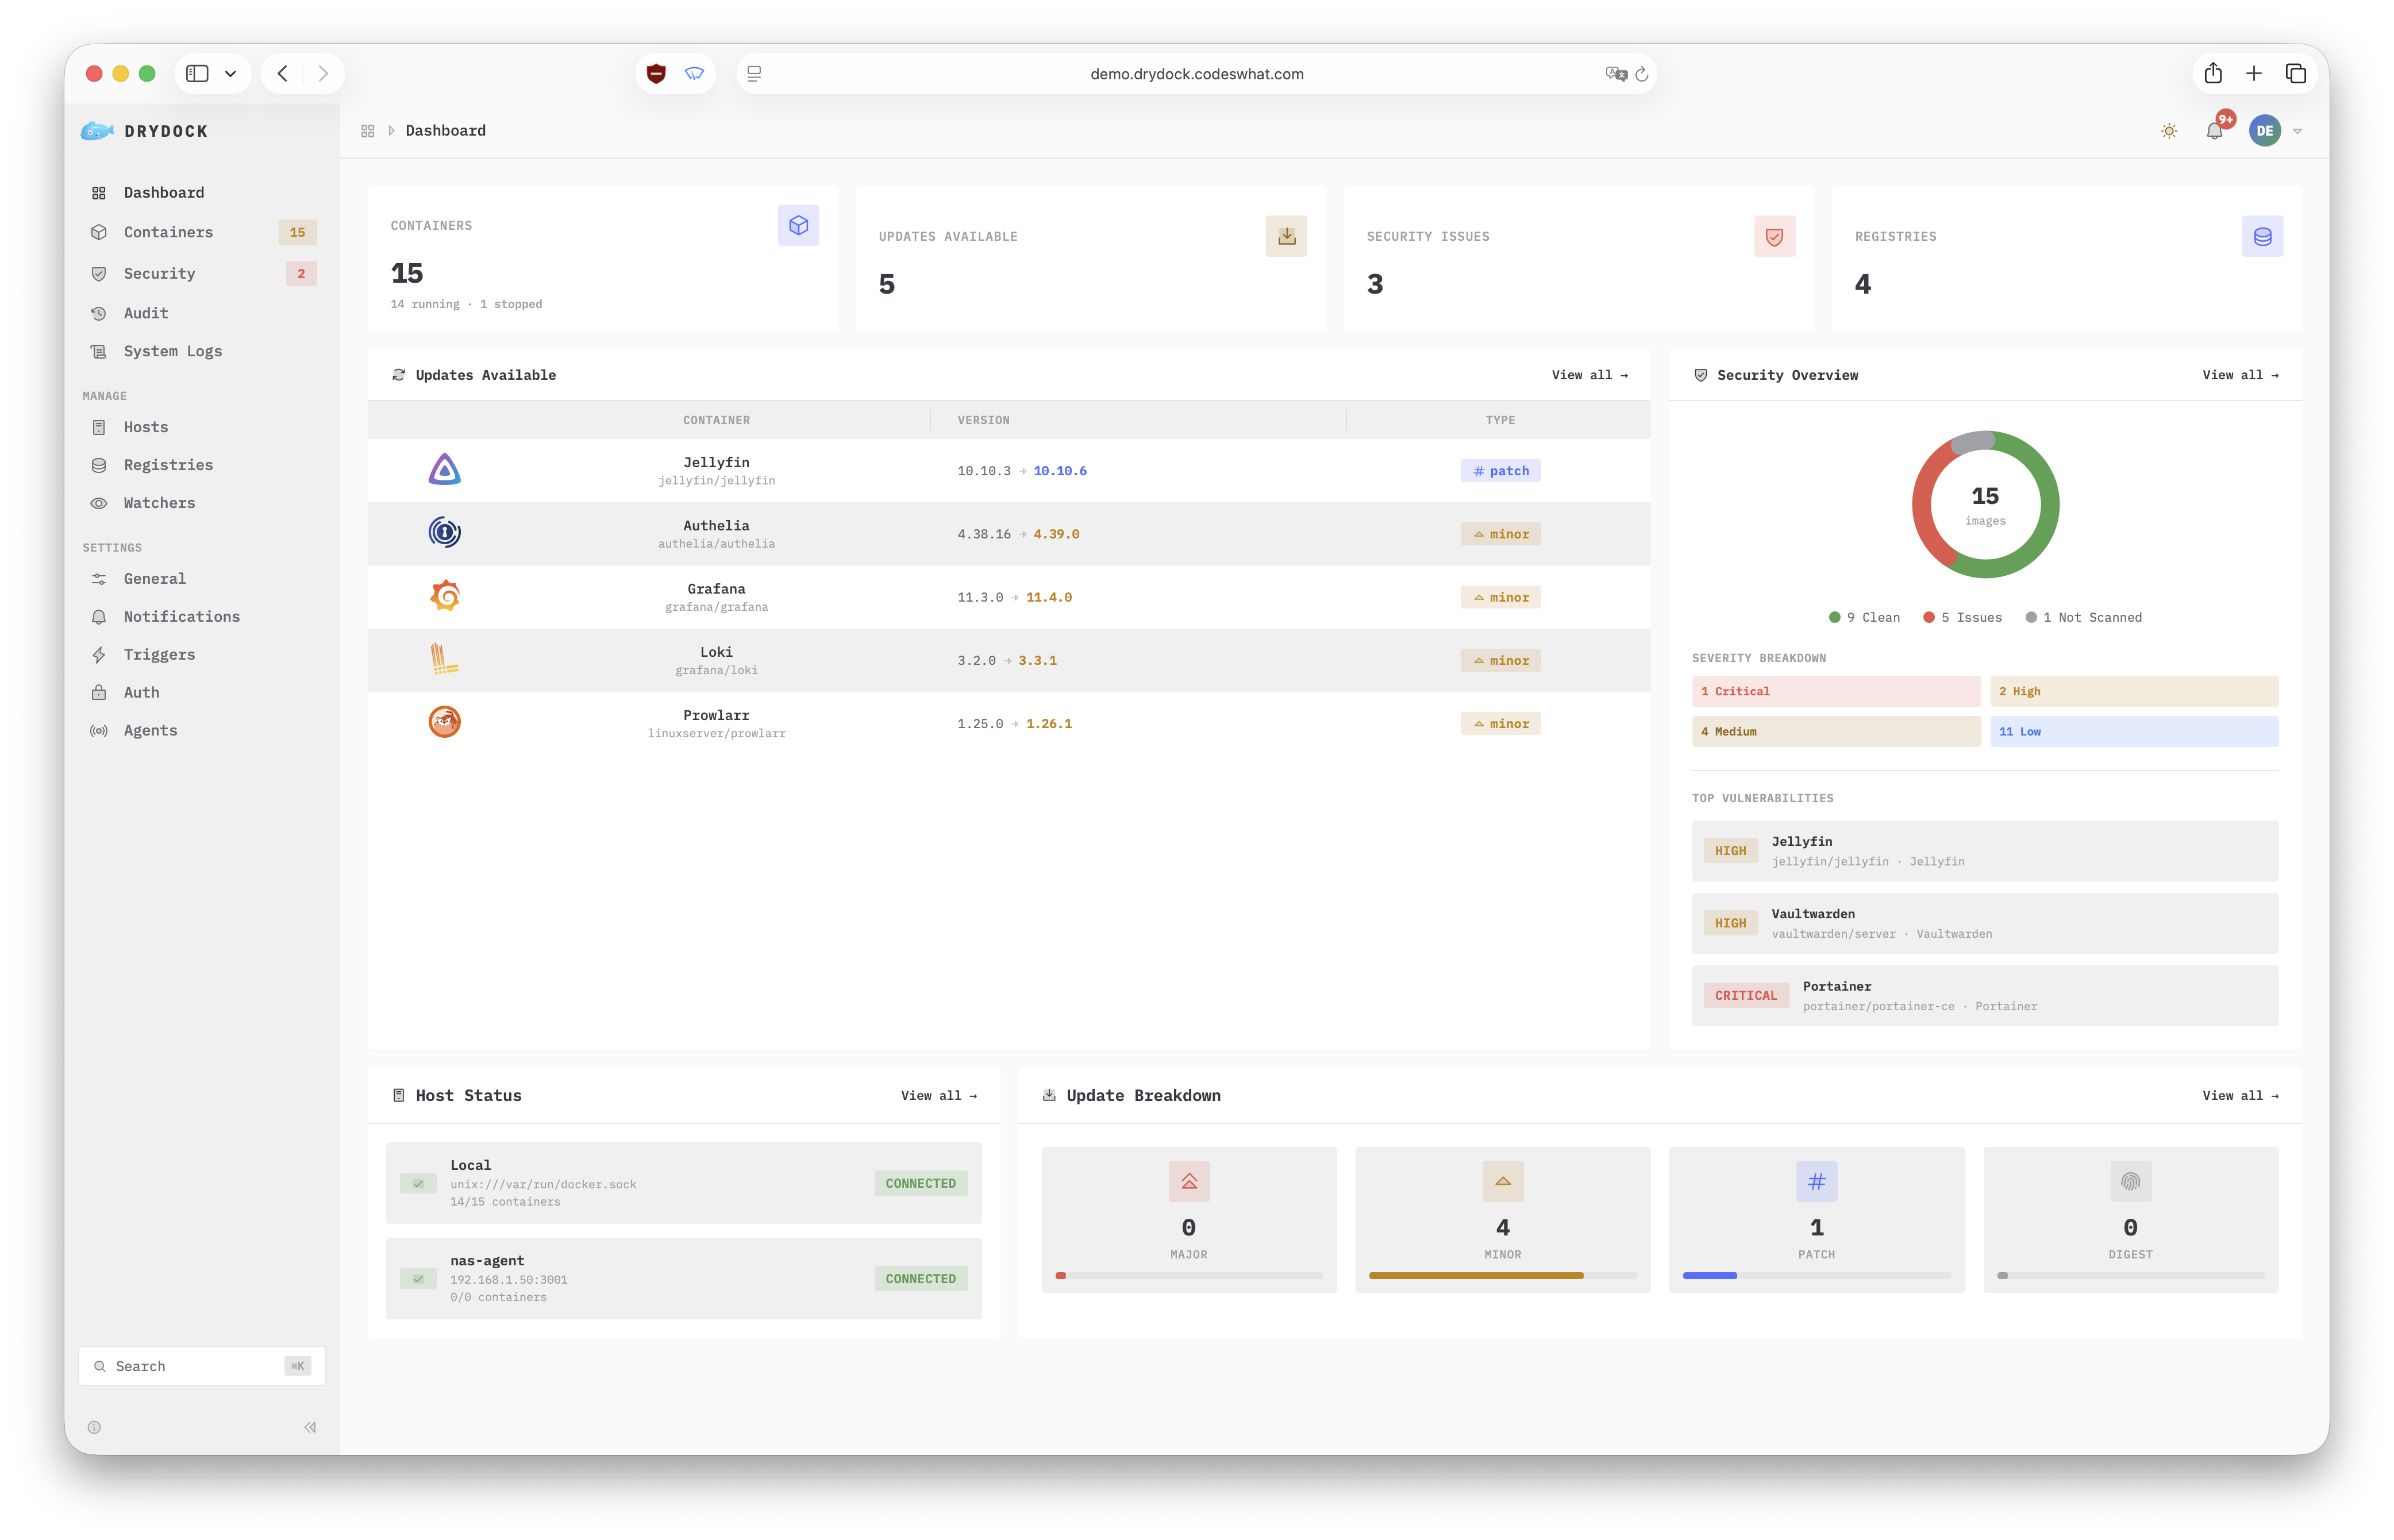
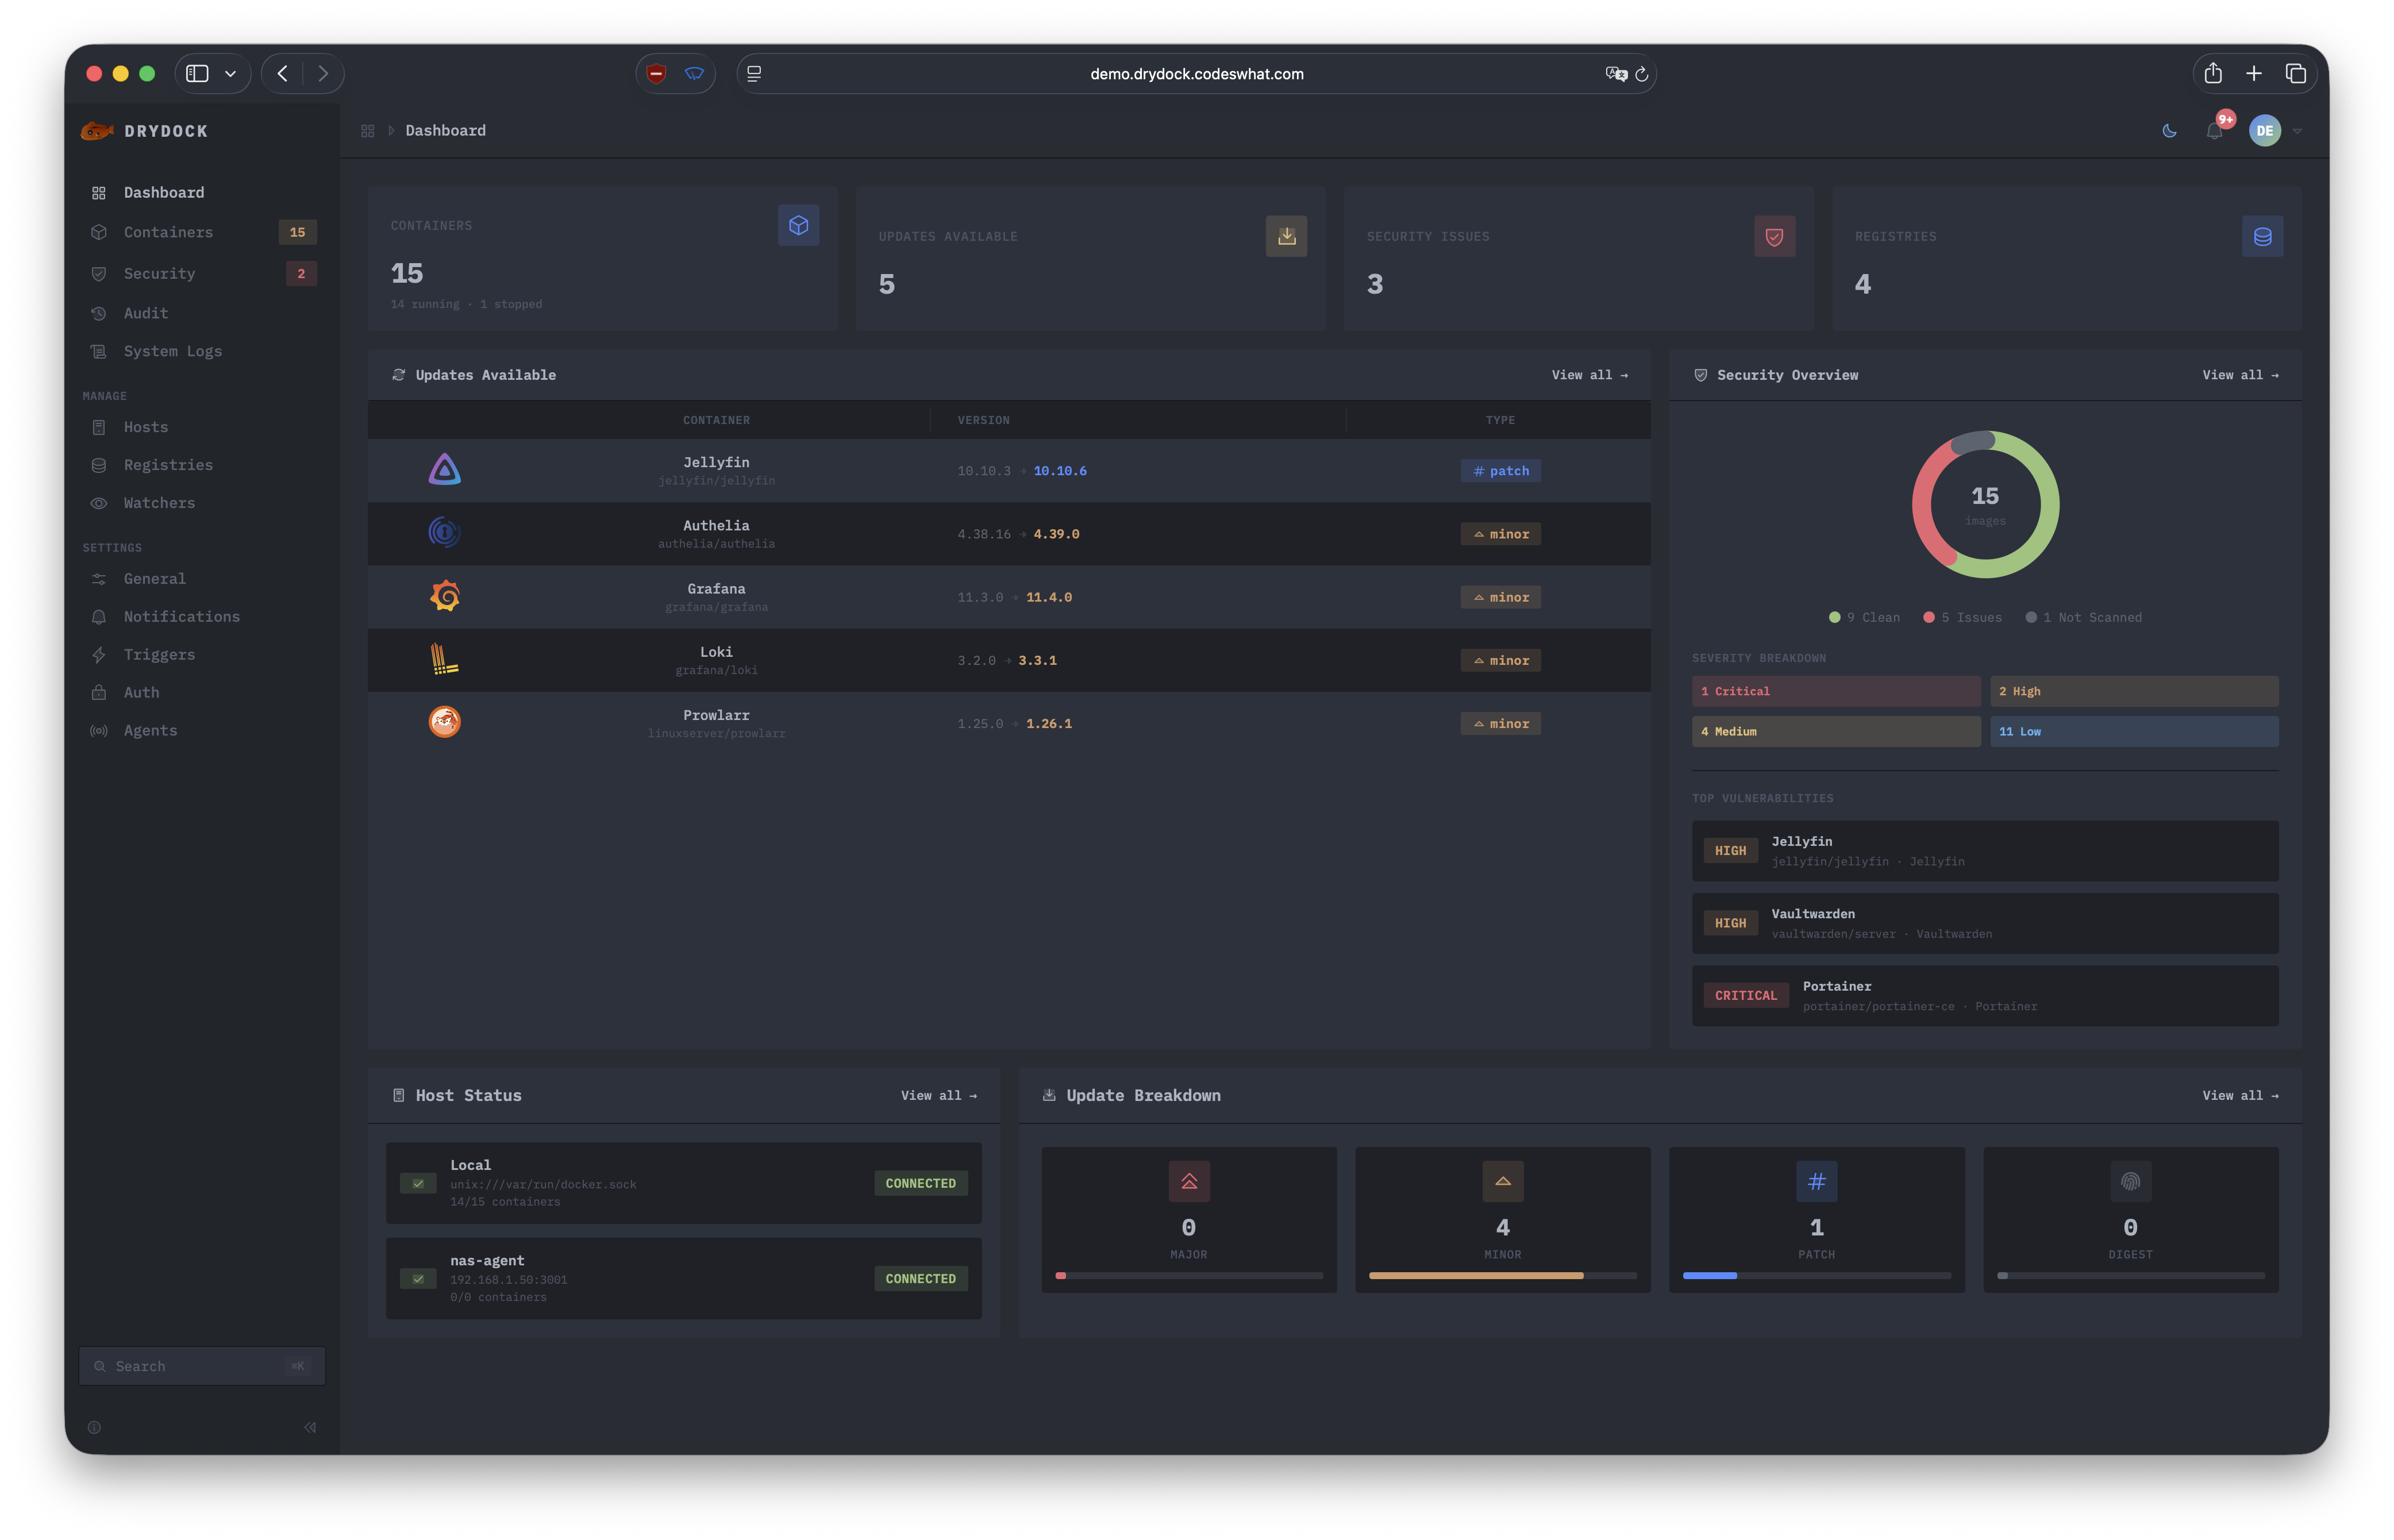
 Fully interactive — real UI, mock data, no install required. Runs entirely in-browser.
