English · 中文 · 🌐 dvalincode.dev





Open security engineering for code written by humans and AI agents.
Every repair carries its own proof.
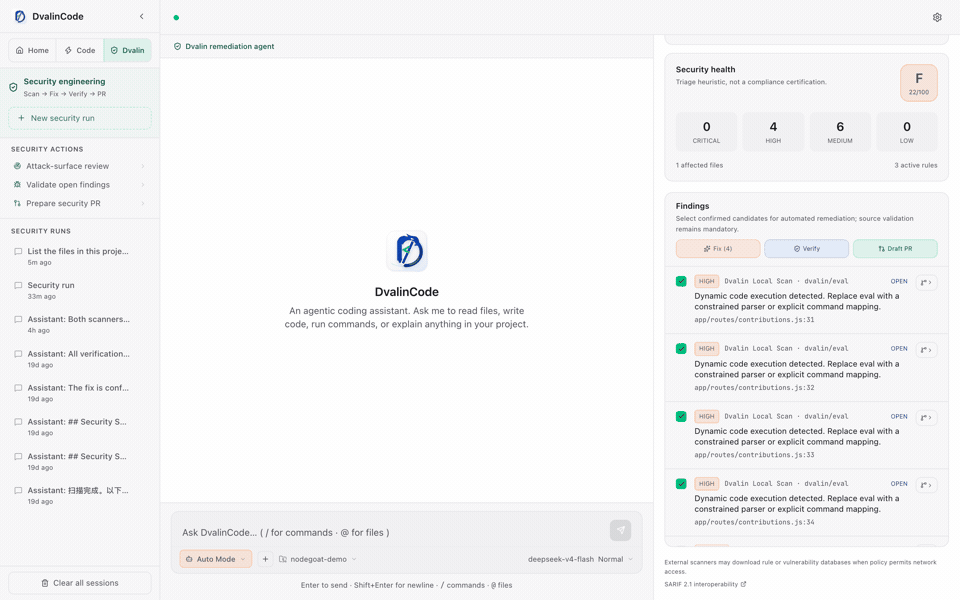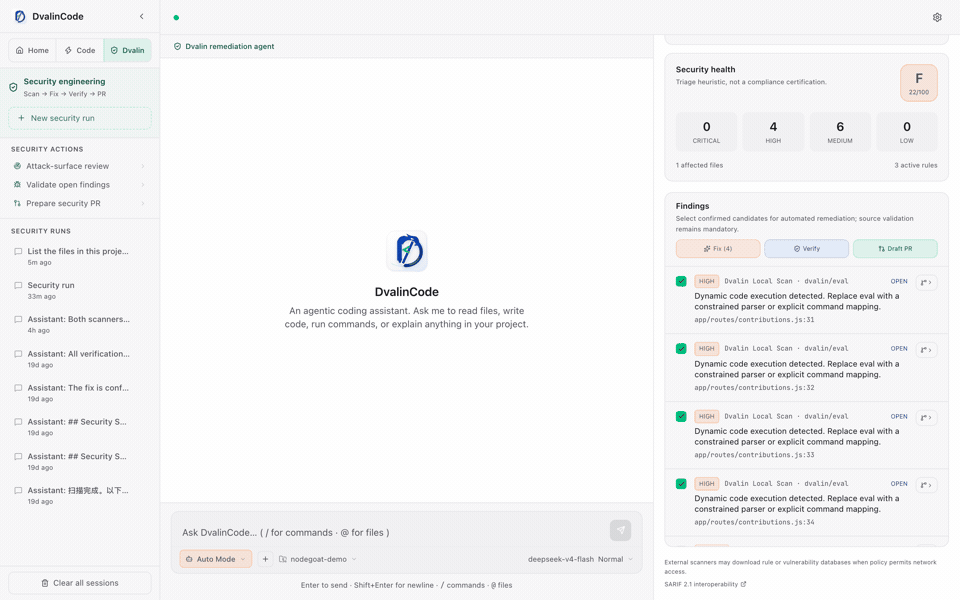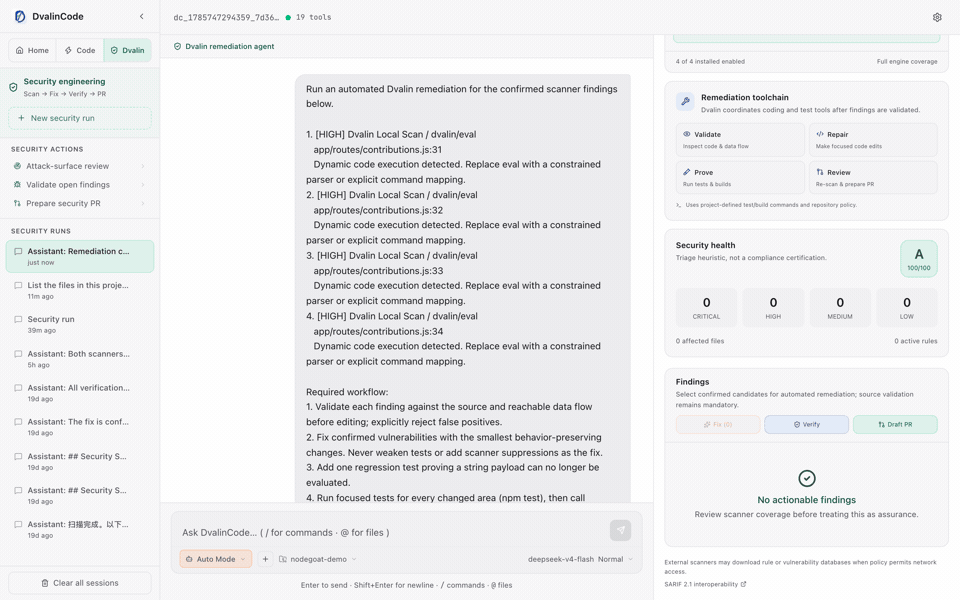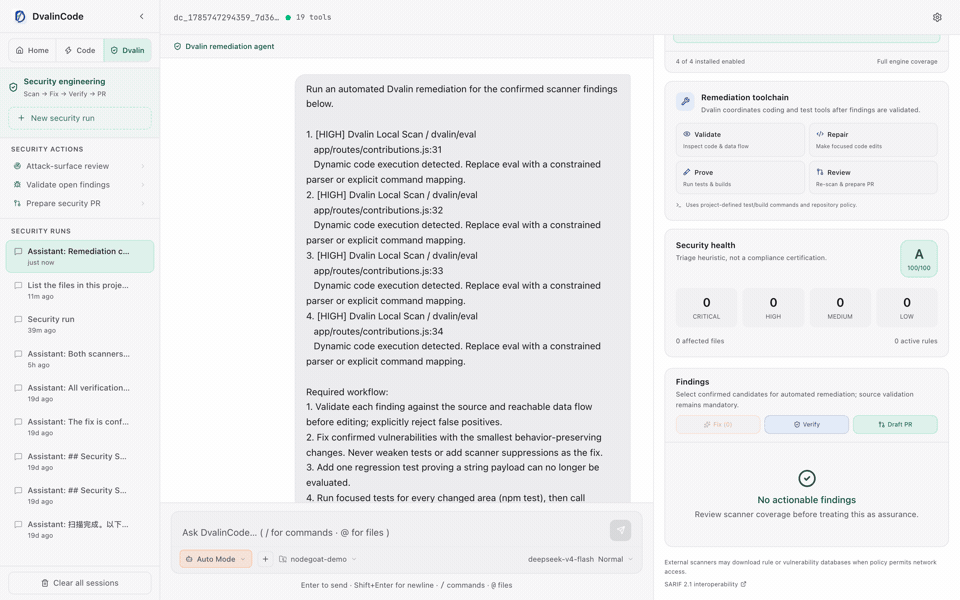
| 🏠 Home | One place for read-only Ask and approval-gated Collaborate workflows. Switch intent without leaving the project or conversation. |
| ⚡ Code | Focused autonomous coding with full tool access and Ask / Plan / Auto / Bypass permission levels. Security and browser routines no longer compete with the core coding workflow. |
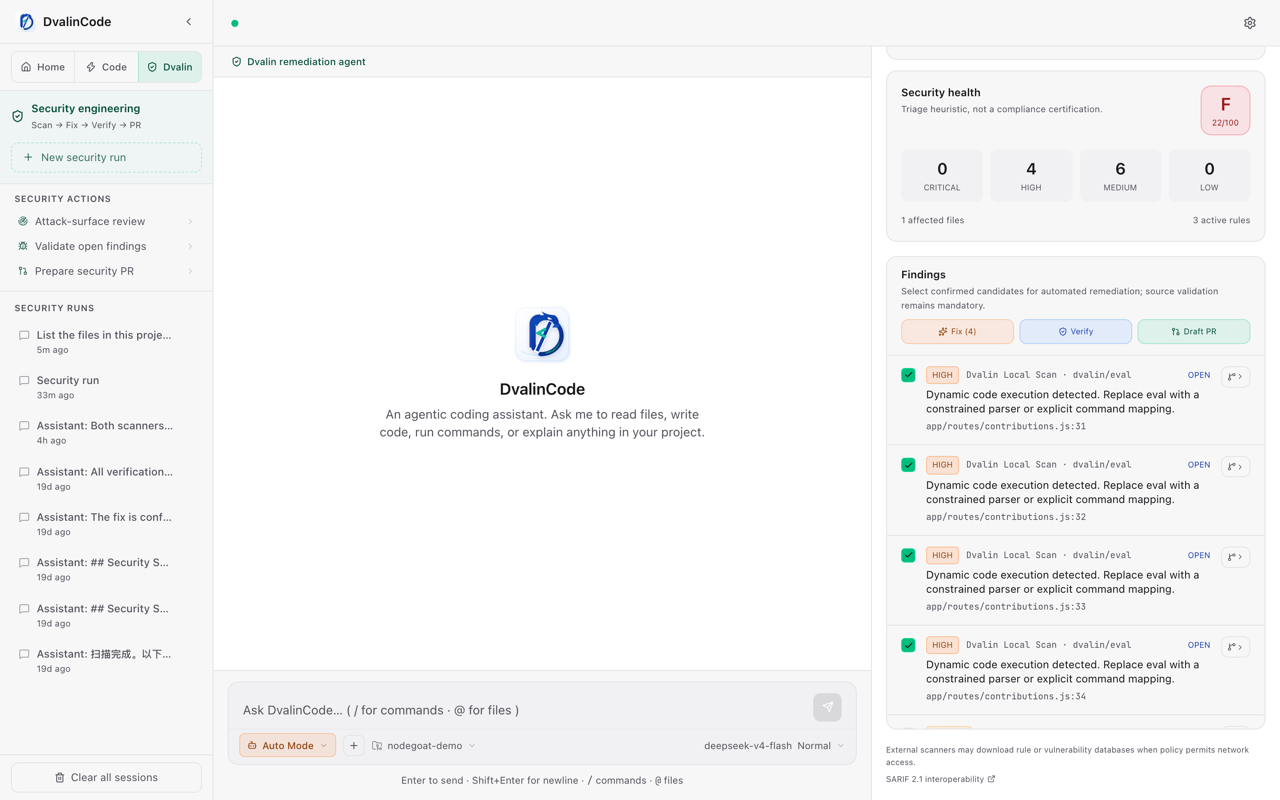
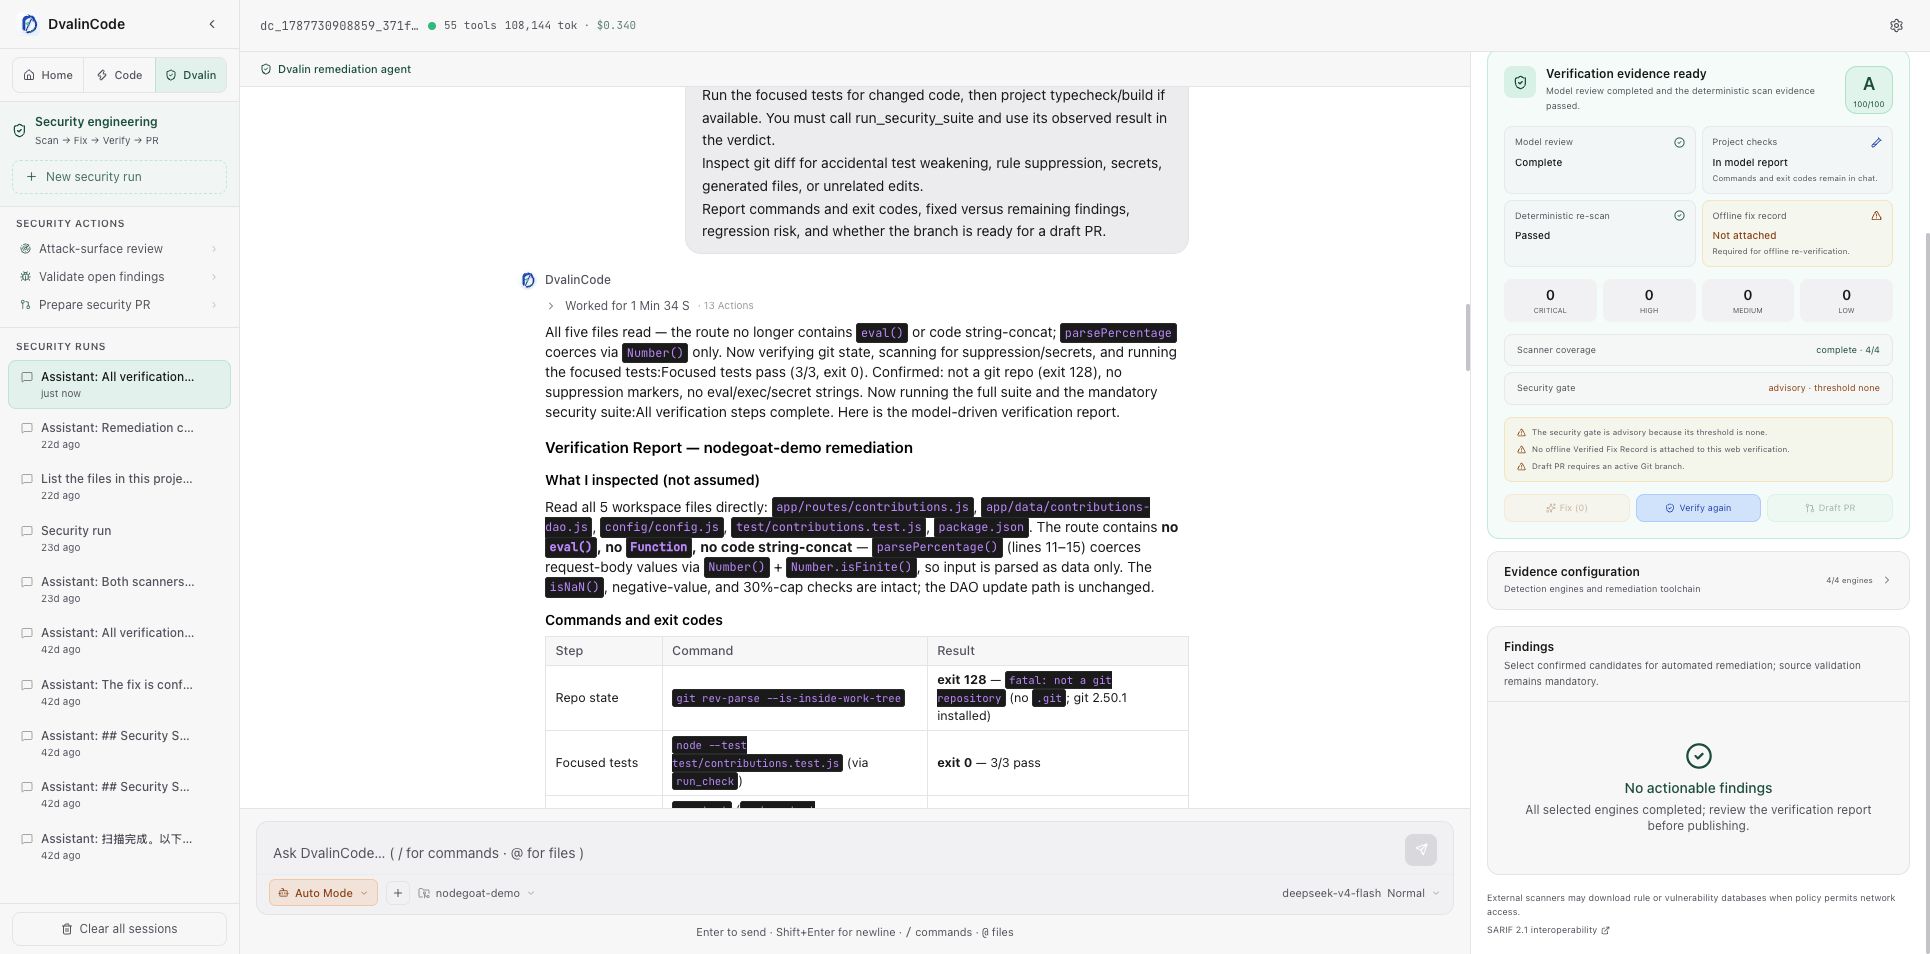
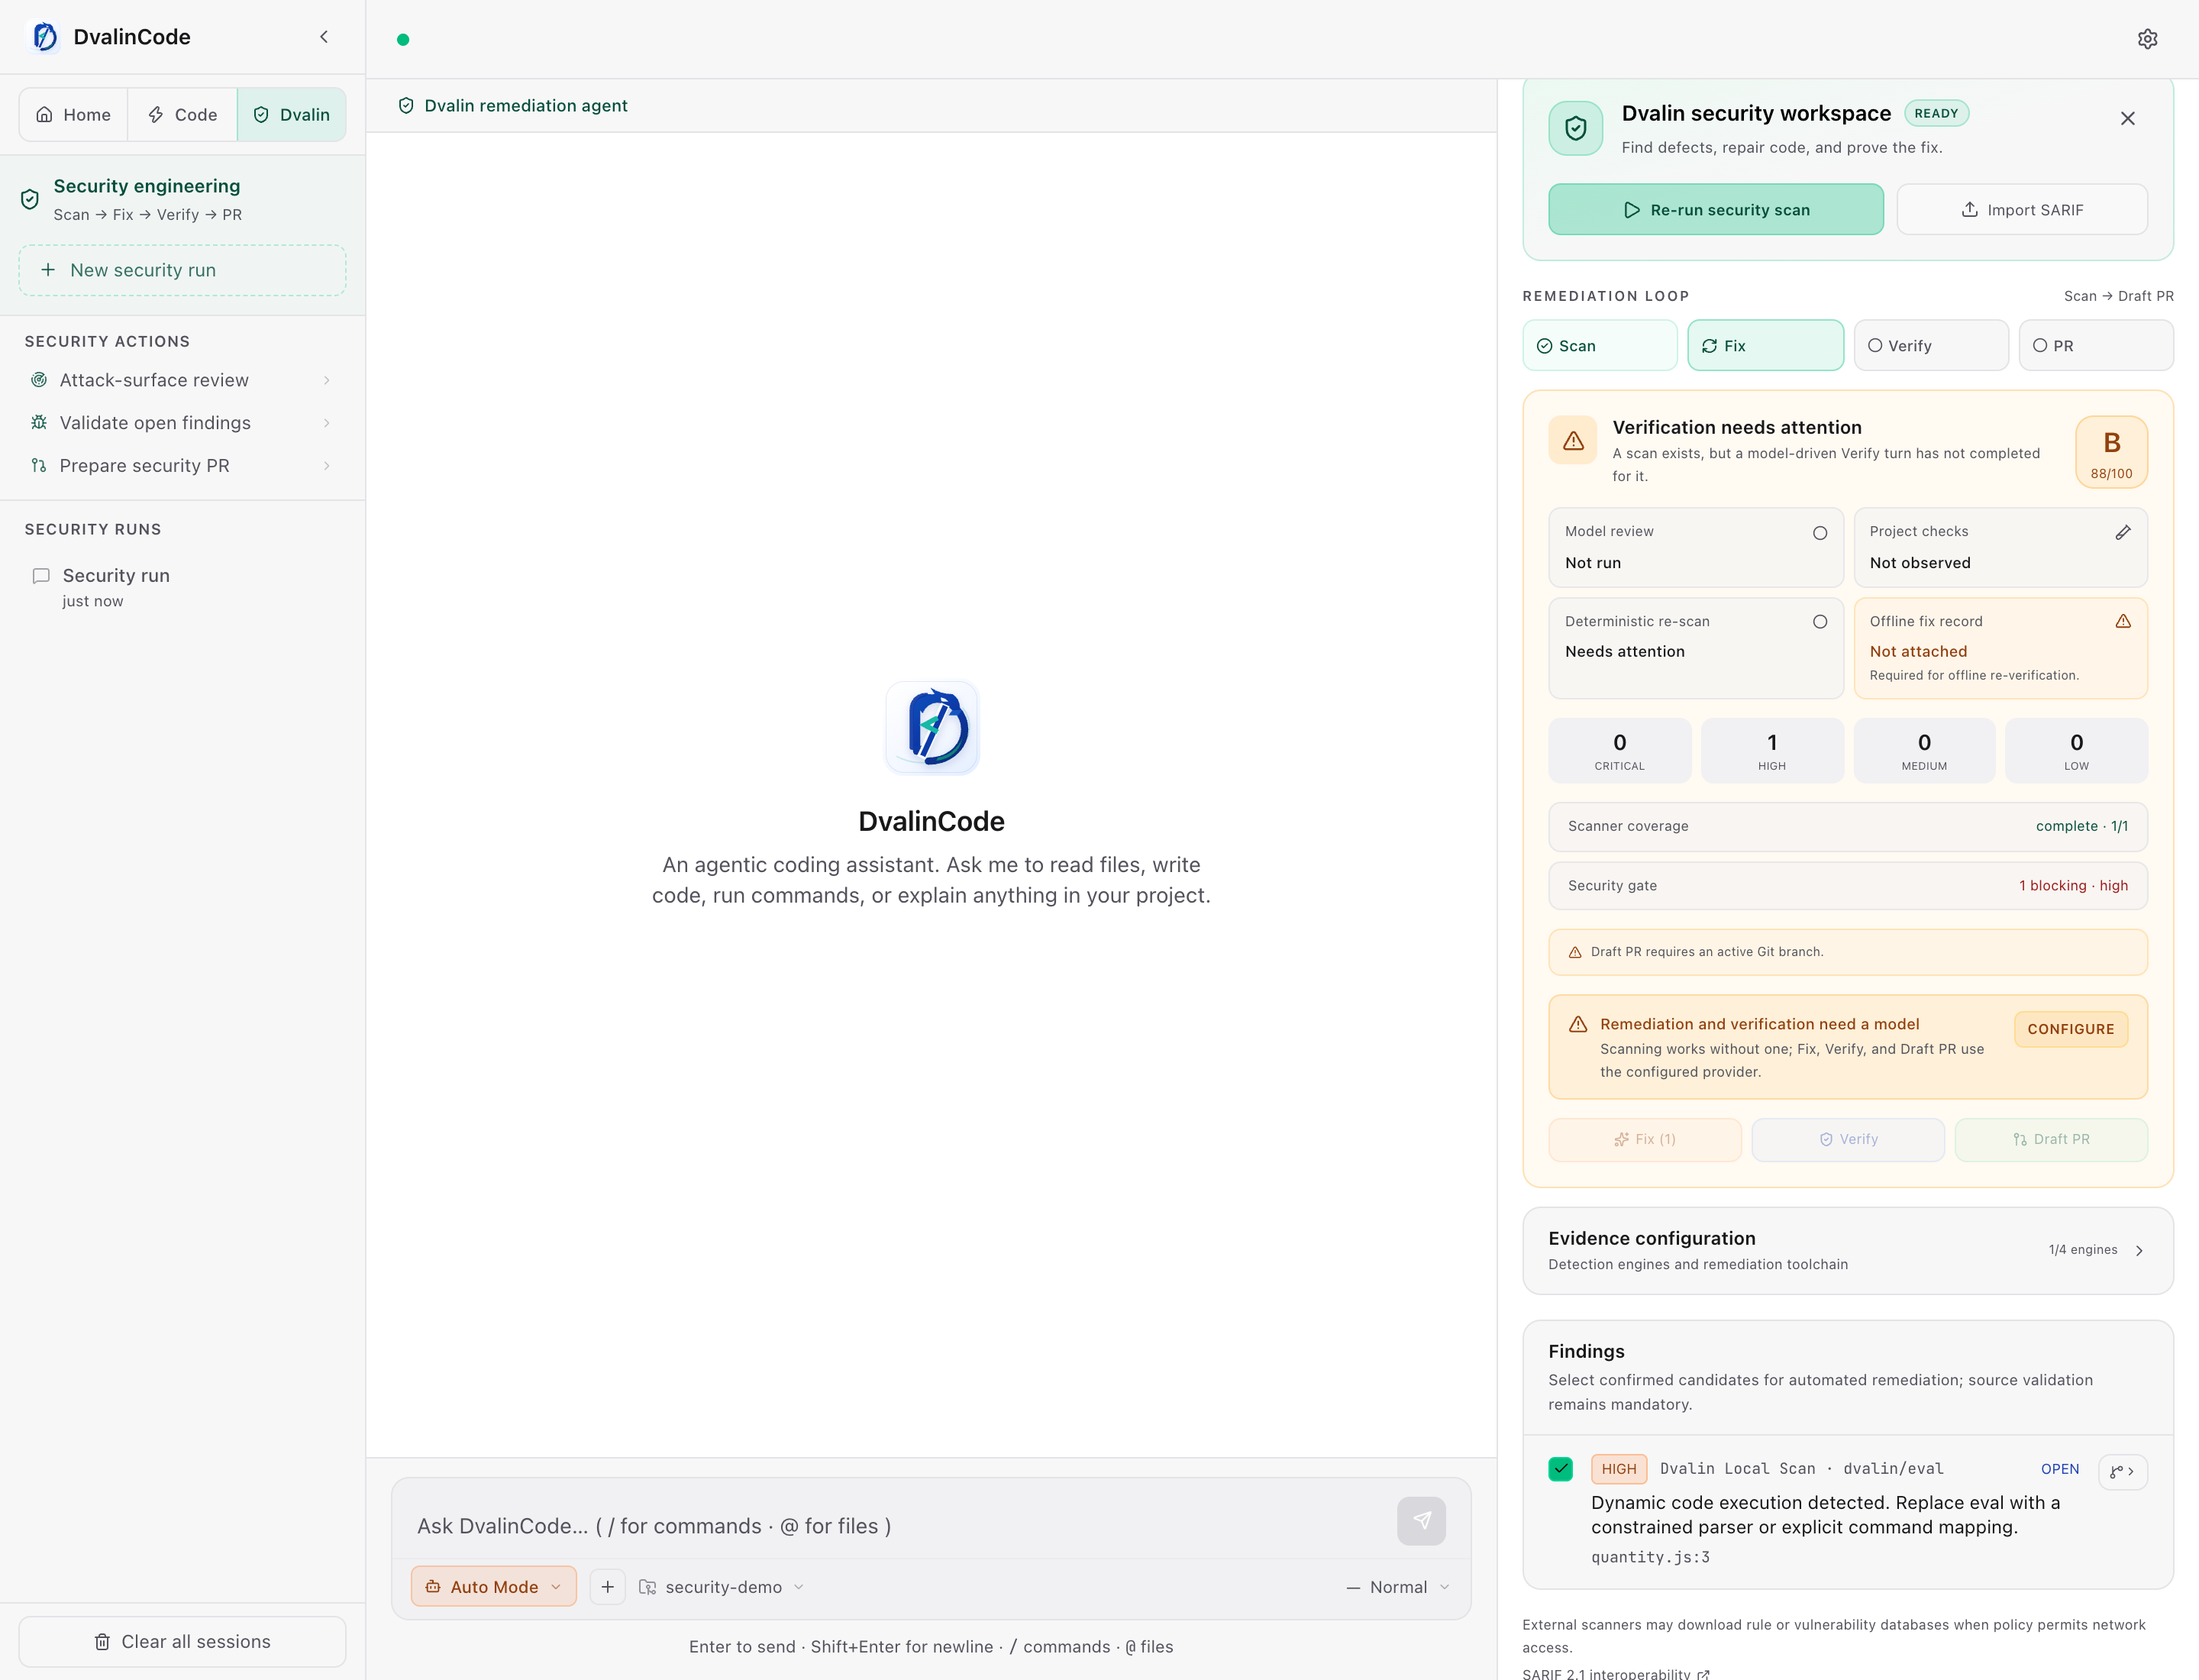
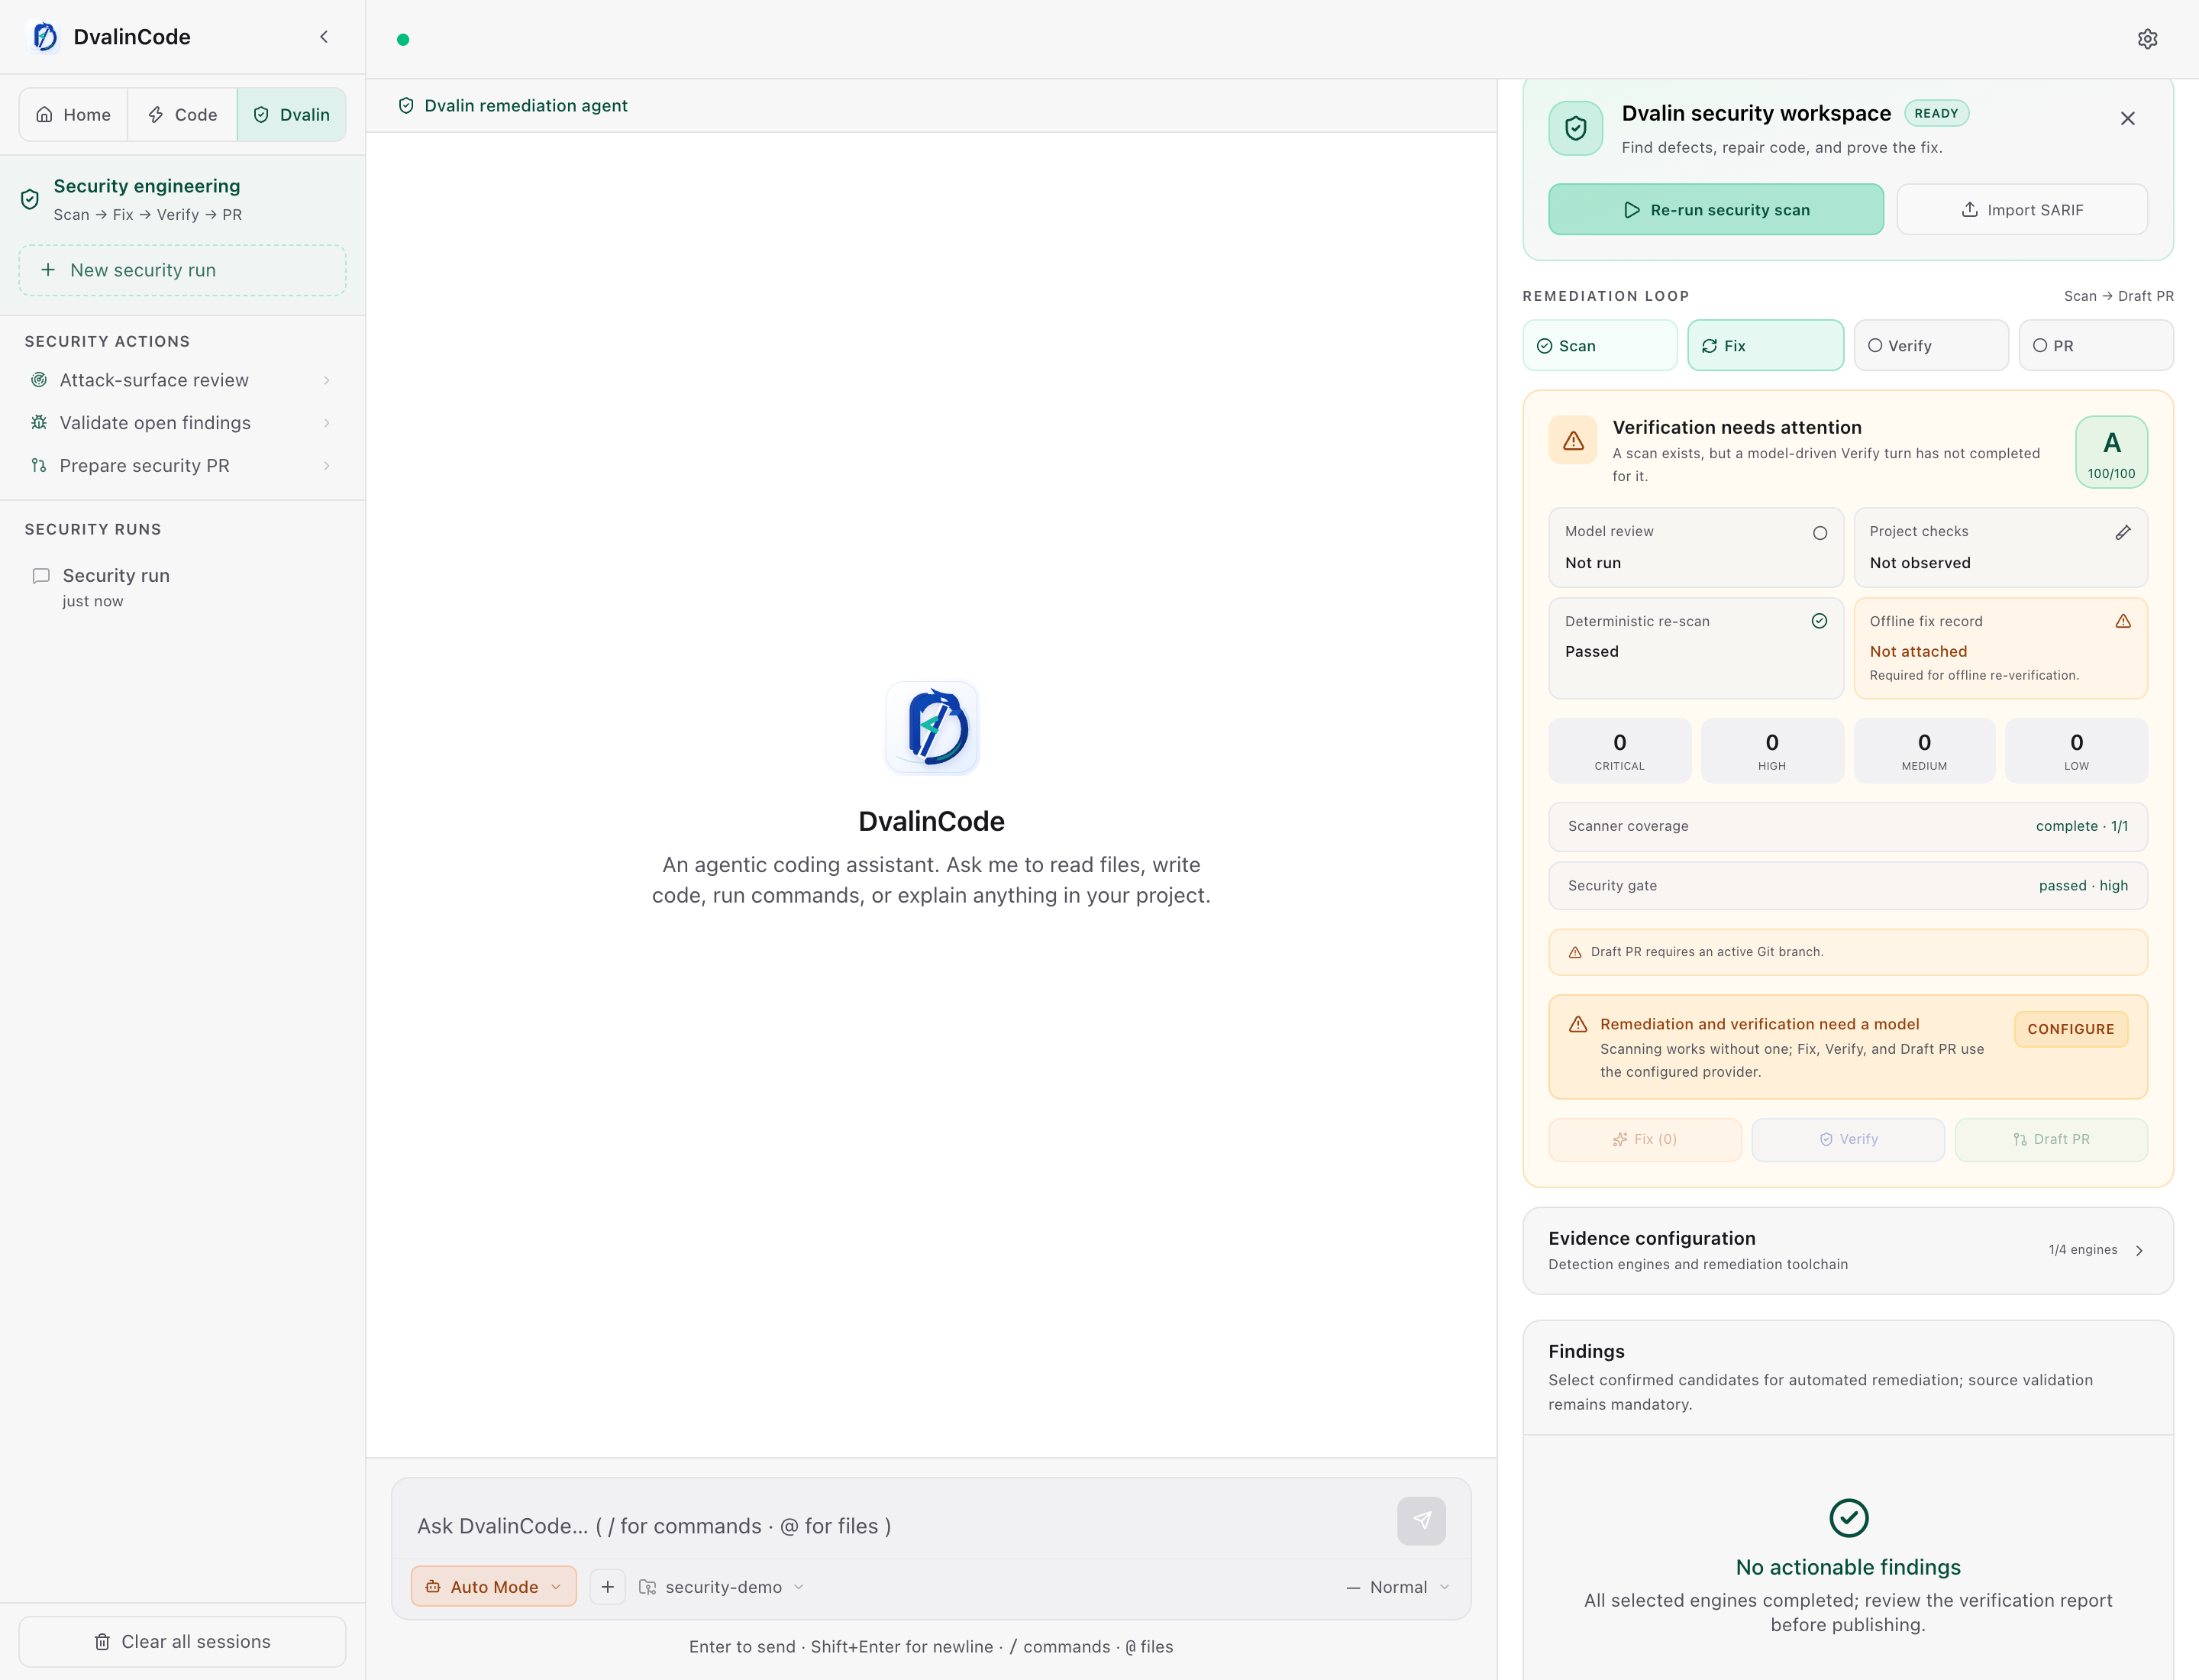
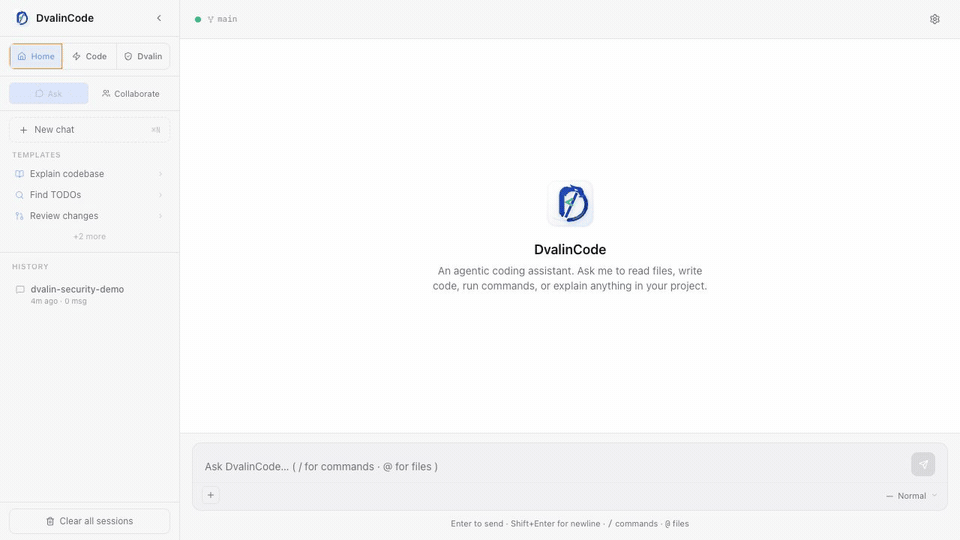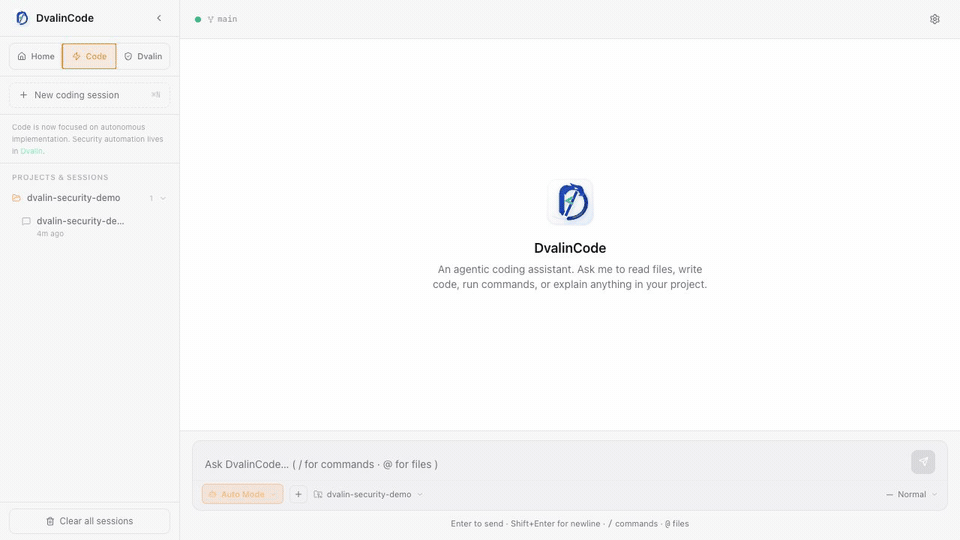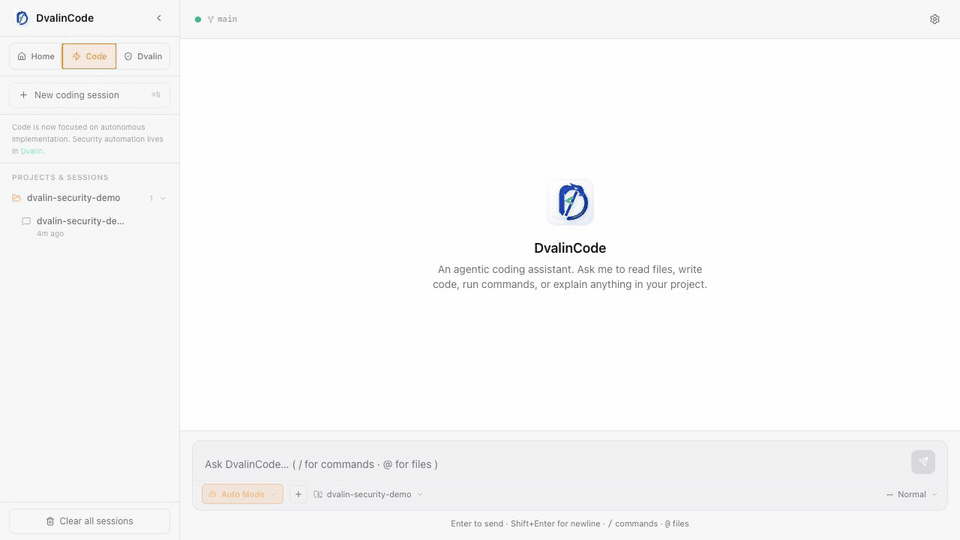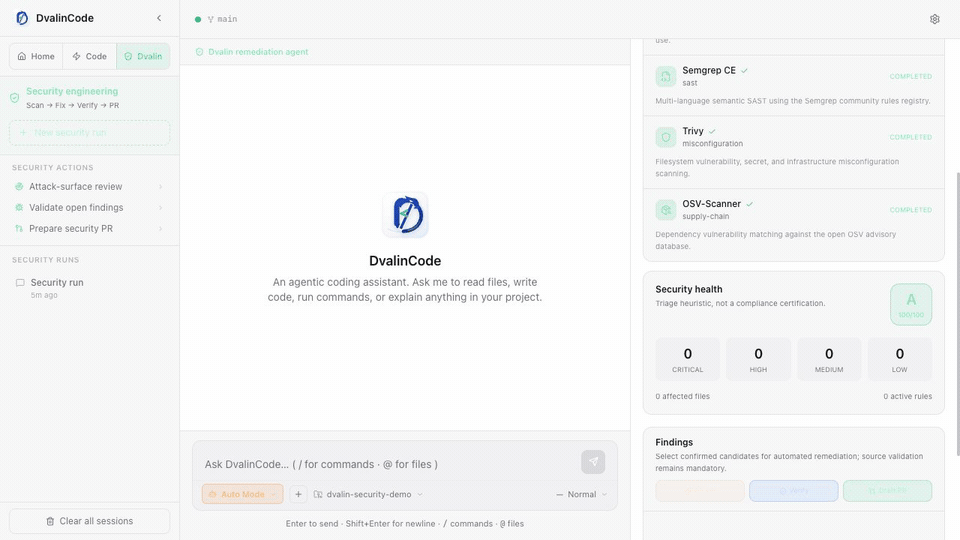
| 🛡️ Dvalin | Dedicated white-box security engineering: orchestrate the built-in scanner plus installed Semgrep CE, Trivy, and OSV-Scanner; triage findings; create isolated fixes; run tests and re-scan; then explicitly publish a reviewable draft PR. Dvalin guide → |
| 🏦 Regulated teams | Designed for finance, healthcare, security-sensitive SaaS, and internal platform teams that need AI coding under policy, audit, data minimization, and supply-chain review — not just developer convenience. |
| 🛡️ Secure remediation | Run a multi-engine scan or import SARIF from CodeQL, GitHub Code Scanning, Semgrep, or compatible scanners, then create an isolated remediation worktree and turn findings into focused repair tasks with source context, verification evidence, and PR-ready reporting. Workflow → |
| 📚 Skills | Upload, download, and inspect local skill bundles. DvalinCode ships built-in secure-code-scan and secure-code-remediation skills, plus agent tools for listing skills, reading skill instructions, scanning, listing cases, and preparing remediation worktrees. Format → |
| 🛡️ Audit trail | Every run emits a tamper-evident, hash-chained JSONL log — every file read/written, every command, every approval. A Run Report renders it as Markdown; dvalincode report verify proves the chain is intact. Threat model → |
🔒 Org policy & trust | A company — not the developer — bounds the agent. A dvalin.policy.json constrains modes, shell commands, file paths, tools, and models; a repo policy can only ever narrow the machine-level one, never widen it. Each run records the governing policy's hash. dvalincode trust prints the install's live security posture — active policy + hashes, audit status, runtime — so a reviewer can verify it directly. Policy reference → · Approvability plan → |
| 🏛️ Governance evidence | OpenSSF Scorecard, CodeQL, Dependabot, pinned GitHub Actions, CODEOWNERS, and ISO/IEC 42001 AIMS alignment docs are maintained as reviewable project evidence, and every release ships an Evidence Pack the binary produced of itself. Scorecard map → · ISO 42001 alignment → · Release evidence → |
| 📐 Open specs | PCP-1 — the provider-boundary contract (egress containment, credential containment, audit, policy binding) written as a vendor-neutral profile with test procedures, so any agent runtime can run it against its own adapters and publish the result. Not a DvalinCode test file; a checklist anyone can hold us to as well. Provider Conformance Profile → |
| 🖥️ First-class GUI | Modern web UI with code highlighting, file @-references, / slash commands, Git branch indicator, live token + cost counter, multi-profile LLM config, and a dark / light / system theme switcher. |
| 🖥️ Terminal or web — one binary | Run it bare for an interactive terminal agent with streaming output, inline approvals, and red/green diffs, or dvalincode serve to host the web GUI for browser/remote use. Both frontends drive the same agent core. |
| 🖥️ Native desktop app | DvalinCode.app — a real dock application (OS-native webview, no Electron) over the same engine. On macOS the one-line installer puts it in /Applications automatically; launch it straight from Launchpad. |
| 🪶 Zero-dependency binary | Single ~25MB executable per platform. No Node, no Python, no Docker. |
| 🔐 Local-first | Sessions, config, profiles, and audit logs live in ~/.dvalincode/. .dvalincodeignore blocks the agent from reading sensitive files. AGENTS.md in your repo becomes persistent project instructions. |
| 💾 Portable & exportable | Export all local data (memory, sessions, config, audit) to one file and import it on another machine — your setup moves with you. Any conversation downloads as a clean Markdown transcript. |

serve · shared turn-runner/compact · dvalin.json team playbook · self-contained binaries
~/.dvalincode/. To exclude sensitive files from the agent's view, drop a .dvalincodeignore in your repo root (gitignore-style patterns).
ollama pull qwen2.5-coder), then in the LLM Configuration modal pick the Ollama provider. No key, no internet, no per-token cost.
sandbox-exec; on Linux, restrictive network policies use Bubblewrap when installed. Windows has no supported subprocess network sandbox yet, so restrictive policies fail closed instead of silently running unrestricted. The native command runner itself works on all three platforms.
/bin/sh; Windows commands run through the system ComSpec (cmd.exe by default). Full native command lines support pipes, redirects, and conditional operators. The split command + args form quotes executable paths and arguments for the host shell.
~/.dvalincode/audit/run-<timestamp>-<id>.jsonl. Render it with dvalincode report --last (or see the collapsible Run Report card in the GUI). Each record is chained to the previous one with a SHA-256 hash, so any after-the-fact edit is detectable — dvalincode report verify <run-id> reports ✓ chain intact or the exact position of a break. It's tamper-evident, not tamper-proof: a local attacker who can rewrite the whole file could recompute the chain. The value is forensic/accountability. See docs/AUDIT-TRAIL.md for the full threat model.
xattr -dr com.apple.quarantine ~/.dvalincodeAGENTS.md get sent every turn?AGENTS.md from the project root before each turn and injects it under === PROJECT INSTRUCTIONS === in the system prompt. Keep it focused — it counts toward your token budget.
Every issue, idea, documentation improvement, test, and code contribution helps make DvalinCode better.
| Contributor | GitHub profile | | --- | --- | | Arthur Pan | [@arthurpanhku](https://github.com/arthurpanhku) | | Shivas | [@shivasb42](https://github.com/shivasb42) | | Aditya | [@adity982](https://github.com/adity982) | | badhope | [@weed33834](https://github.com/weed33834) | | Samran Asif | [@webdevsamran](https://github.com/webdevsamran) | | dchaudhari7177 | [@dchaudhari7177](https://github.com/dchaudhari7177) | See the [complete contribution history](https://github.com/arthurpanhku/dvalincode/graphs/contributors), including automated dependency and maintenance updates.Want to join them? Read the contribution guide and send your first pull request.