**The open behavioral classification standard for agentic AI components.**
Stable IDs, AIVSS scores, and behavioral fingerprints for every way a skill file,
MCP server, system prompt, or agent plugin can be weaponized — scored consistently,
mapped to the frameworks security teams already report against.
[](records/)
[](schema/ave-record-1.1.0.schema.json)
[](https://aivss.owasp.org)
[](https://owasp.org)
[](https://atlas.mitre.org)
[](docs/specs/ave-in-sarif.md)
[](LICENSE)
[](https://github.com/aveproject/ave/actions/workflows/tests.yml)
[-0f6e56?style=flat-square)](.github/workflows/tests.yml)
[](https://github.com/aveproject/ave/actions/workflows/codeql.yml)
[](https://github.com/aveproject/ave/actions/workflows/dependency-review.yml)
[](https://github.com/aveproject/ave/actions/workflows/secret-scan.yml)
[](https://scorecard.dev/viewer/?uri=github.com/aveproject/ave)
[](SECURITY.md)
[](CODE_OF_CONDUCT.md)
[Registry](https://aveproject.org/registry.html) · [Schema](https://aveproject.org/schema.html) · [Crosswalks](https://aveproject.org/crosswalks.html) · [Architecture](https://aveproject.org/architecture.html) · [Scoring](https://aveproject.org/scoring.html) · [API](https://api.aveproject.org) · [Scanner](https://github.com/bawbel/scanner)
---
## What is AVE?
Skill files, MCP server manifests, and system prompts are executable
instructions, not documentation. Any process that loads them runs them.
There is no compiler, no type checker, no sandbox. The runtime is an LLM
that reads natural language and acts on it.
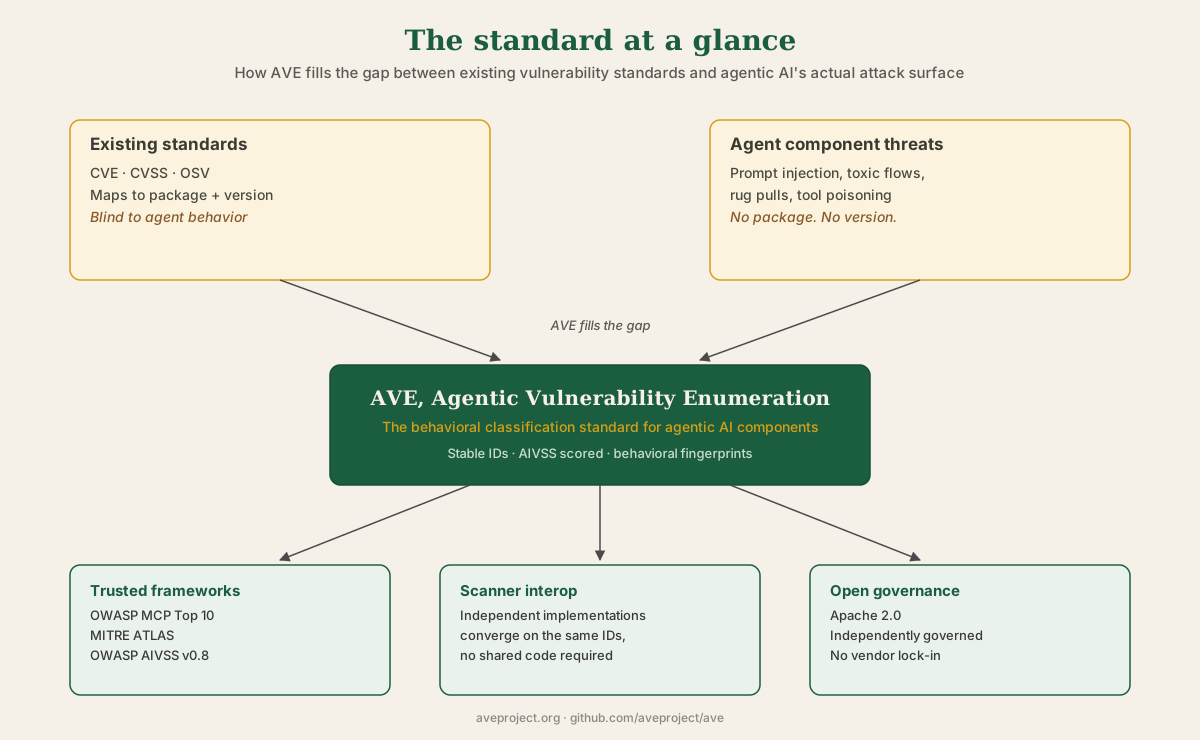
Existing vulnerability standards were built for conventional software.
CVE identifies flaws in a specific product and version. OSV maps them to
package and version ranges. Neither can describe a prompt injection hidden
in an MCP tool description — there is no package, no version, no vulnerable
dependency. The danger is in what the component *does*, not what it imports.
**AVE fills that gap.** It assigns stable identifiers to distinct behavioral
classes in agentic AI, scores them with OWASP AIVSS v0.8, and maps every
record to OWASP MCP Top 10 and MITRE ATLAS so findings land in frameworks
defenders already use.
AVE is a standard, not a product. The `bawbel-scanner` implements it as the
reference implementation. Any tool can map to it — see the
[implementer guide](docs/specs/ave-implementer-guide.md) for how.
### What AVE is not
AVE is a naming and classification standard. It assigns stable IDs to
behavioral vulnerability classes and describes how to detect them. It
is not a runtime enforcement mechanism, and an AVE ID on its own stops
nothing. Enforcement requires a separate policy or gating layer that
consumes AVE's records, the same relationship CWE has to an actual
static analyzer, or a CVE has to a patch management system.
```
Your CI pipeline scans dependencies for known package vulnerabilities.
It does not scan your SKILL.md for prompt injection.
AVE fixes that.
```