ISMS CORE Project

πŸŽ‹ ISMS CORE Project

Compliance Operations, Risk & Evidence β€” ISO 27001 Β· ISO 27701 Β· ISO 27017 Β· ISO 27018 Β· ISO 42001

ISO 27001:2022 ISO 27701:2025 ISO 27018:2025 ISO 27017:2026 ISO 42001:2023 Control Packs Content License Platform License

29 compliance assessment modules β€” click to expand

NIST CSF NIS2 DORA CIS Controls v8 BSI IT-Grundschutz CSRM NCSC CH TISAX Swiss nDSG Swiss ISG EU CRA EU AI Act EU Cloud Sovereignty NIST AI RMF COBIT 2019 CyberFundamentals BE BaFin BAIT CSSF LU ACN IT UK NIS UK Op Resilience NCSC CAF v4.0 ReCyF v2.5 PCI DSS v4.0.1 FINMA NIST SP 800-53 Rev 5 CSA CCM v4.1 CSA AICM v1.1 BSI C5:2026 BSI C3A MITRE ATT&CK Crosswalk Mappings

Grows fast. Bends, doesn't break. Built to last. πŸŽ‹

--- ## 🎯 What is ISMS CORE? ISMS CORE is a production-grade **control engineering** platform for building and operating an information security management system. It treats compliance implementation as an **engineering problem** β€” not a consulting exercise. > **New here?** Read [PARADIGM.md](PARADIGM.md) first β€” it explains how ISMS CORE differs from traditional ISMS approaches, how to choose between products, and what to expect. --- ## Five Products. Four Standards. One Platform.
### πŸ—οΈ [Framework](isms-core-framework/) ISO 27001:2022 **Full SSE engineering product** for mature security teams and consultants. Governance policies, implementation guides, assessment scripts, generated workbooks β€” one complete pack per control. **53** control packs Β· **93** Annex A controls
**376** IMP docs Β· **188** generators
EN Β· FR Β· DE Β· IT Complete
### ⚑ [Operational](isms-core-operational/) ISO 27001:2022 **Foundation ISMS for SMEs** (10–500 people). Operational policies with single-sheet compliance checklists. No engineering overhead β€” read the policy, run the checklist, done. **53** control groups Β· **53** OP-POL docs
**53** checklist generators
EN Β· FR Β· DE Β· IT Complete
### πŸ”’ [Privacy](isms-core-privacy/) ISO 27701:2025 **Privacy information management** β€” controller, processor, and shared control groups for ISO 27701:2025. Pairs with Framework or Operational. **21** control groups Β· **23** PRIV-POL docs
**42** IMP docs Β· **21** generators
EN Β· FR Β· DE Β· IT Complete
### ☁️ [Cloud](isms-core-cloud/) ISO 27018:2025 ISO 27017:2026 **PII protection + cloud security controls** β€” checklists for cloud service providers processing PII (ISO 27018:2025 Annex A) plus 4 standalone cloud security extension controls (ISO 27017:2026), each a standalone standard alongside ISO 27001. **16** control groups Β· **16** POL docs
**32** IMP docs Β· **16** generators
EN Β· FR Β· DE Β· IT Complete
### πŸ€– [AI](isms-core-ai/) ISO 42001:2023 **AI management system** β€” governance policies covering AI development, deployment, impact assessment, responsible use, and third-party AI relationships. **10** AI control groups + 2 foundation policies Β· **12** AI-POL
**20** IMP docs Β· **10** checklist generators
EN Β· FR Β· DE Β· IT Complete
### πŸ–₯️ [Platform](PLATFORM.md) All five standards **Live compliance management system** β€” turns all content products into dashboards, gap tracking, evidence ingestion, risk registers, and audit reports. Docker Compose, 10 services, self-hosted. **46** connectors Β· **29** assessment modules Β· **4,632** crosswalk objects / 60 axes
8 country jurisdictions Β· **21+** threat intelligence sources Live
--- ## πŸ“¦ What You Get β€” Ready to Use This is not a framework reference or a checklist template library. **Every control pack ships production-ready artifacts you open, adapt, and issue.**
Artifact Format What it is Who uses it Products
POL Markdown Governance policy document β€” what the control requires, who owns it, which standards apply. Set your org name, CISO, and effective date. Issue it. ISMS Manager β†’ Board / Staff All five products
IMP-UG Markdown Implementation User Guide β€” how the ISMS Manager implements and operates the control. Roles, process steps, KPIs, review cycles. ISMS Manager Framework Β· Privacy Β· Cloud Β· AI
IMP-TG Markdown Implementation Technical Guide β€” step-by-step for the engineer. Commands, config snippets, vendor-specific notes, hardening checklists. Security Engineer Framework Β· Privacy Β· Cloud Β· AI
SCR Python 3.11+ Assessment generator β€” run python3 generate_*.py to produce a structured, formatted compliance evidence workbook. Single dependency: openpyxl. ISMS Manager β†’ Auditor All five products
WKBK Excel (.xlsx) Generated compliance workbook β€” per-control assessment items, evidence status, scoring, and auditor notes. Output of the SCR generator. Hand directly to your auditor. Auditor / Control Owner All five products
REF Markdown Reference extracts from the ISO standard text mapped to this control. Cross-references to adjacent and related Annex A controls. ISMS Manager / Auditor Framework
CTX Markdown Context document linking this control pack to adjacent and dependent control packs β€” for control stacking and dependency mapping. ISMS Manager Framework
FORM Markdown Ready-to-use templates: evidence collection forms, meeting agendas, approval records, risk acceptance forms. ISMS Manager / Control Owner Framework
> **Example workflow β€” A.8.24 Use of Cryptography:** > 1. Open `POL/` β†’ your organisation's cryptography policy, ready to sign and issue > 2. Open `IMP/` β†’ the `…-UG` file: how to run a key management programme (KPIs, review cycle, ownership) > 3. Open `IMP/` β†’ the `…-TG` file: TLS config, certificate lifecycle, HSM setup, vendor notes > 4. Run `SCR/generate_a824_*.py` β†’ produces `.xlsx` assessment workbook > 5. Hand the workbook to your auditor as structured compliance evidence **Prerequisites for generators:** Python 3.11+, `pip install openpyxl` --- ## 🧭 Who This Is For (and Not For) **This is for:** - Security teams building an ISMS wanting **repeatable, auditable evidence** - Engineers who prefer **automation + tests** over "security theater" - SMEs needing **practical, audit-ready policies** without over-engineering - Organisations processing PII needing **ISO 27701 controller/processor controls** - Cloud service providers needing **ISO 27018 PII compliance** or **ISO 27017 cloud security controls** - Organisations developing AI systems needing **ISO 42001 AIMS governance** - Consultants and auditors needing **structured, traceable control packs** **This is not for:** - "One-click compliance" expectations - Legal interpretations of GDPR/DORA/NIS2 (use counsel) - Running scripts you haven't reviewed (treat this like code) --- ## πŸš€ Quick Start **Prerequisites:** Python 3.11+, `pip install openpyxl` ### Framework β€” ISO 27001:2022 Full Engineering ```bash # Browse the 53 control packs cat isms-core-framework/CONTROLS.md # Navigate to a control, read POL β†’ IMP-UG β†’ IMP-TG, then generate the workbook cd isms-core-framework/A.8-technological-controls/isms-a.8.24-use-of-cryptography/SCR python3 generate_a824_1_data_transmission_assessment.py ``` ### Operational β€” ISO 27001:2022 SME Edition ```bash cd isms-core-operational/A.5-organisational-controls/isms-a.5.1-2-6.1-2-secure-employment-and-roles/SCR python3 generate_op_checklist_a512612.py ``` ### Privacy β€” ISO 27701:2025 ```bash cd isms-core-privacy/privacy-controller/priv-a.1.2.2-5-lawful-basis-and-consent/SCR python3 generate_priv_checklist_a1225.py ``` ### Cloud PII β€” ISO 27018:2025 ```bash cd isms-core-cloud/iso27018-pii-cloud/cld-a.11-information-security/SCR python3 generate_cld_pii_checklist_a11.py ``` ### Cloud Sec β€” ISO 27017:2026 ```bash cd isms-core-cloud/iso27017-sec-cloud/cld-sec-a.5.38-shared-roles-responsibilities/SCR python3 generate_cld_sec_checklist_a538.py ``` ### AI β€” ISO 42001:2023 ```bash # Start with the AI governance foundation policy (available in EN, FR, DE, IT) cat "isms-core-ai/00-ai-foundation-policies/ai-pol-01-aims-governance-and-decision-making/POL/AI-POL-01 - AIMS Governance and Decision-Making Framework.md" ``` ### Platform β€” Live Compliance Dashboard ```bash cd isms-core-platform cp .env.example .env # Fill in HOST_IP, passwords, ADMIN_PASSWORD docker compose up -d # COMPOSE_PROFILES=opensearch-single is set in .env.example bash bootstrap.sh # One-shot: seeds all control groups, imports all content # β†’ Open https://{HOST_IP} ``` Read [PLATFORM.md](PLATFORM.md) for the full deployment guide, TLS options, connector setup, and Go-Live Checklist. --- ## πŸ“Έ Platform Screenshots
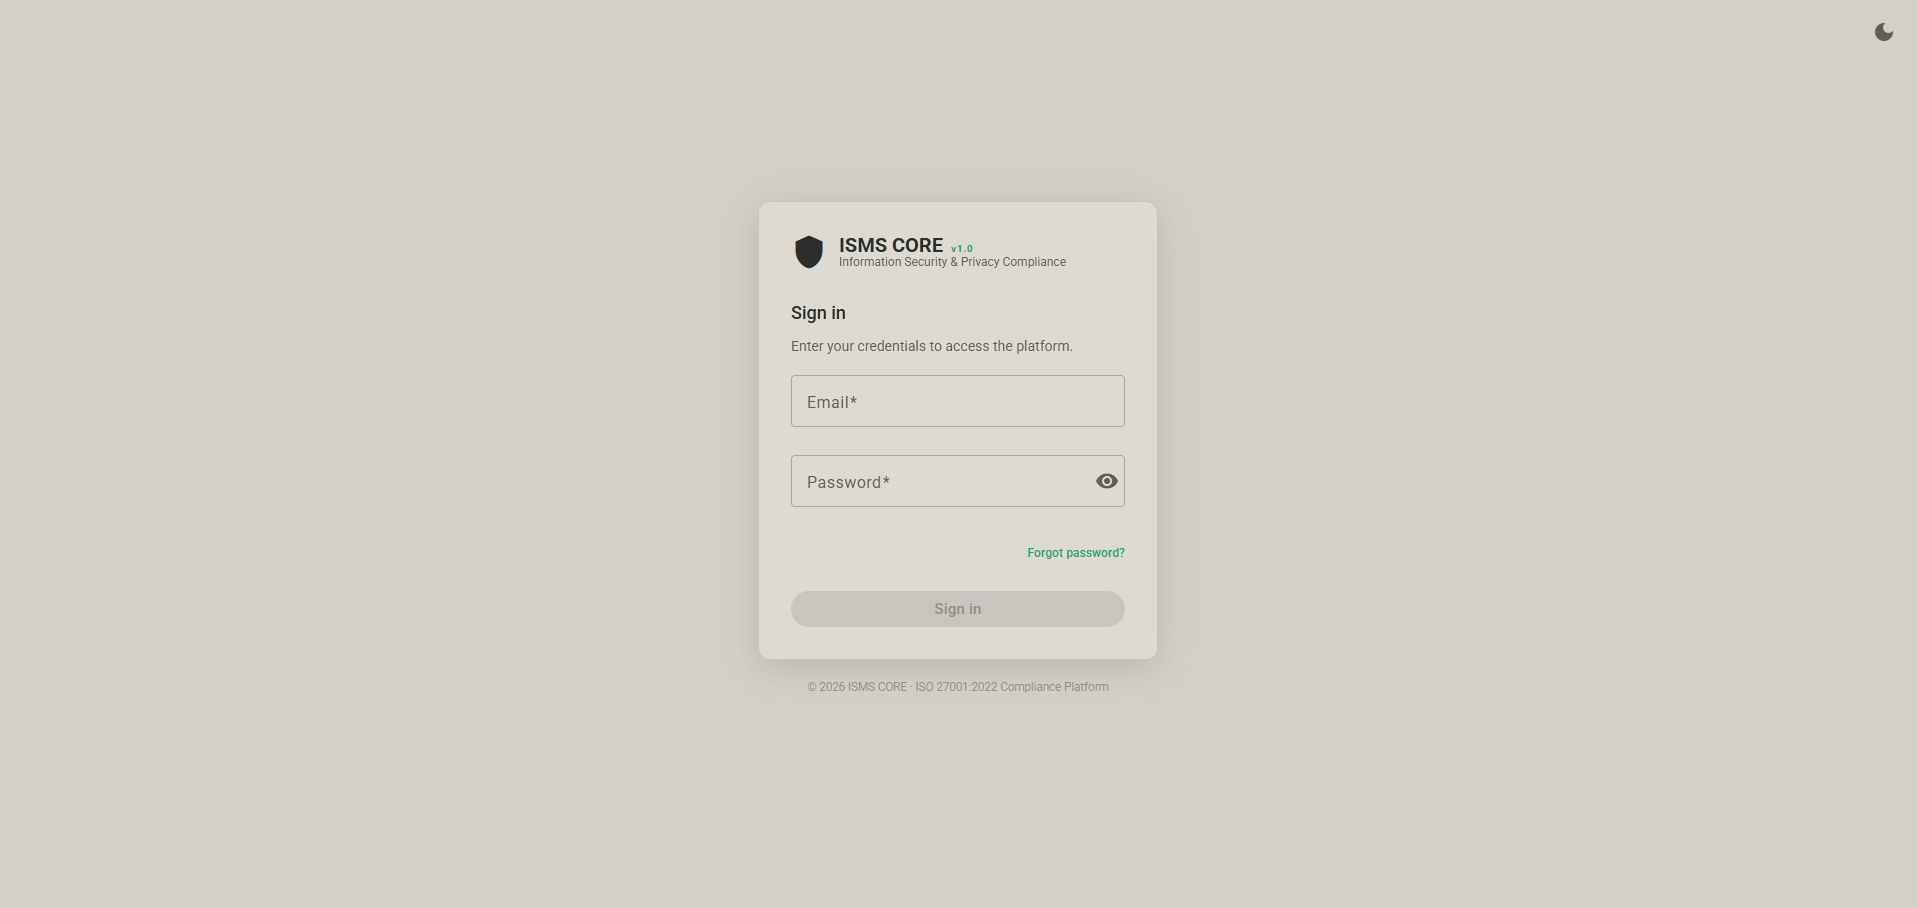
Login
Login screen
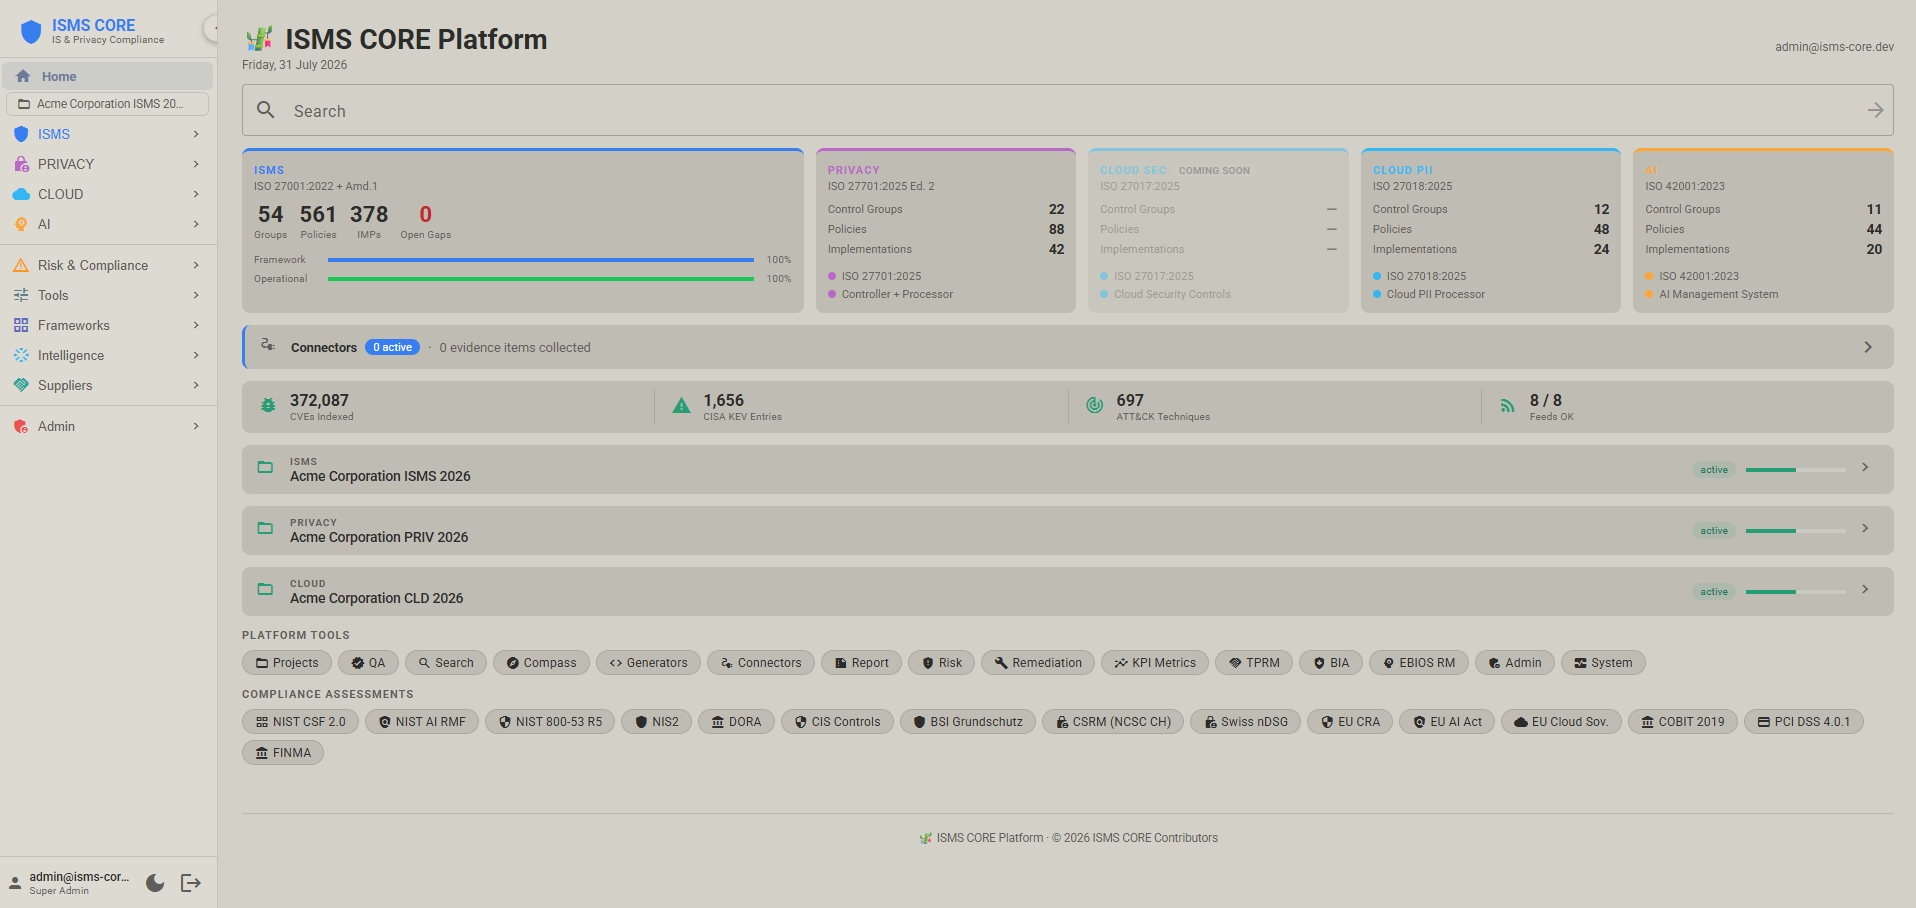
Home Dashboard
Home dashboard β€” ISMS + Privacy + Cloud + AI product switcher with compliance quick-access row
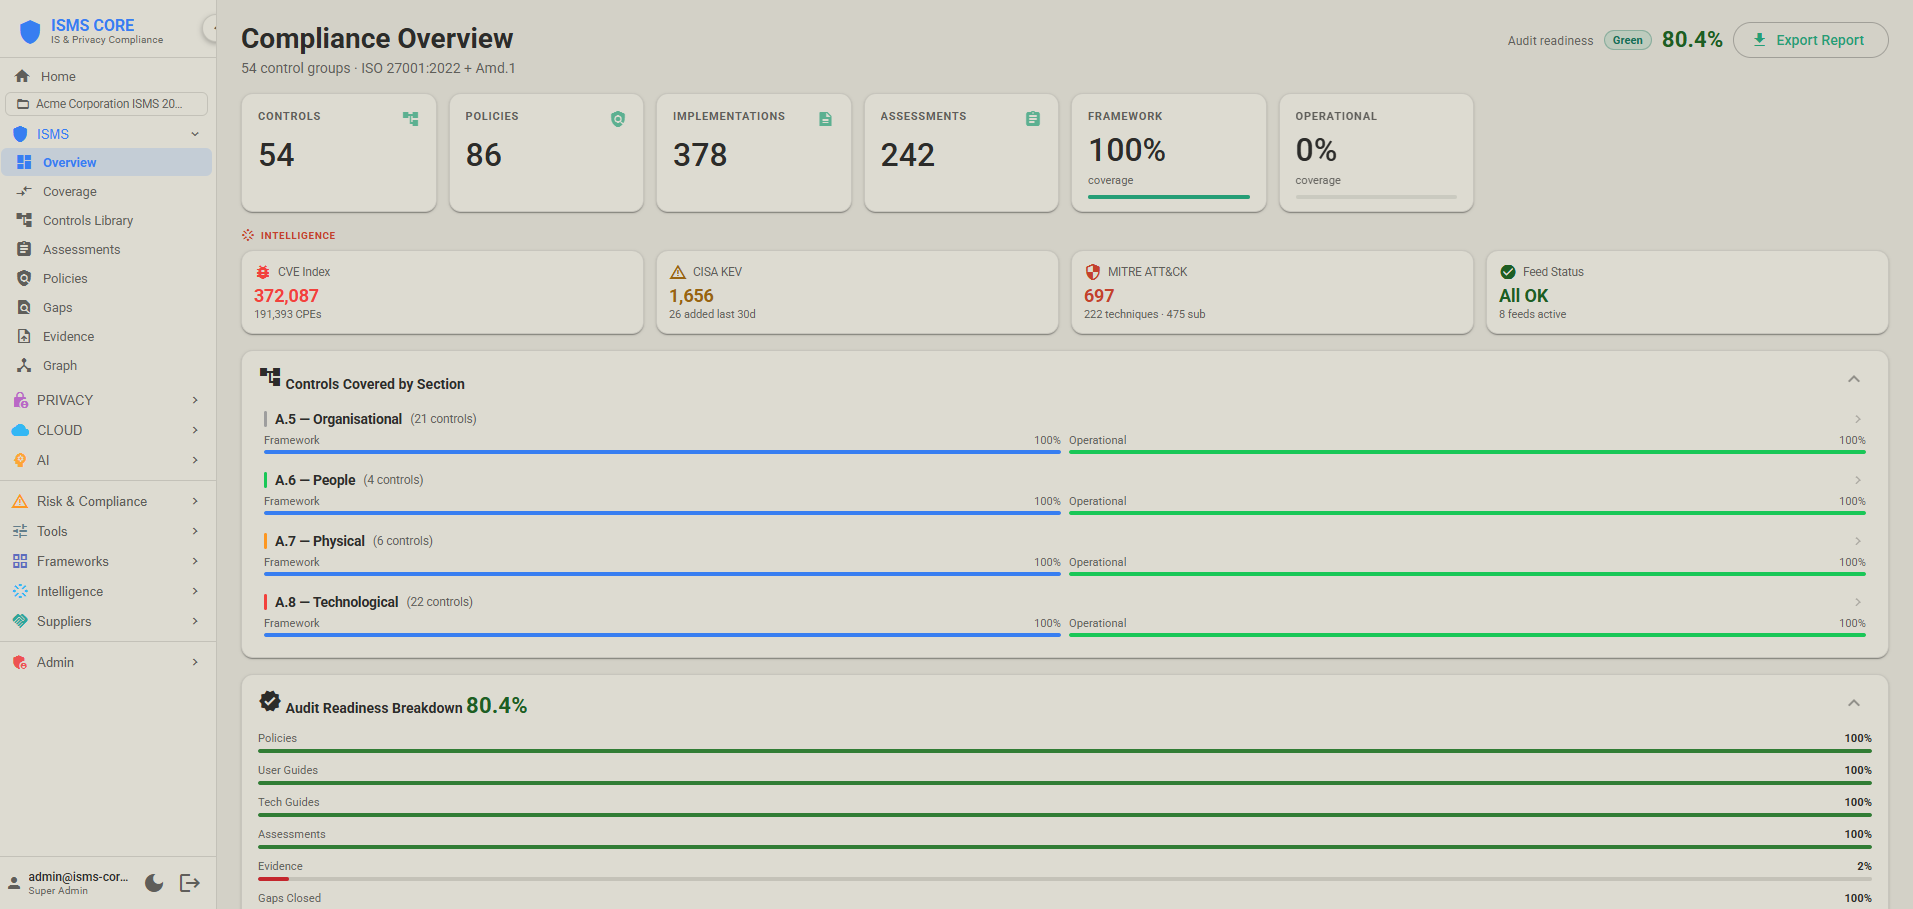
Compliance Overview
Compliance overview β€” 53 control groups, 100% coverage, audit readiness
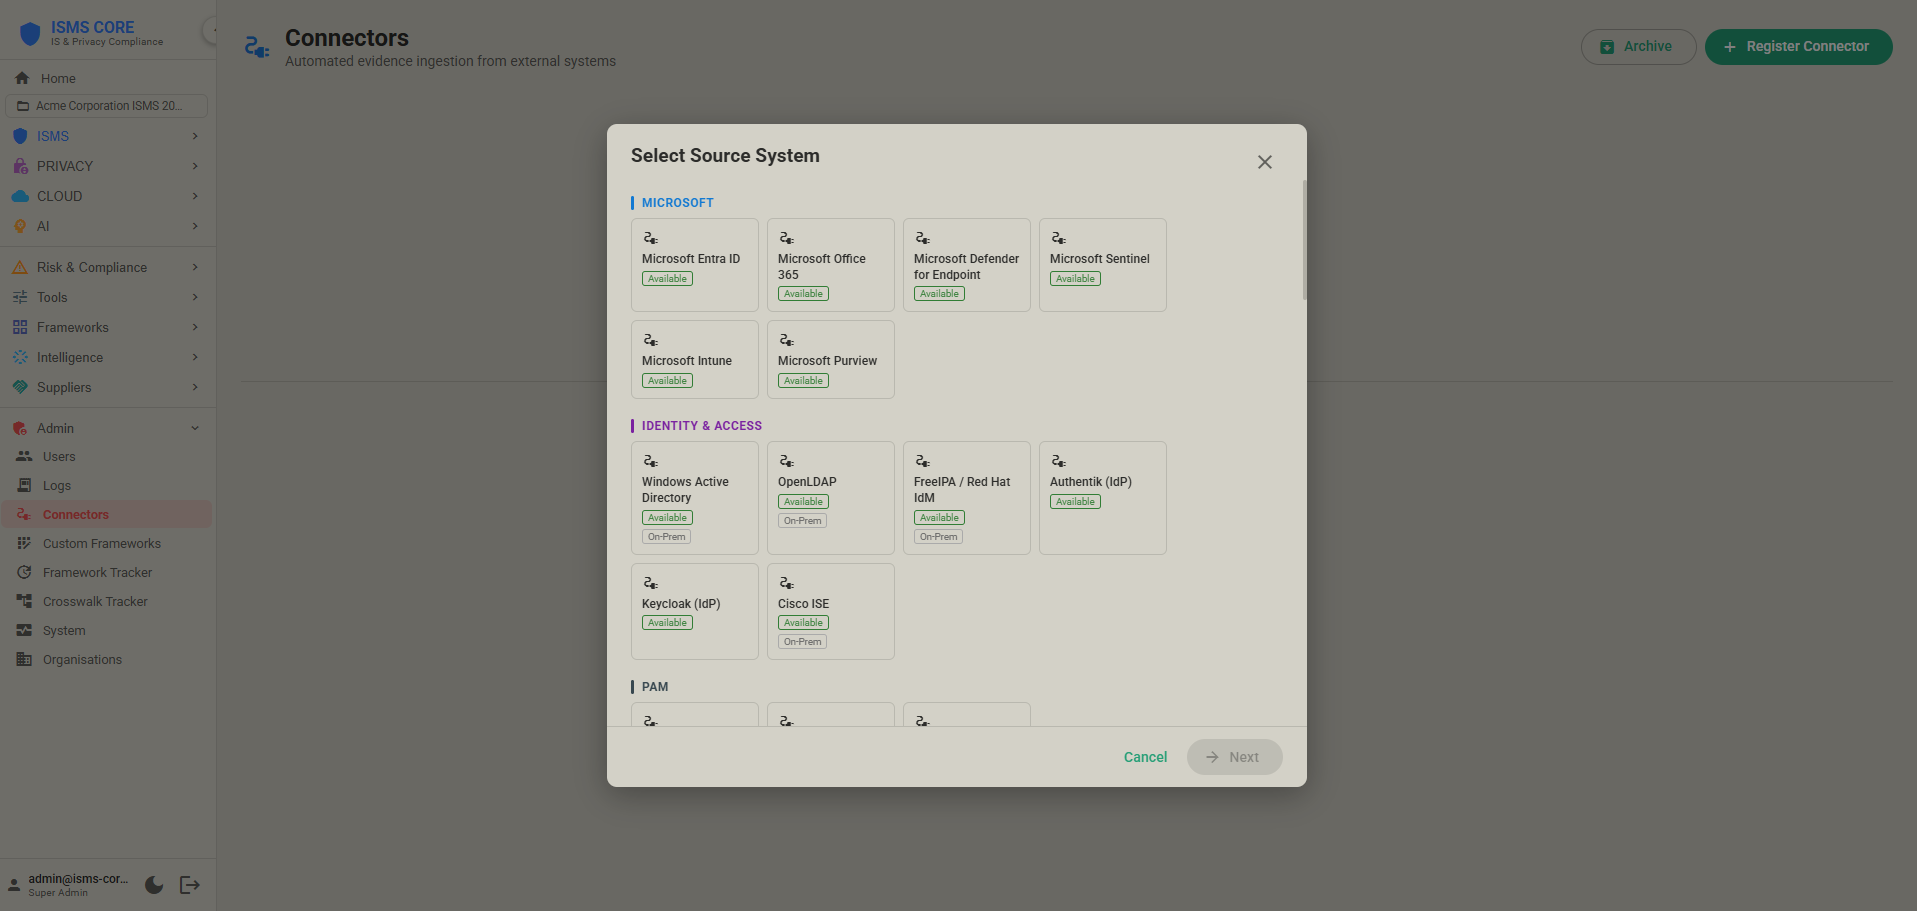
Connectors β€” Automated Evidence
Automated evidence connectors β€” MS Entra ID, Defender, M365, Azure CSPM
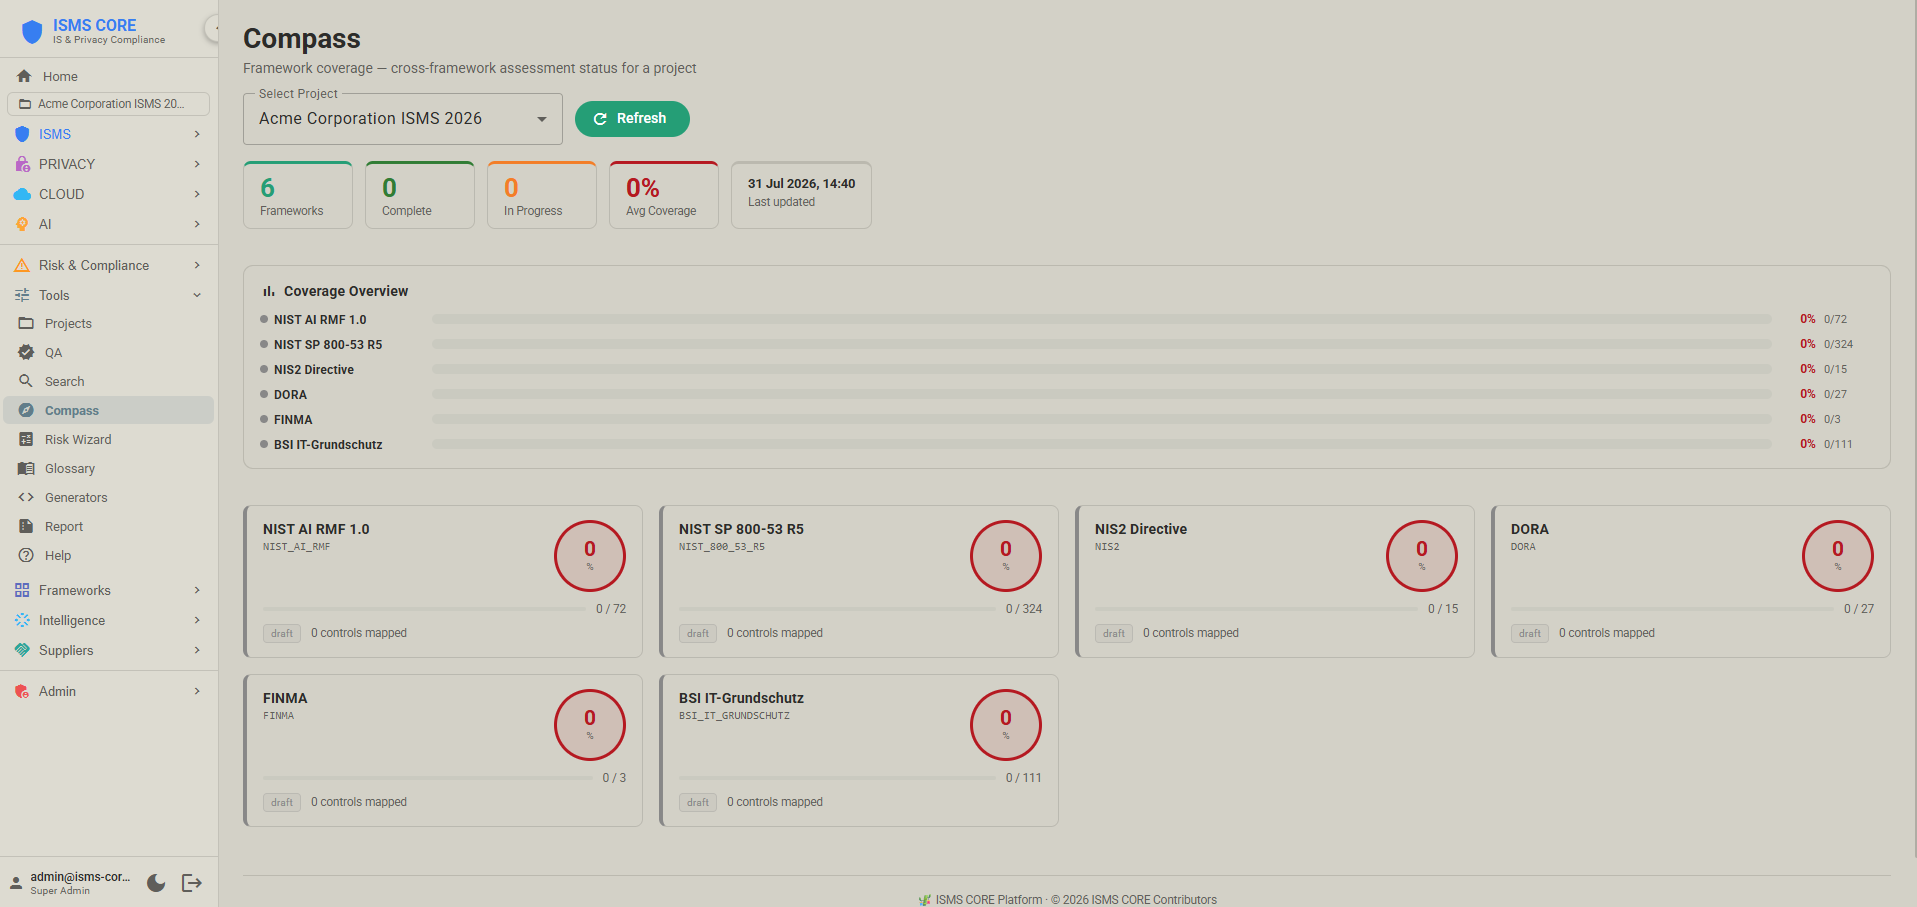
ISMS Compass (AI Gap Analysis)
ISMS Compass β€” AI-powered gap analysis against Gold Standard
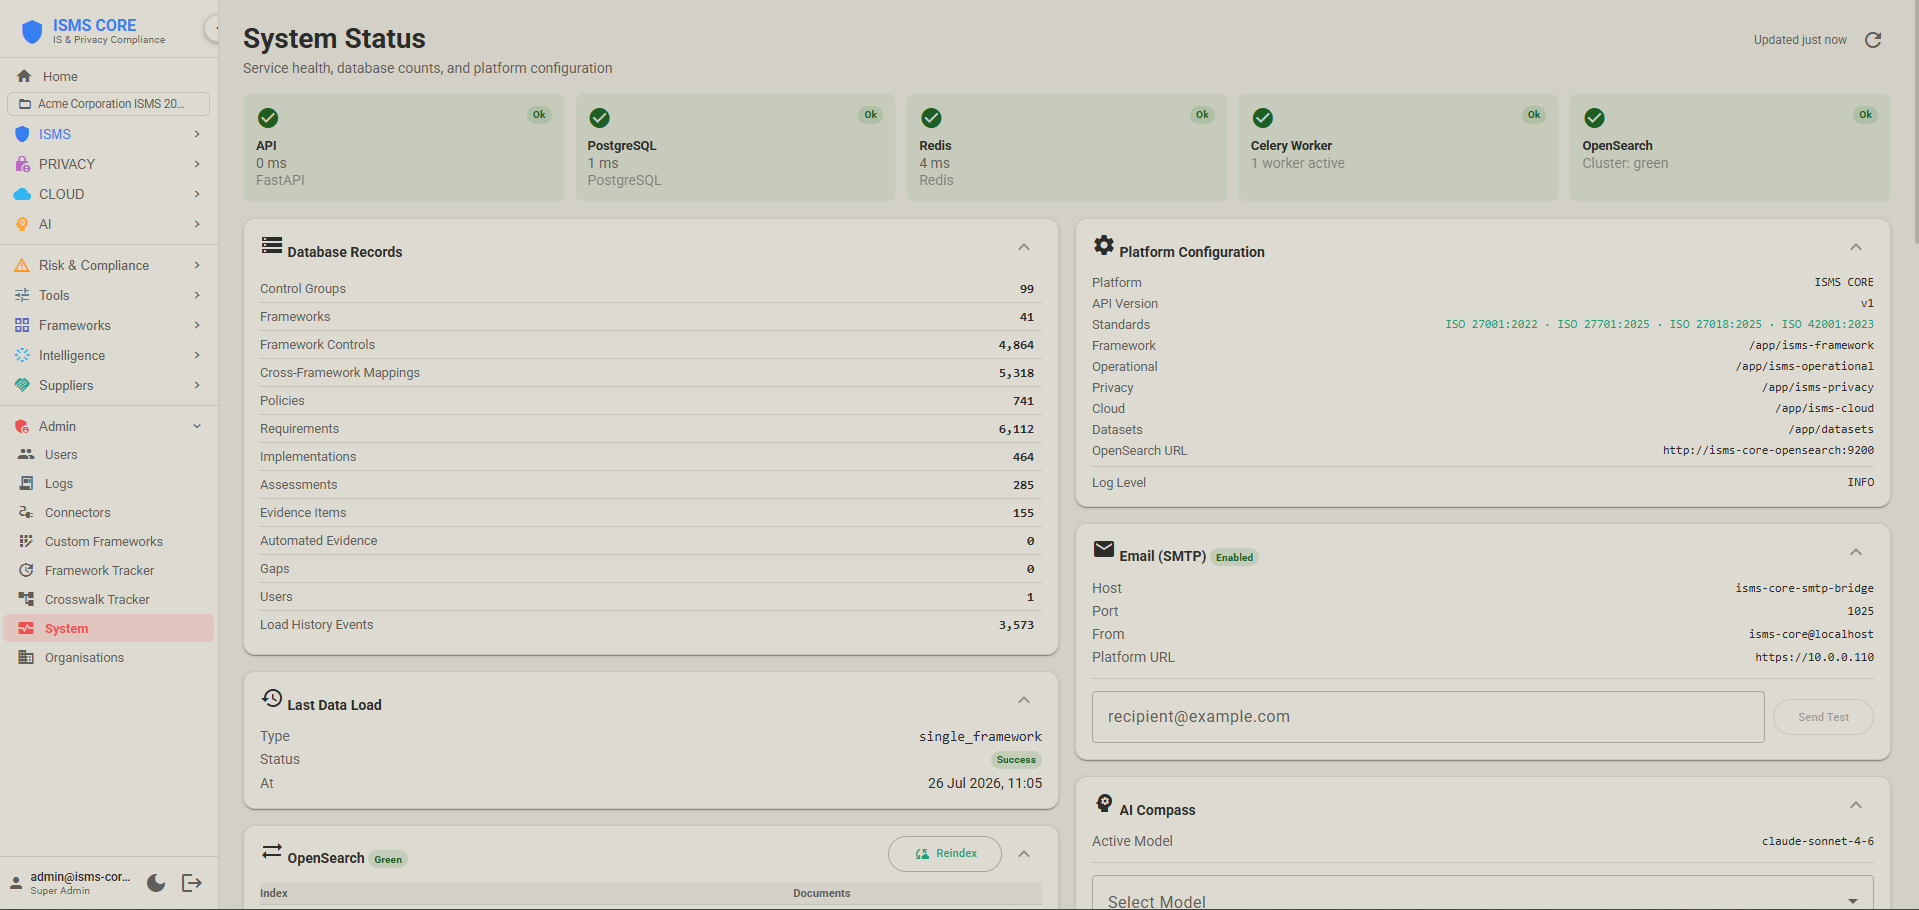
System Status
System status β€” all services healthy, OpenSearch green, Celery active
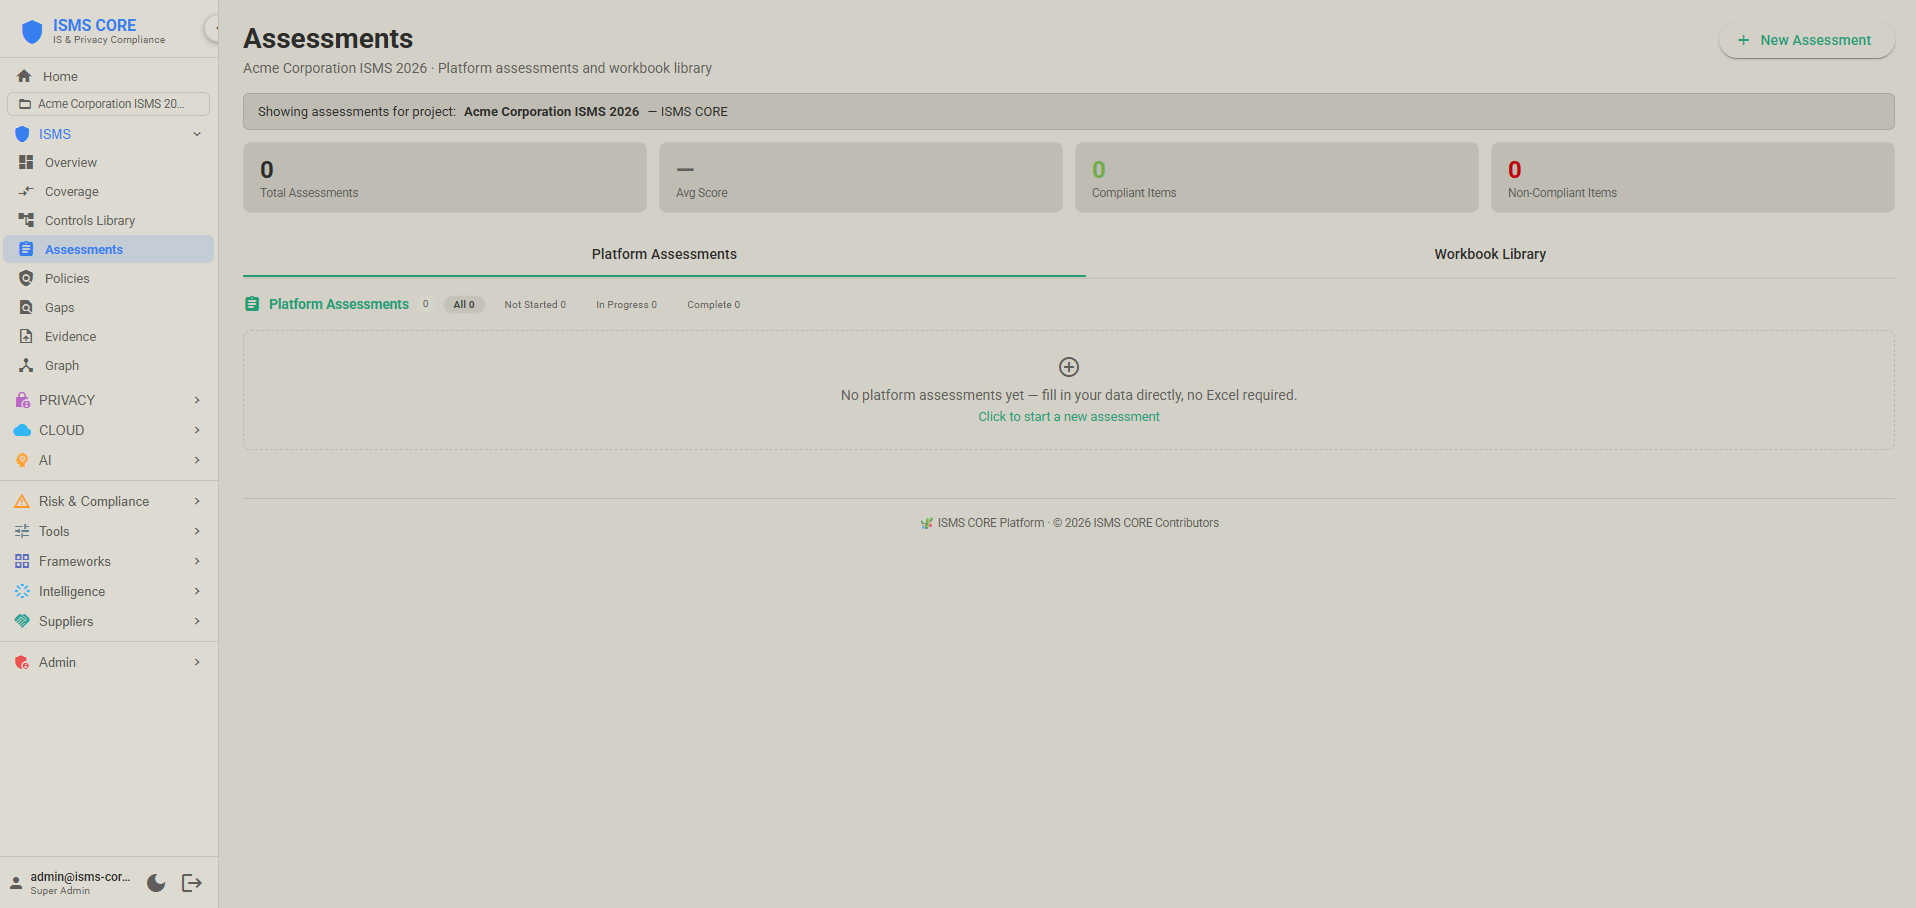
Assessments & Collections
Platform assessments with collections β€” grouped scoring, CSV/XLSX/PDF export
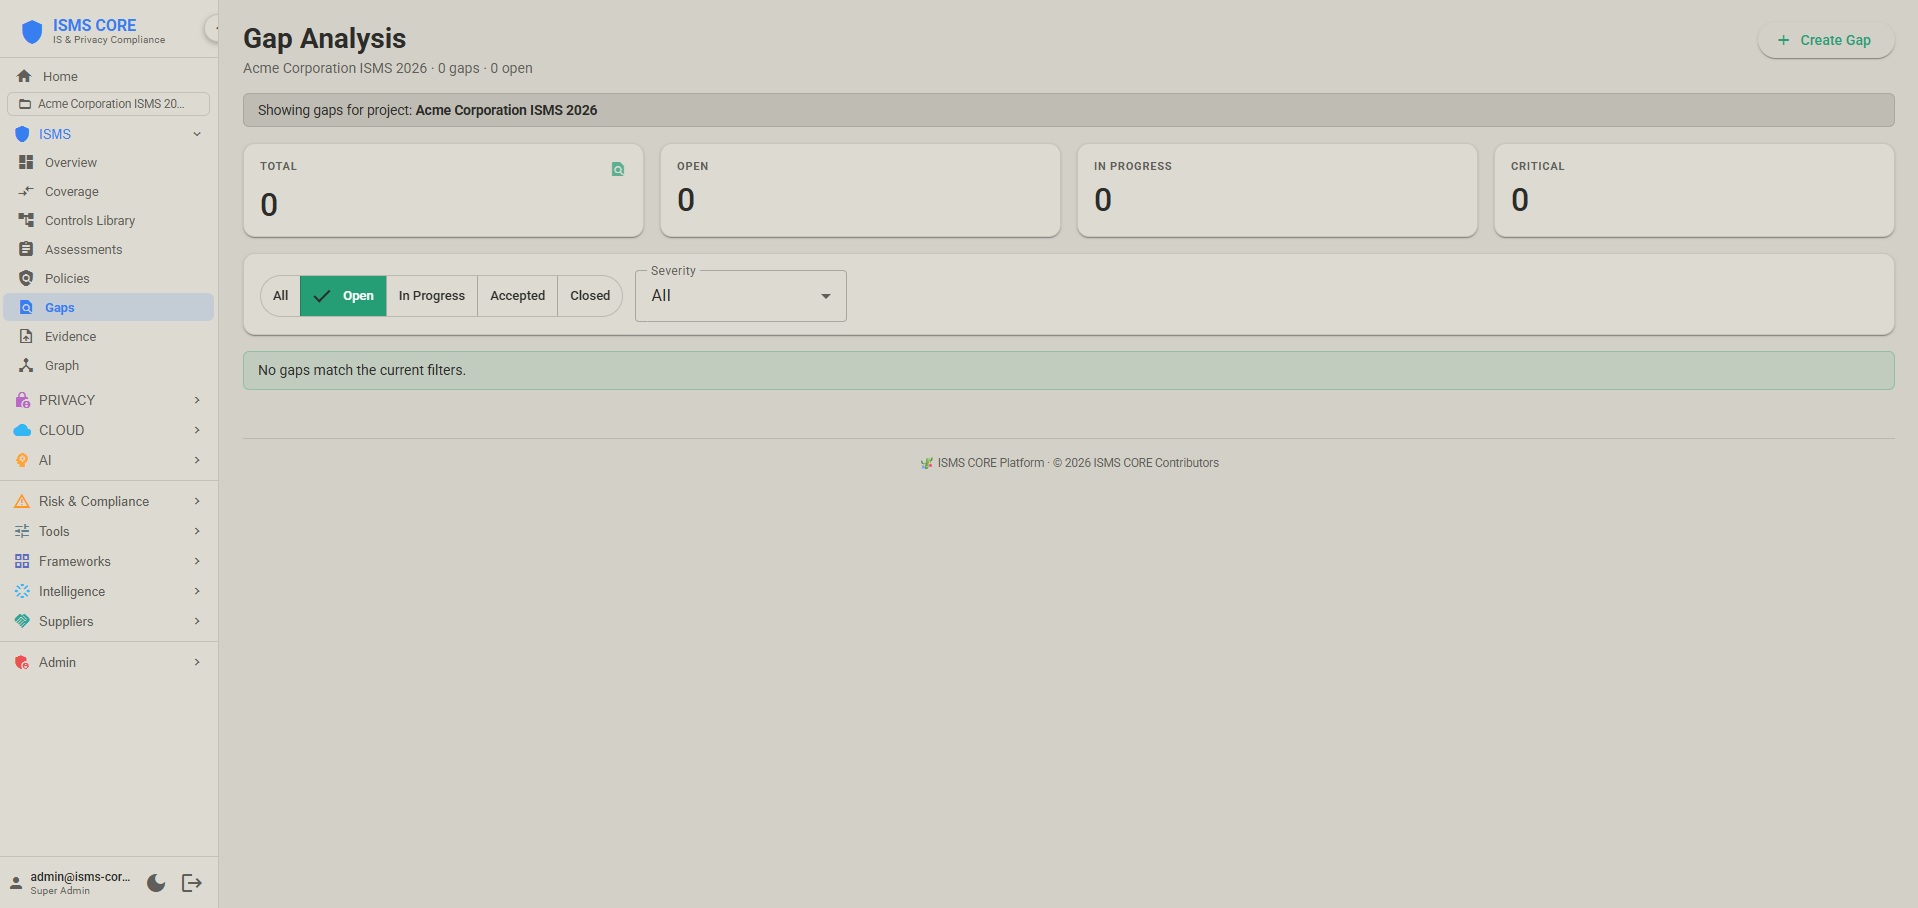
Gap Register
Gap register with BSI 200-3 risk scoring β€” likelihood, impact, risk level
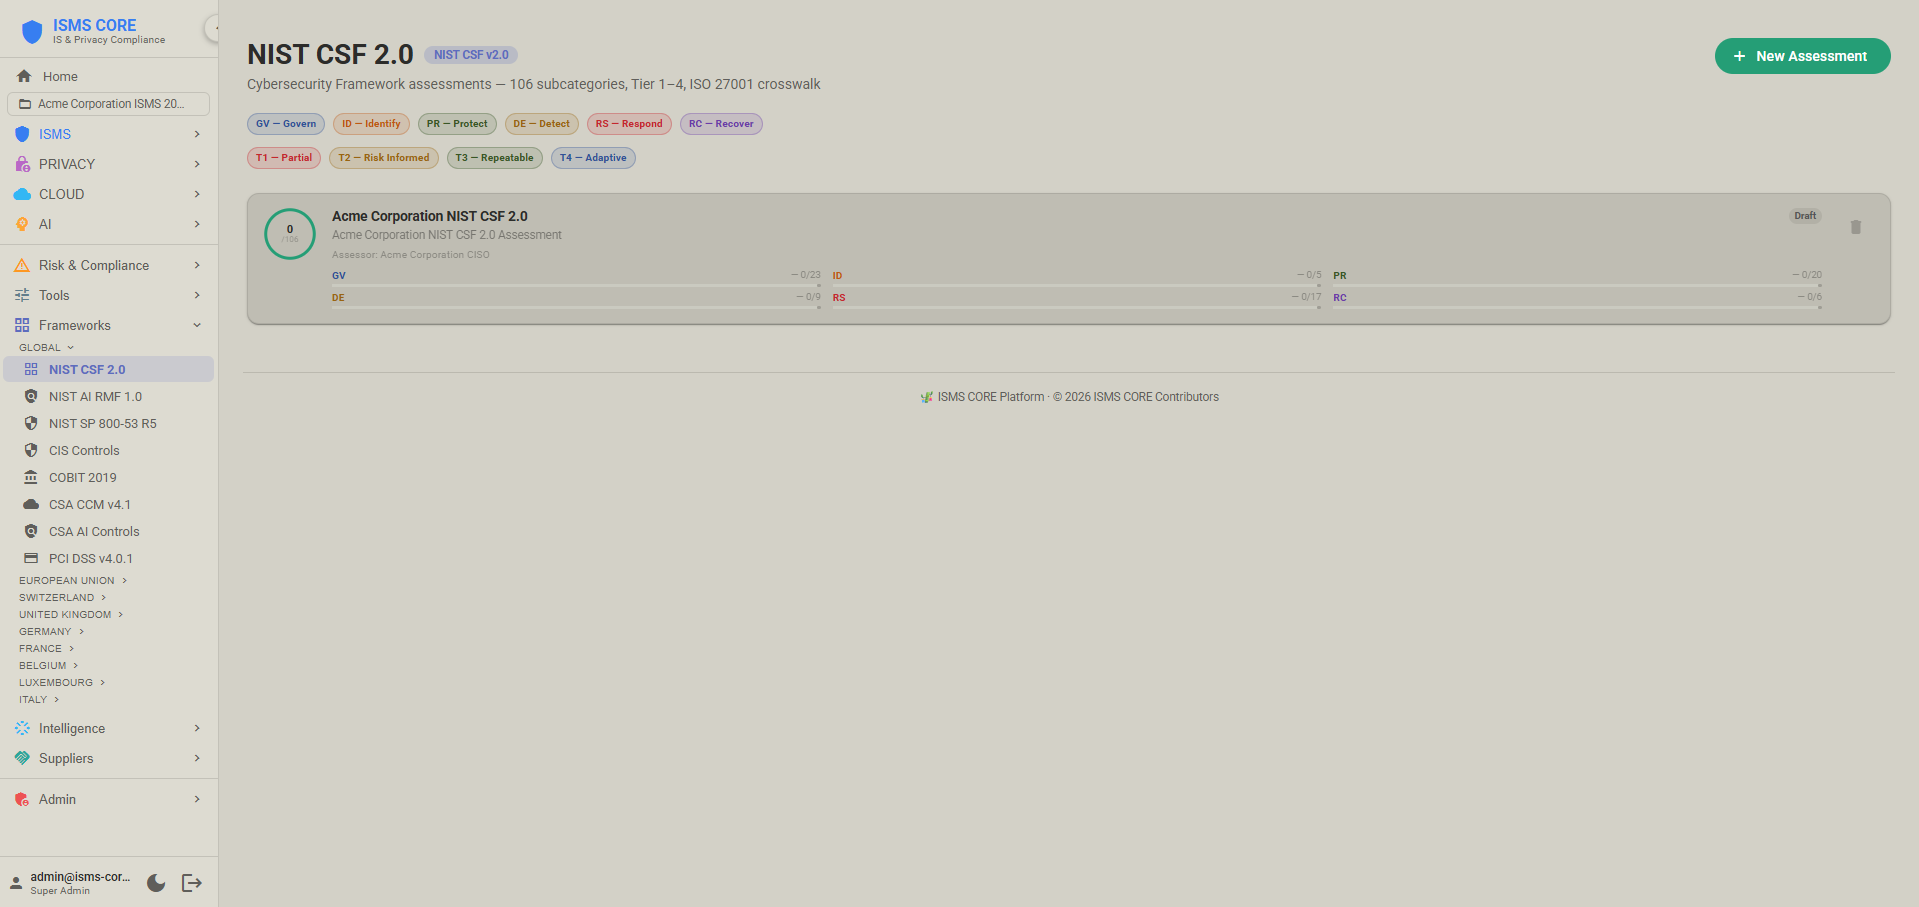
NIST CSF 2.0 Assessment
NIST CSF 2.0 β€” 106 subcategory assessment with tier ratings, function breakdown, and gap analysis
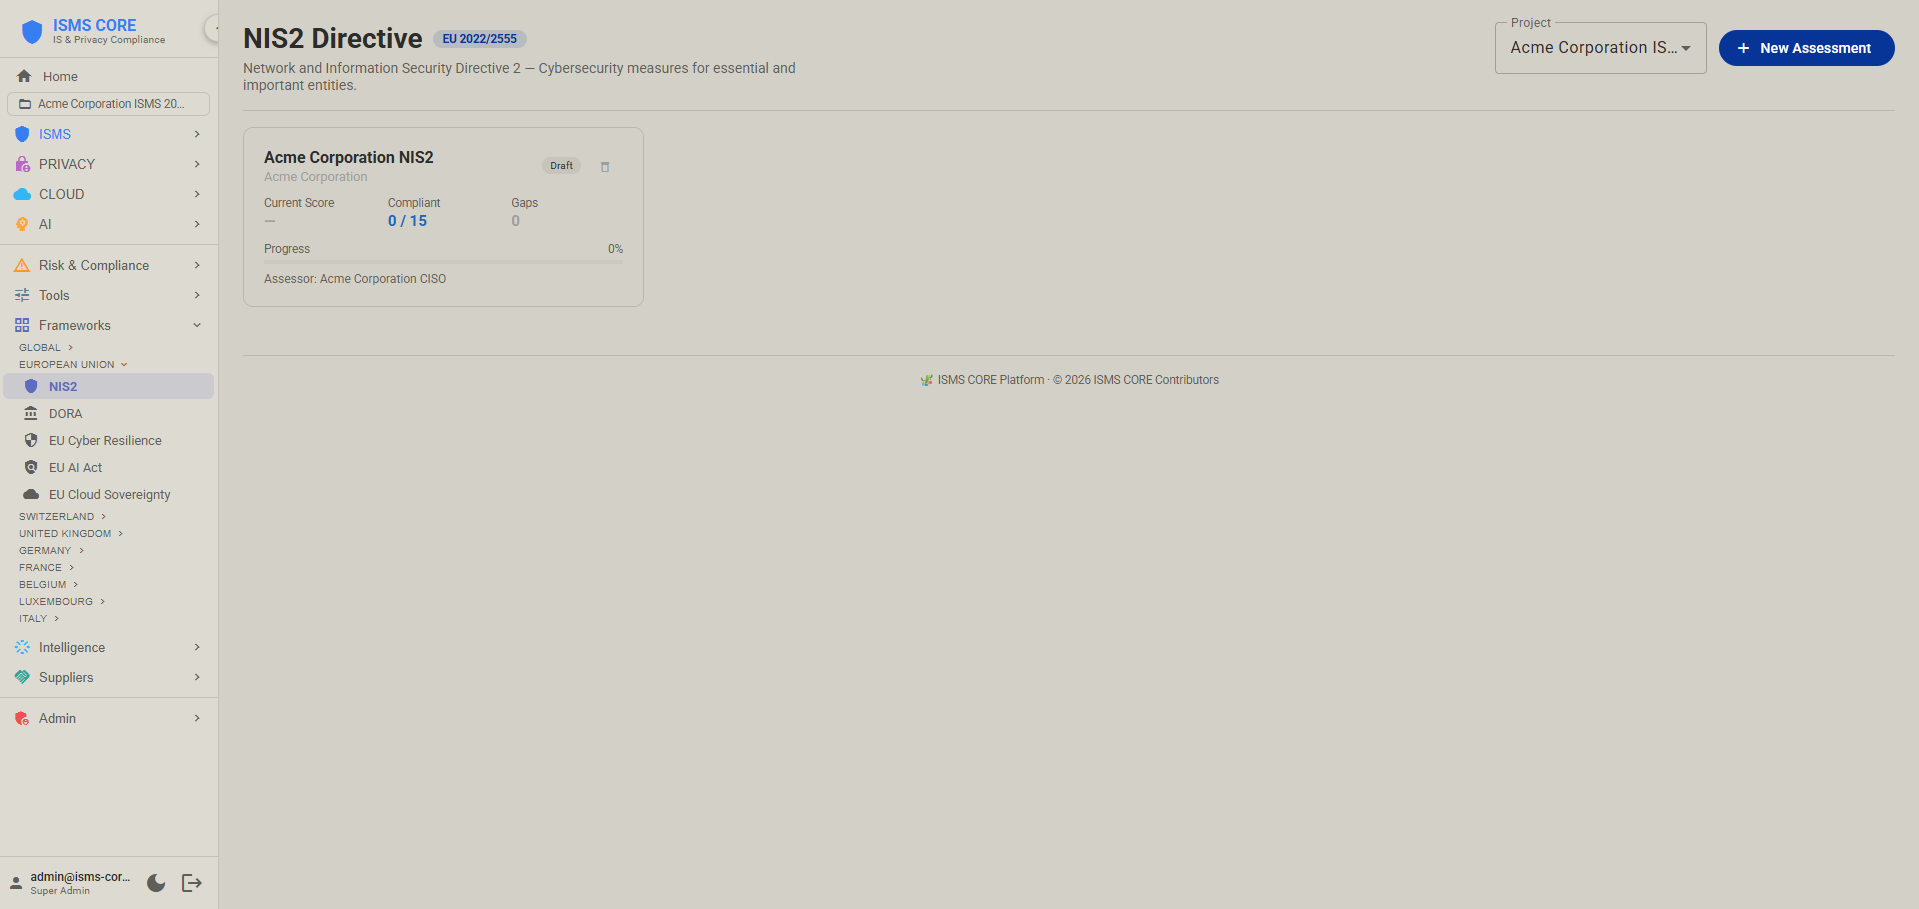
NIS2 Assessment
NIS2 Directive (EU 2022/2555) β€” Article 21 security measures and Article 23 reporting obligations
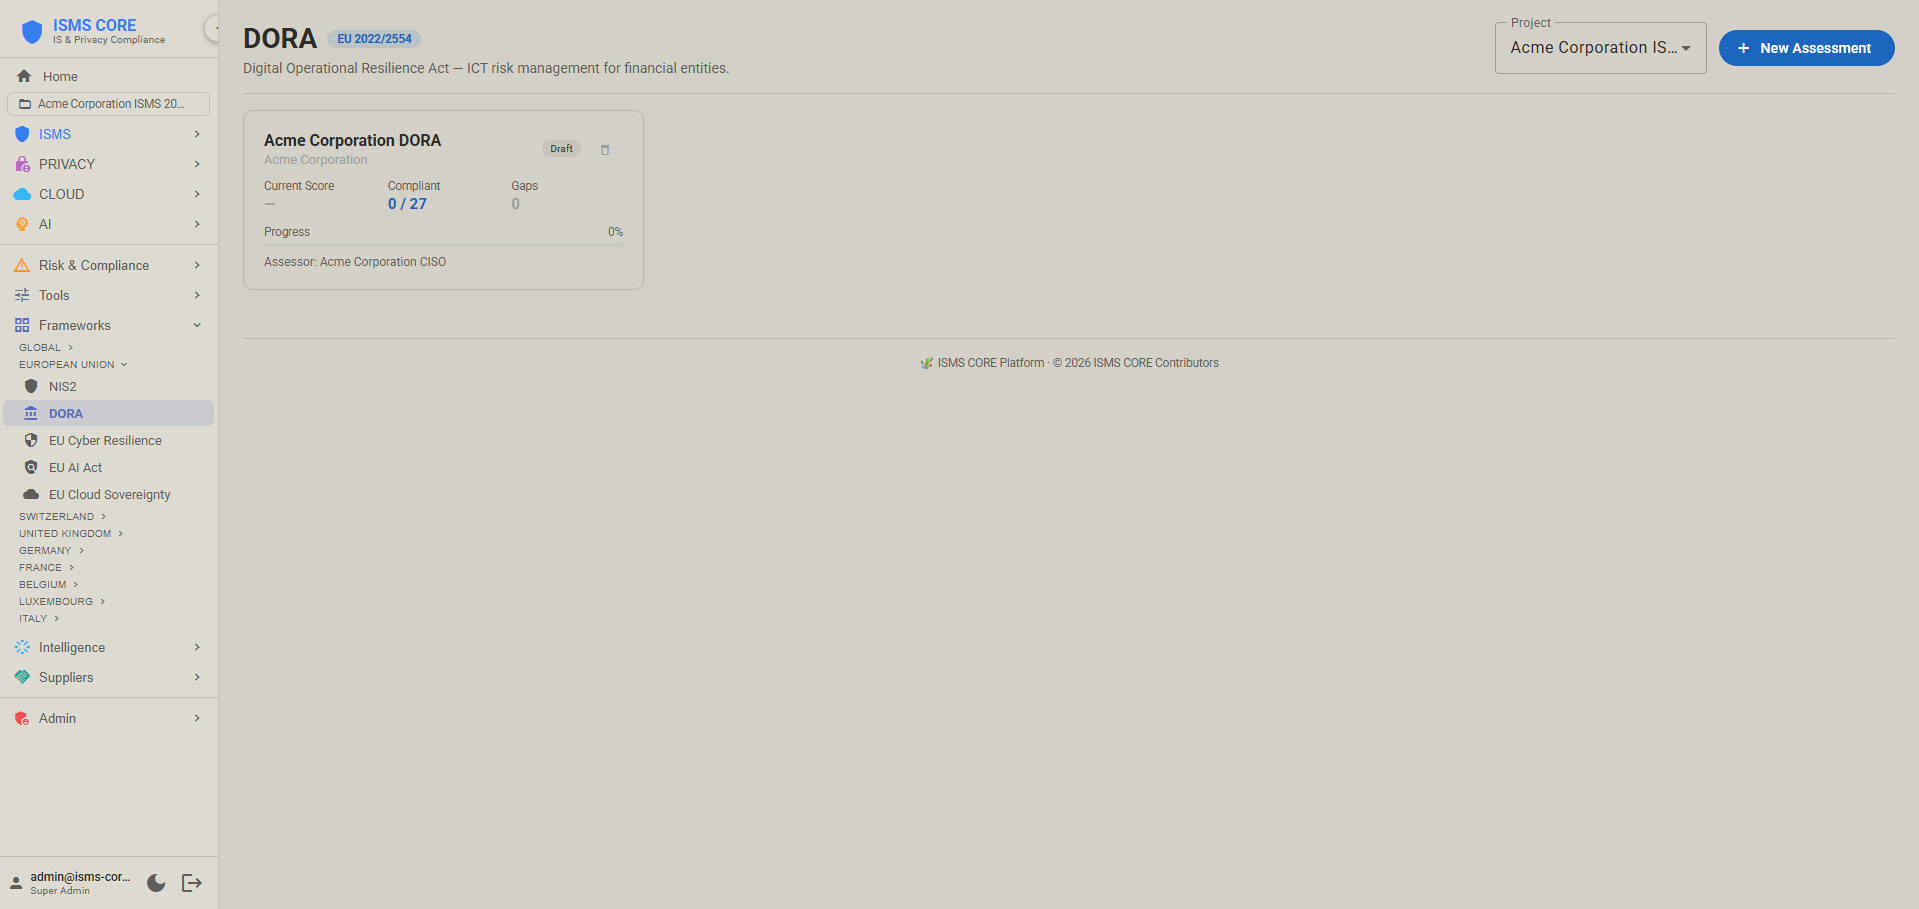
DORA Assessment
DORA (EU 2022/2554) β€” 27 articles across 5 pillars, ICT risk maturity scoring 0–4
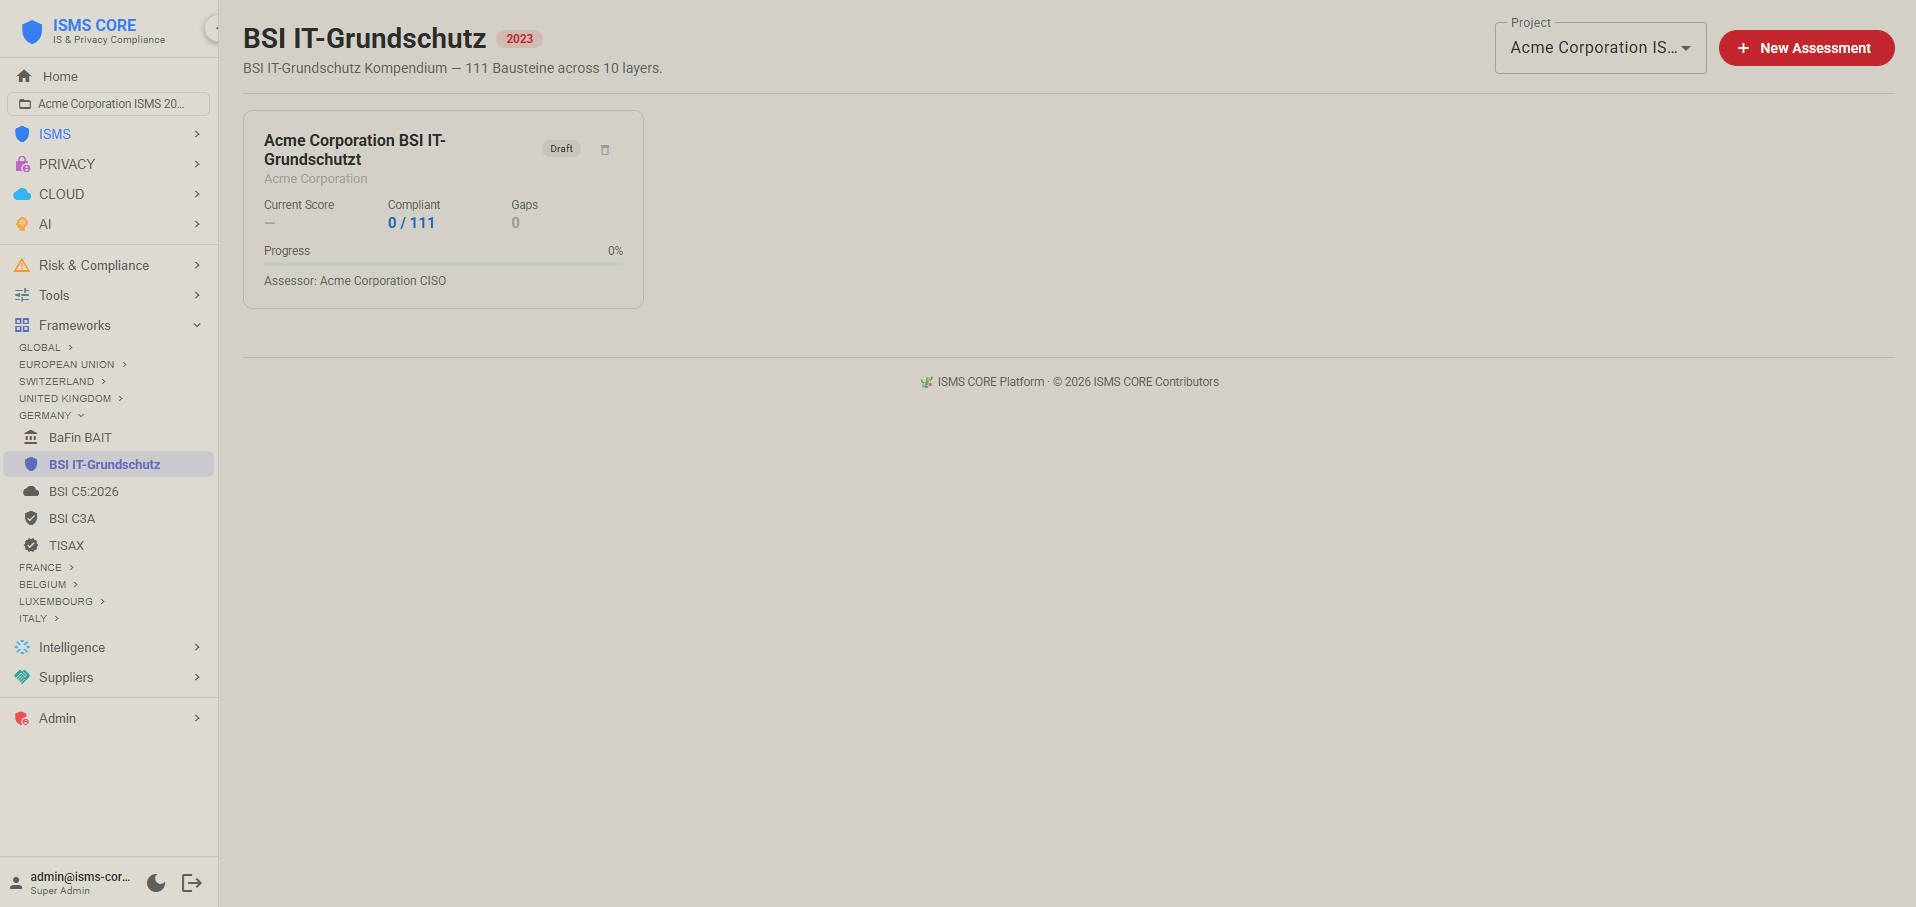
BSI IT-Grundschutz Assessment
BSI IT-Grundschutz Kompendium β€” all 111 building blocks mapped to ISO 27001:2022
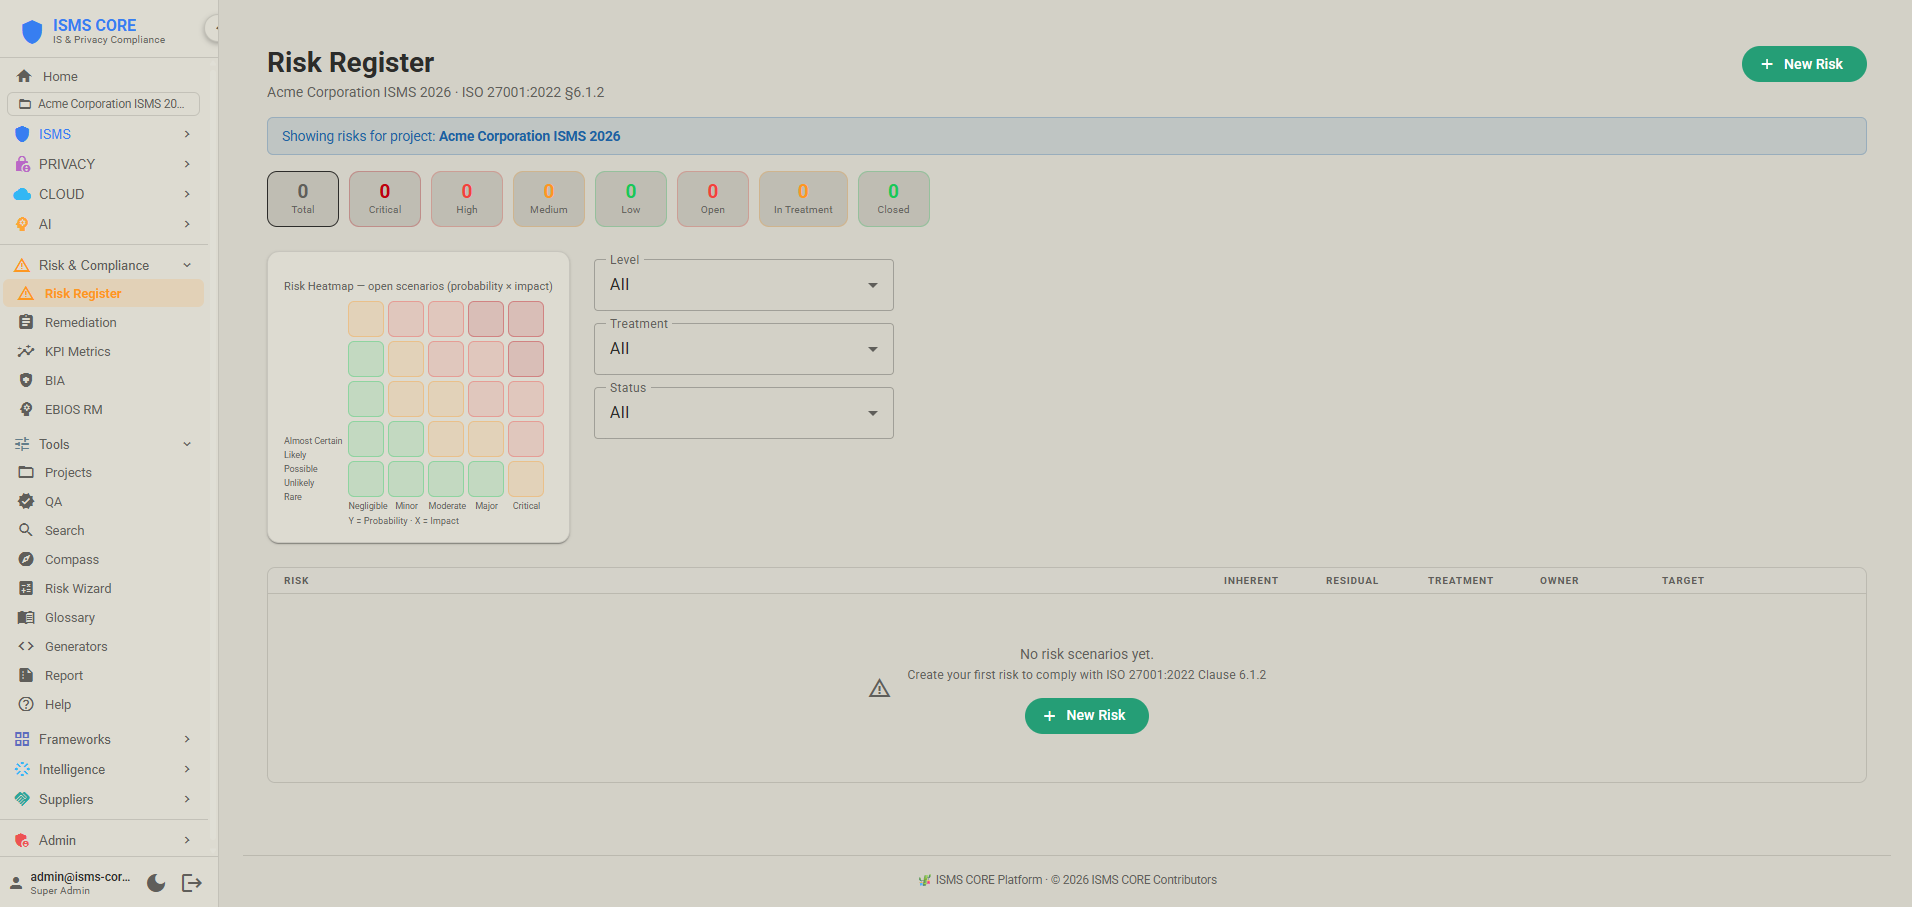
Risk Register & Heatmap
Risk Register β€” 5Γ—5 probability/impact matrix, risk heatmap, treatment workflow
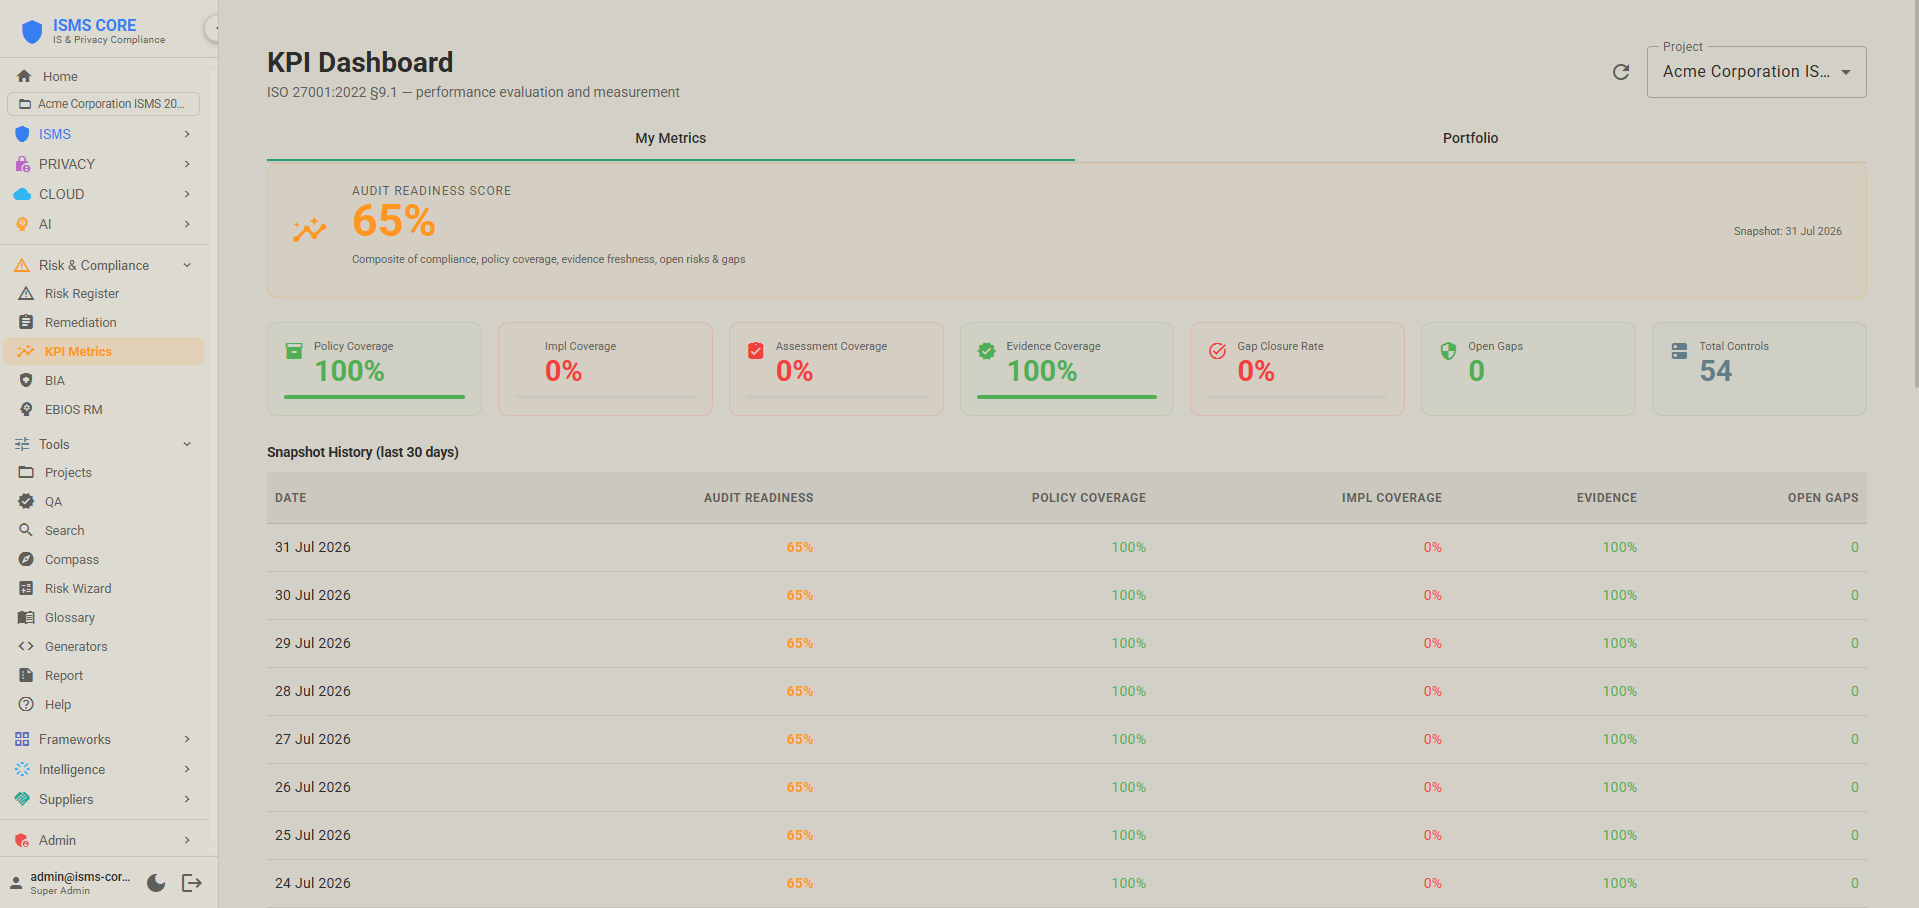
KPI Metrics & Audit Readiness
KPI dashboard β€” 9 named metrics, sparkline trends, Audit Readiness hero score
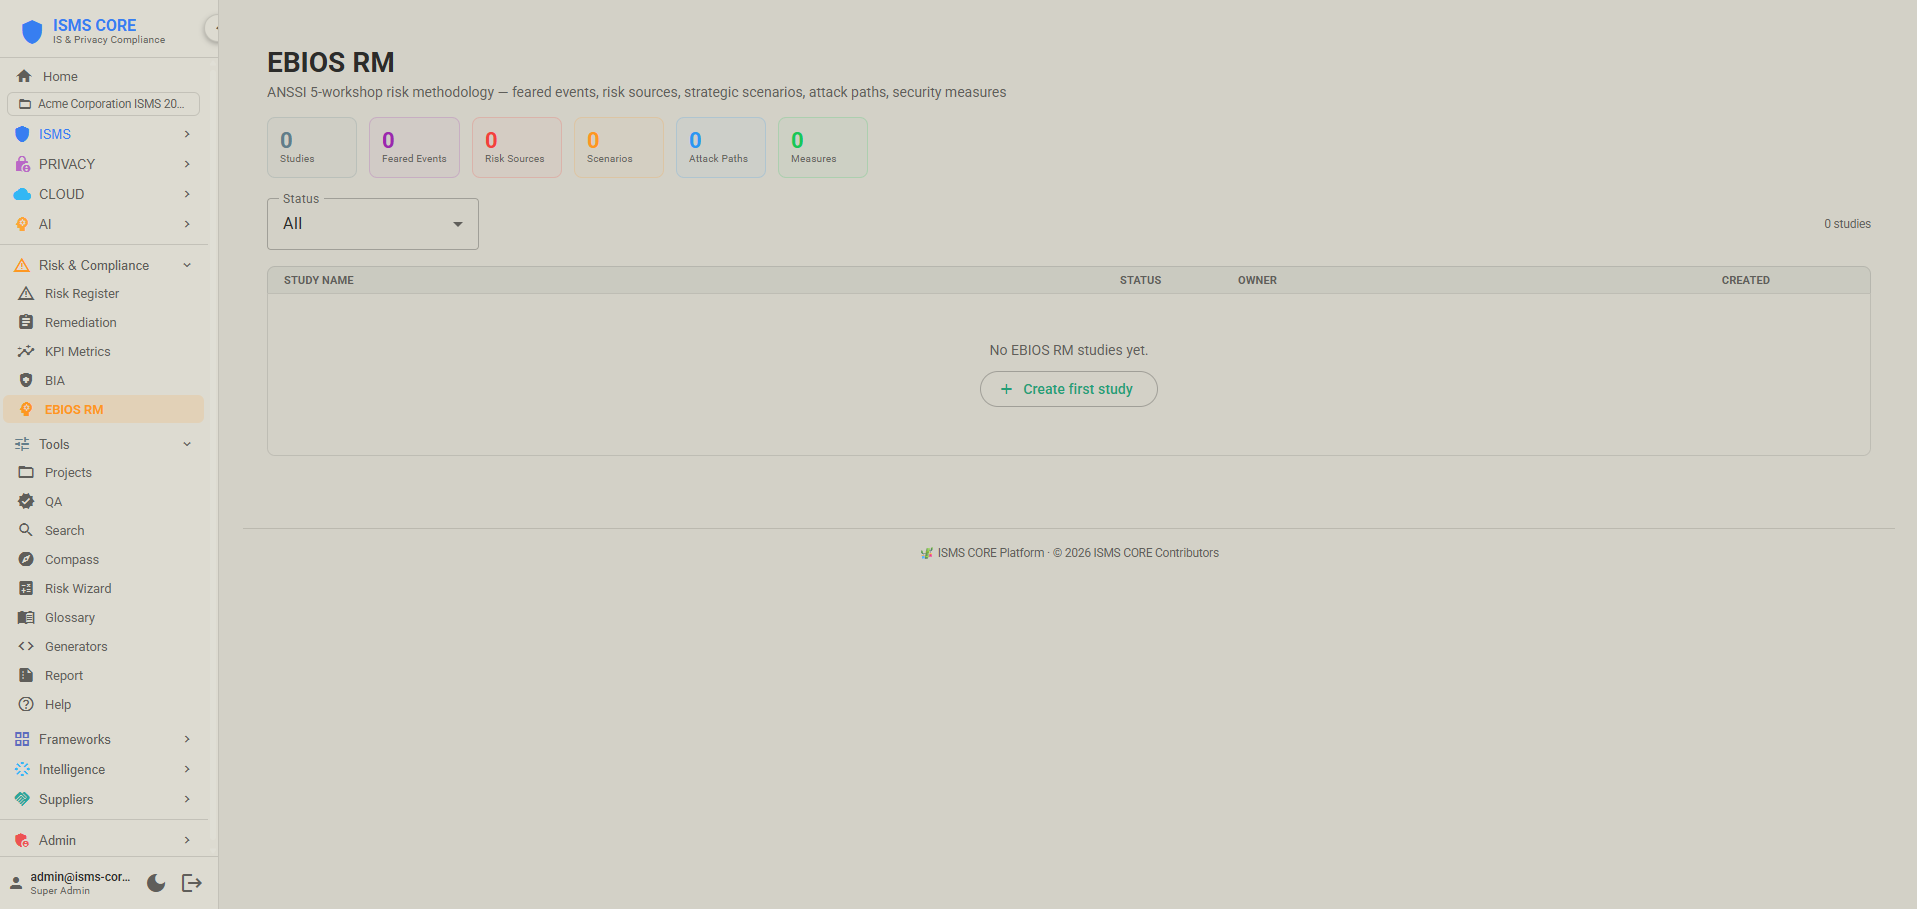
EBIOS RM
EBIOS RM β€” 5-workshop ANSSI methodology, feared events, MITRE ATT&CK attack paths
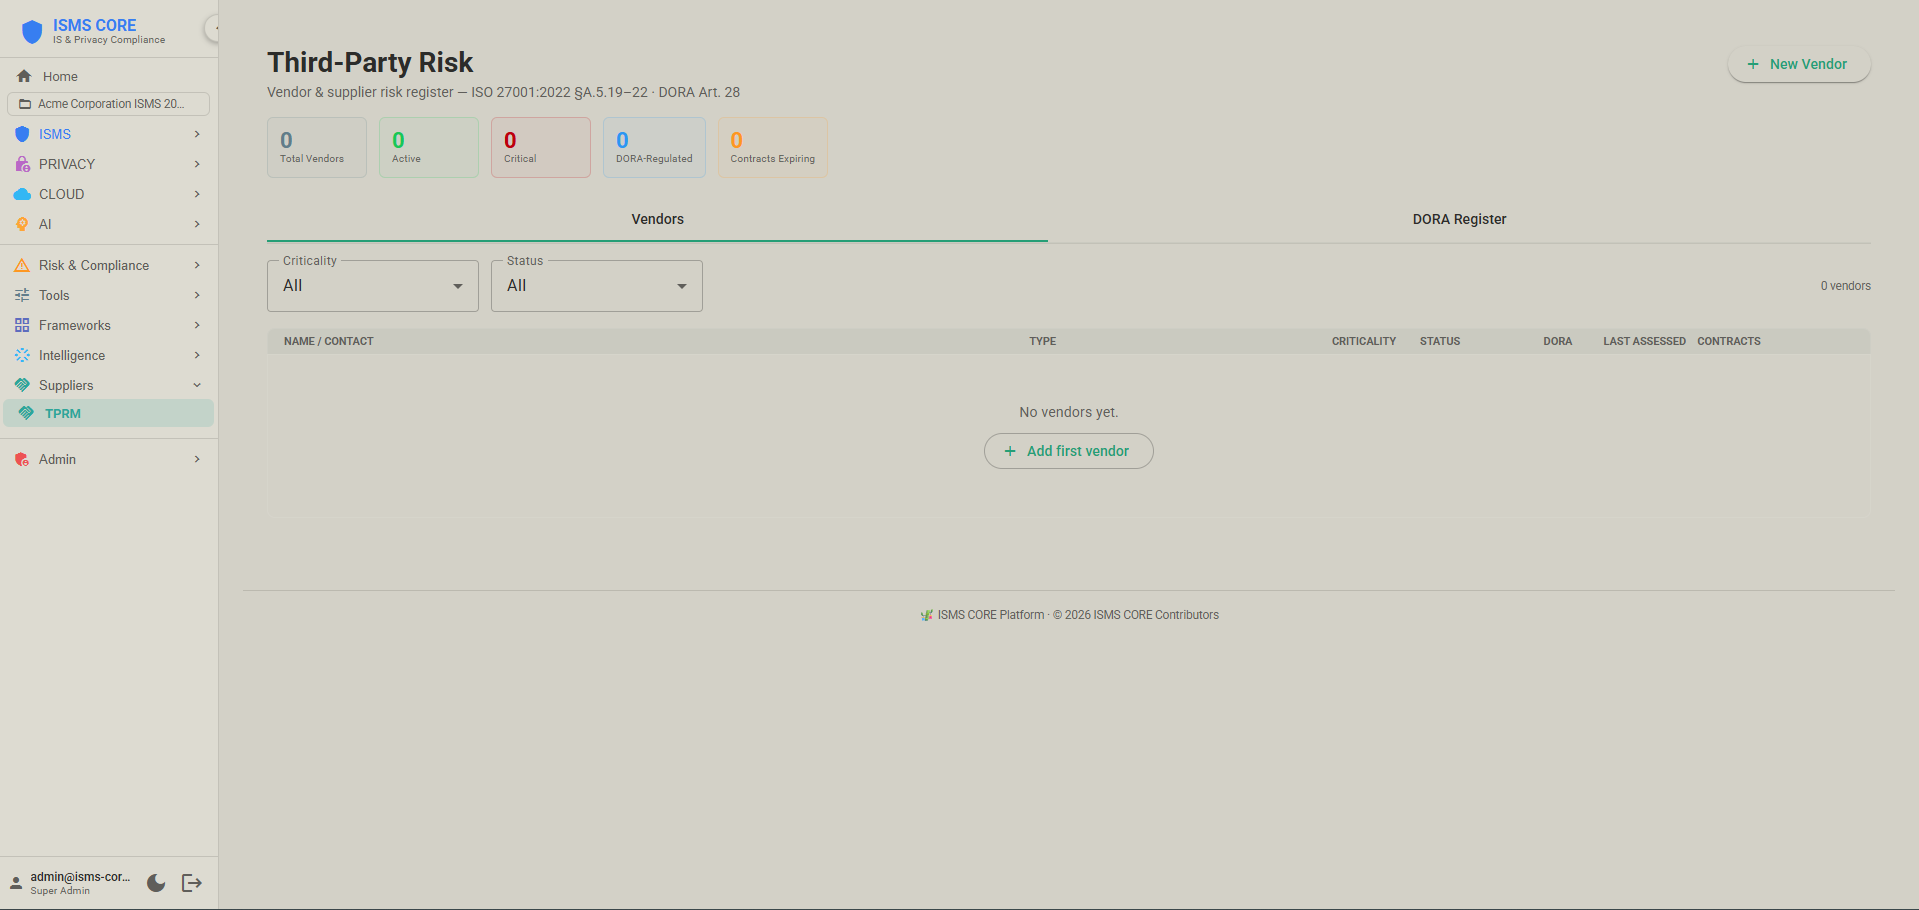
TPRM β€” Third-Party Risk
TPRM β€” vendor/supplier register with DORA ICT fields, contract expiry alerts
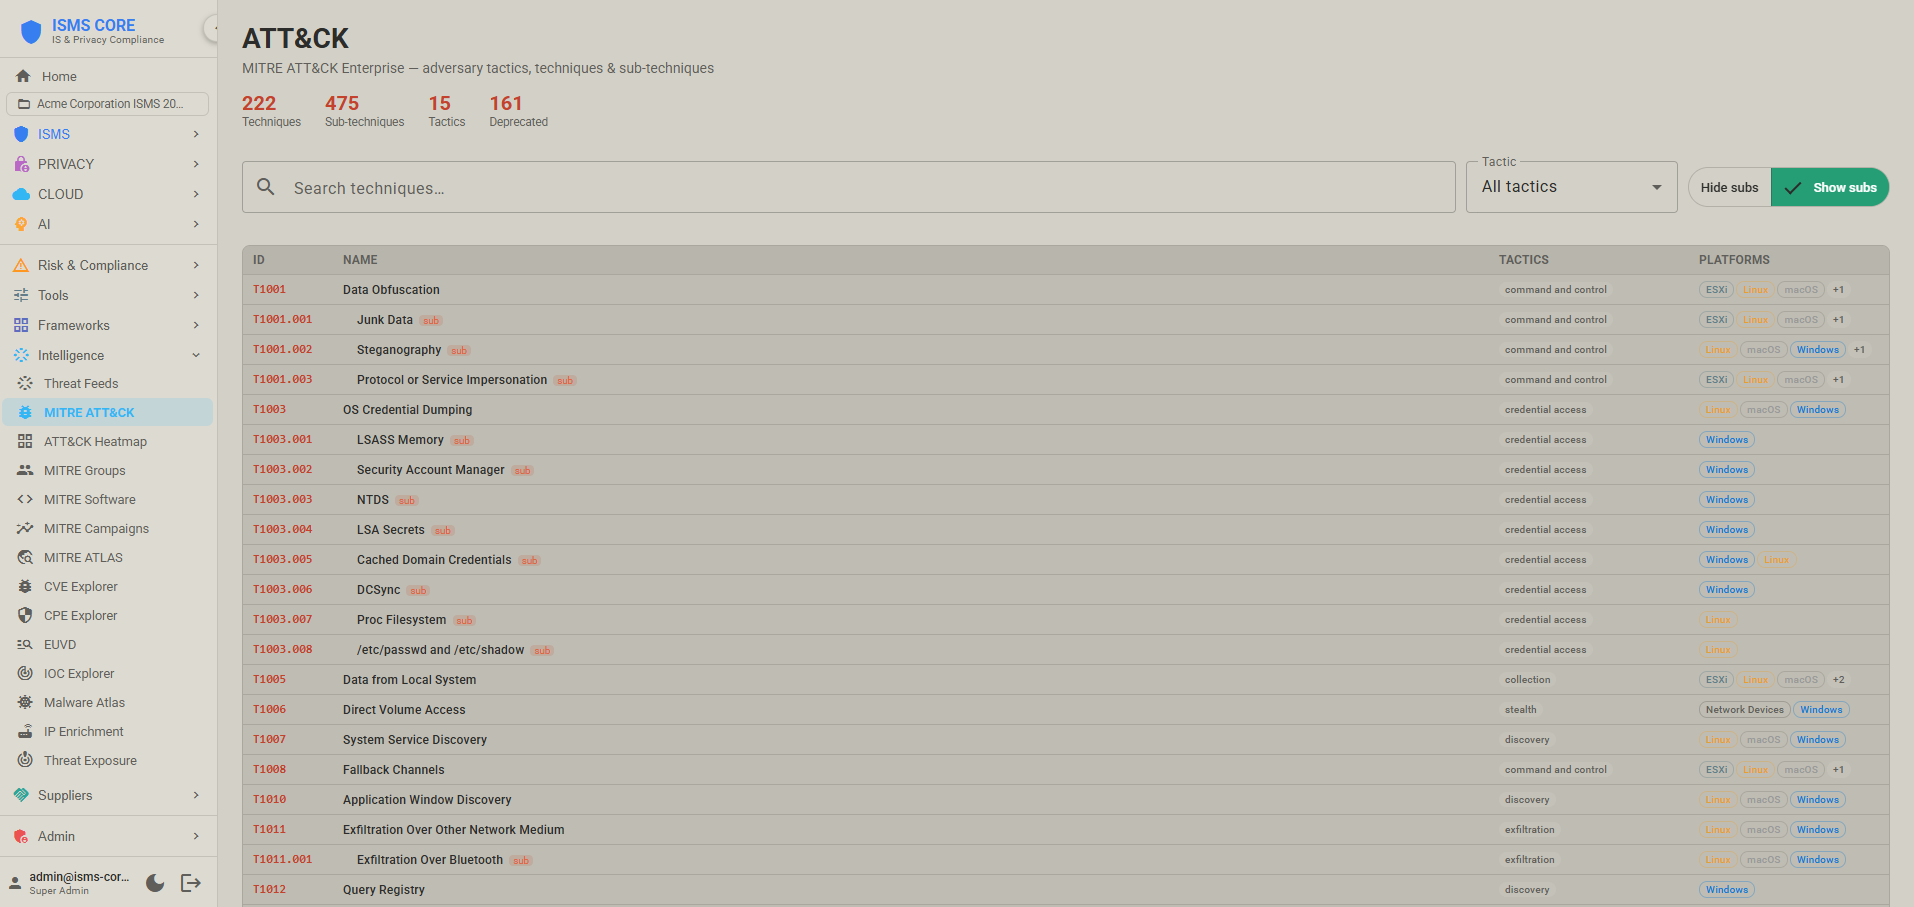
MITRE ATT&CK
MITRE ATT&CK v20 β€” 706 techniques across 15 tactics with EPSS and KEV correlation
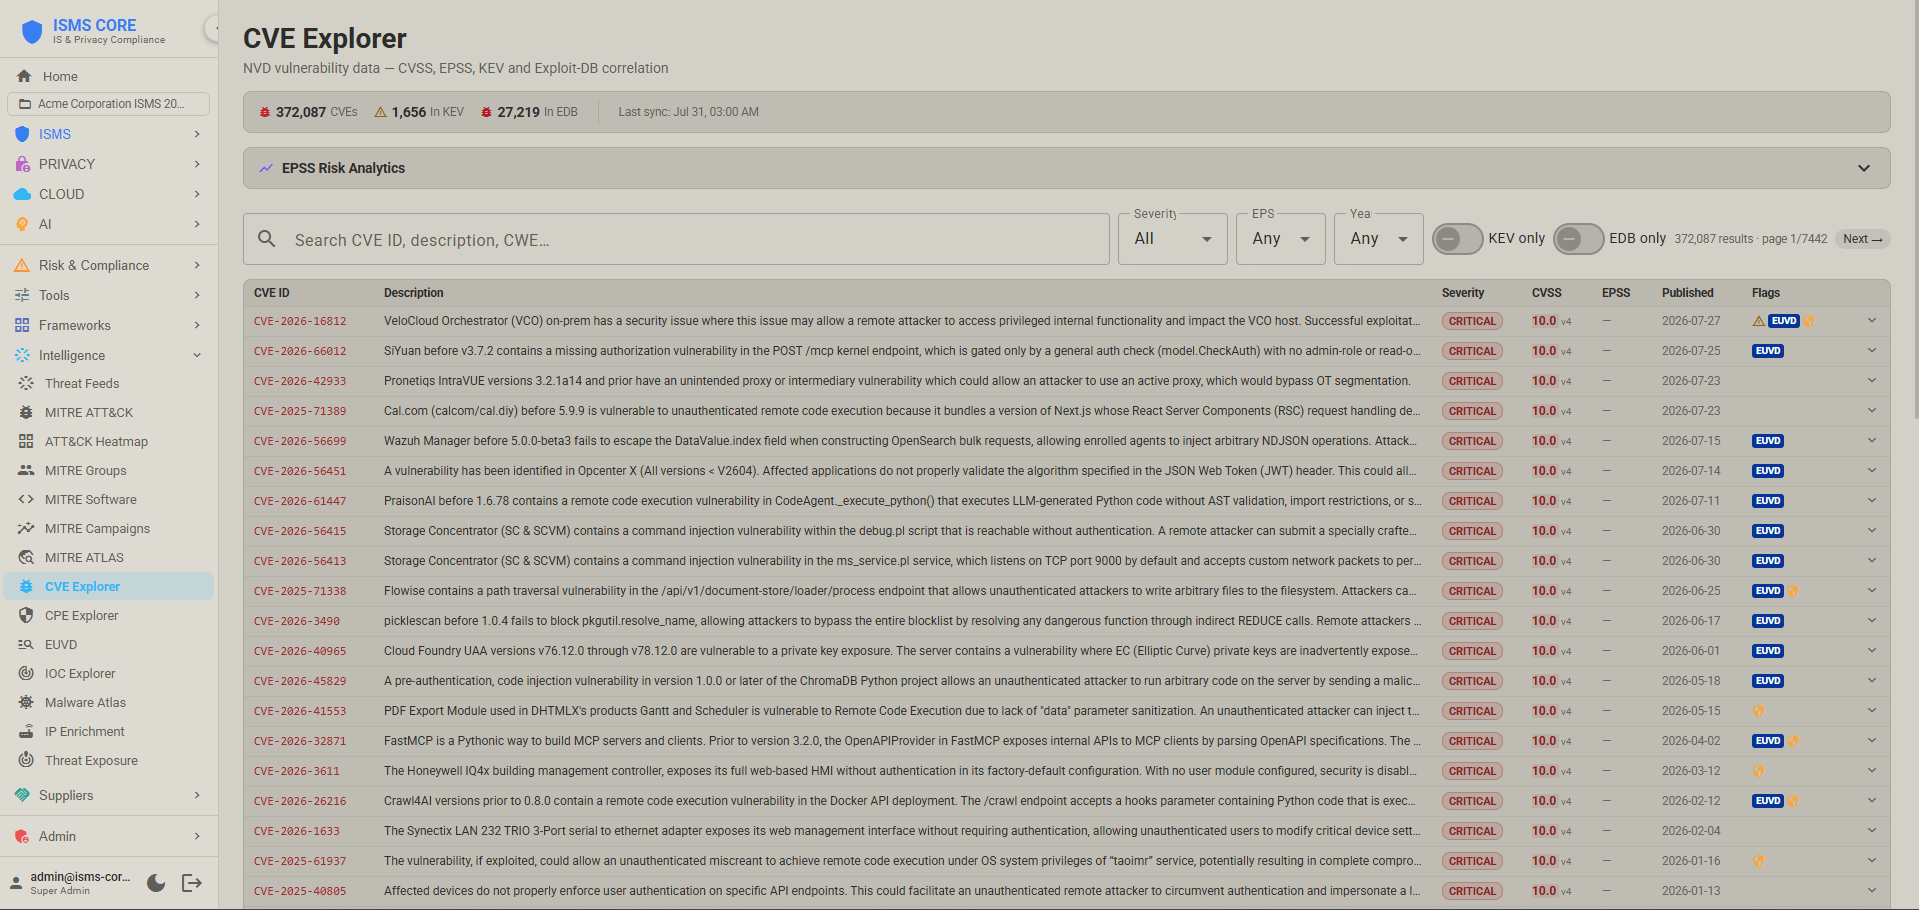
CVE Explorer
CVE/CPE Explorer β€” NVD vulnerability search with CVSS, EPSS, KEV filters
--- ## πŸ”— Framework Integration
Show all 29+ framework integrations and crosswalk mappings
| Framework / Standard | What ISMS CORE provides | Status | |---|---|---| | ISO/IEC 27001:2022 | Full Annex A control packs (Framework + Operational) | ![Complete](https://img.shields.io/badge/Complete-0066CC?style=flat-square) | | ISO/IEC 27002:2022 | Implementation guidance integrated into IMP-TG documents | ![Integrated](https://img.shields.io/badge/Integrated-0066CC?style=flat-square) | | ISO/IEC 27701:2025 | Full Privacy Extension Pack β€” controller, processor, and shared controls | ![Complete](https://img.shields.io/badge/Complete-7030A0?style=flat-square) | | ISO/IEC 27018:2025 | Full Cloud Extension Pack β€” 12 Annex A control groups for PII in cloud | ![Complete](https://img.shields.io/badge/Complete-00897B?style=flat-square) | | ISO/IEC 42001:2023 | Full AI Extension Pack β€” 10 AI control groups (plus 2 foundation policies) covering AIMS governance, impact assessment, responsible use, and third-party AI | ![Complete](https://img.shields.io/badge/Complete-FF6B35?style=flat-square) | | NIST CSF 2.0 | Full assessment tool β€” 106 subcategories, tier 1–4 ratings, XLSX import/export, radar chart. ISO 27001 crosswalk. | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-FF6600?style=flat-square) | | NIST AI RMF 1.0 | Full assessment tool β€” 72 subcategories, 0–4 maturity; ISO 42001 crosswalk: 32 mappings, EU AI Act: 13 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-FF6600?style=flat-square) | | NIS2 Directive (EU 2022/2555) | 10 Article 21 measures + 5 Article 23 obligations, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-003399?style=flat-square) | | DORA (EU 2022/2554) | 27 articles across 5 pillars (ICT Risk, Incident Reporting, Testing, TPRM, Information Sharing), maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-1565C0?style=flat-square) | | CIS Critical Security Controls v8 | 153 safeguards across 18 controls, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-2E7D32?style=flat-square) | | BSI IT-Grundschutz Kompendium | All 111 Bausteine across 10 layers, maturity 0–4. Crosswalk: ISO 27001↔BSI (386), ISO 27701↔BSI (101), ISO 27018↔BSI (51) | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-CC0000?style=flat-square) | | CSRM (Swiss NCSC, 2025) | Object-centric module β€” IT Protection Objects, 20 NIST CSF 2.0 baseline requirements, binary status, 6 Control Objectives | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-D32F2F?style=flat-square) | | TISAX / VDA ISA 6.0 | 79 requirements across 9 domains, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-1B5E20?style=flat-square) | | Swiss nDSG 2023 | 25 provisions across 6 chapters, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-C62828?style=flat-square) | | Swiss ISG (SR 128, 2024) | 27 requirements across 8 sections, 24h cyberattack reporting; ISO 27001 crosswalk: 27 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-B71C1C?style=flat-square) | | EU Cyber Resilience Act (2024/2847) | 26 essential requirements across 6 groups, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-1A237E?style=flat-square) | | EU AI Act (2024/1689) | 9 articles β€” Chapter III Section 2 high-risk system requirements (Art. 8–15) plus Art. 27 fundamental rights impact assessment, maturity 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-4527A0?style=flat-square) | | EU Cloud Sovereignty Framework (v1.2.1) | 8 Sovereignty Objectives (SOV-1 to SOV-8), SEAL-0 to SEAL-4 scoring, weighted Sovereignty Score | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-01579B?style=flat-square) | | COBIT 2019 | 40 governance/management objectives, capability scoring 0–4 | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-7B1FA2?style=flat-square) | | CyberFundamentals (BE) | 41 NIST CSF 2.0 aligned practices, maturity 0–4; ISO 27001 crosswalk: 107 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-1A237E?style=flat-square) | | BaFin BAIT (DE) | 23 requirements across 12 modules, maturity 0–4; ISO 27001 crosswalk: 69 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-B71C1C?style=flat-square) | | BSI C5:2026 (DE) | 168 criteria across 17 domains β€” Cloud Computing Compliance Criteria Catalogue v1.0.1. Used for third-party attestation of cloud service providers in Germany and the EU. Replaces C5:2020. | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-C62828?style=flat-square) | | BSI C3A (DE) | 30 criterion groups across 6 sovereignty domains (Strategic / Legal / Data / Operational / Supply Chain / Technology) β€” Criteria enabling Cloud Computing Autonomy v1.0. Companion to C5:2026; presupposes C5 compliance. | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-AD1457?style=flat-square) | | CSSF 20-750 (LU) | 19 requirements across 7 domains, maturity 0–4; ISO 27001 crosswalk: 47 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-4A148C?style=flat-square) | | ACN Guidelines (IT) | Determinazione obblighi di base (Apr 2025) β€” 37 measures/87 requirements (Important) or 43 measures/116 requirements (Essential), maturity 0–4; ISO 27001 crosswalk: 43 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-006630?style=flat-square) | | UK NIS Regulations | 13 requirements across 3 objectives, maturity 0–4; ISO 27001 crosswalk: 51 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-1A237E?style=flat-square) | | UK Operational Resilience | 12 requirements across 4 objectives, maturity 0–4; ISO 27001 crosswalk: 34 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-283593?style=flat-square) | | NCSC CAF v4.0 (UK) | 41 Contributing Outcomes across 14 Principles and 4 Objectives β€” outcome-based; ISO 27001 crosswalk: 41 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-003366?style=flat-square) | | ReCyF v2.5 β€” France NIS2 (ANSSI) | 20 Security Objectives across 4 pillars (Gouvernance / Protection / DΓ©fense / RΓ©silience) β€” France's pending NIS2 transposition law; ISO 27001 crosswalk: 20 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-002395?style=flat-square) | | PCI DSS v4.0.1 | 198 assessed sub-requirements across 12 requirements, 6 prioritised milestones, milestone-based scoring; ISO 27001 crosswalk: 39 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-003087?style=flat-square) | | FINMA | 21 requirements across 3 circulars/guidance (2023/1 Operational Risk, 2018/3 Outsourcing, Guidance 03/2024 Cyber Risks), maturity 0–4; ISO 27001 crosswalk: 73 mappings | ![Assessment Tool](https://img.shields.io/badge/Assessment_Tool-5D4037?style=flat-square) | | NIST SP 800-53 Rev. 5 | Security control cross-mapping | ![Mapped](https://img.shields.io/badge/Mapped-FF6600?style=flat-square) | | MITRE ATT&CK v20 | Threat technique mapping (Enterprise / ICS / Mobile) β€” 706 techniques across 15 tactics, EPSS + CISA KEV correlation. v19 is kept alongside v20. | ![v20](https://img.shields.io/badge/v20-DC143C?style=flat-square) | | MITRE ATLAS | AI/ML adversarial threat techniques | ![Mapped](https://img.shields.io/badge/Mapped-DC143C?style=flat-square) | | ENISA EUVD | European Vulnerability Database β€” exploited + critical CVEs; daily feed; EUVD Explorer + cross-enrichment of NVD CVE index with `in_euvd` flag | ![Feed](https://img.shields.io/badge/TI_Feed-003399?style=flat-square) | | Exploit-DB | Daily exploit database (~52K entries) β€” cross-referenced to NVD CVE by CVE ID; adds `edb_id`, `edb_verified` (Metasploit module flag), `edb_description` to matching CVEs. EDB/EDBβœ“ chips in CVE Explorer; EDB-only filter. | ![Feed](https://img.shields.io/badge/TI_Feed-8B0000?style=flat-square) | | VulnCheck KEV | Daily feed β€” VulnCheck's own Known Exploited Vulnerabilities catalogue, broader than CISA's (~67% of entries aren't in CISA KEV); adds `in_vulncheck_kev` flag, separate from CISA's `in_kev`, on CVE Explorer. VC-KEV chip; VulnCheck-only filter. Requires `VULNCHECK_API_KEY` (free Community tier). | ![Feed](https://img.shields.io/badge/TI_Feed-6A1B9A?style=flat-square) | | CIRCL MISP OSINT Feed | Public MISP feed (Luxembourg) β€” 6-hourly manifest delta; 100K+ IOCs (IPs, domains, URLs, hashes) cross-enriched with ATT&CK TIDs, Malpedia family slugs, actor slugs at ingest | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | Botvrij MISP OSINT Feed | Public MISP feed (Botvrij.eu) β€” 6-hourly manifest delta; deduplicated against CIRCL by IOC value + source | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | AbuseIPDB | Daily blacklist (top 10K confidence=100 IPs); on-demand single-IP enrichment with 24h cache; OpenSearch `ti-abuseipdb-blacklist` index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | Malpedia | Weekly malware knowledge base β€” families (aliases, ATT&CK TIDs), threat actors (country, motivation); links IOCs to malware + actor attribution | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | URLhaus | Daily malware download URL feed (abuse.ch) β€” URLs, associated payload hashes; `ti-urlhaus` OpenSearch index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | ThreatFox | Daily malware IOC feed (abuse.ch) β€” IPs, domains, URLs, hashes with confidence scores and malware family labels; requires `THREATFOX_API_KEY` | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | SSL Blacklist (SSLBL) | Daily SSL certificate blacklist (abuse.ch) β€” SHA1 fingerprints of certificates used by malware C2 infrastructure; `ti-sslbl` index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | MalwareBazaar | Daily malware sample hash feed (abuse.ch) β€” MD5/SHA1/SHA256 hashes with family classification; requires `MALWAREBAZAAR_API_KEY` | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | Feodo Tracker | Daily C2 IP blacklist (abuse.ch) β€” Emotet, QakBot, TrickBot, Dridex botnet command-and-control IPs; confidence 85; `ti-feodotracker` index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | AlienVault OTX | Daily Open Threat Exchange pulses β€” IOCs with TLP labels (WHITE/GREEN/AMBER/RED), ATT&CK TIDs, and confidence scores derived from pulse subscriber count; requires `OTX_API_KEY` | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | Red Flag Domains | Daily suspicious newly-registered domain feed β€” `ti-red-flag-domains` index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | Stopforumspam | Daily spammer IP/email/username database β€” `ti-stopforumspam` index | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | VirusTotal enrichment | Daily IOC confidence enrichment β€” queries existing IOCs against VT v3 API, updates confidence scores based on AV engine detection ratios; free tier (~500 req/day); requires `VT_API_KEY` | ![OSINT Feed](https://img.shields.io/badge/OSINT_Feed-8B0000?style=flat-square) | | GreyNoise enrichment | On-demand IP Enrichment lookup β€” internet-noise/scanner classification, RIOT (known-legitimate-service) status; free Community tier capped at 50 lookups/week, so manual-lookup only, never a scheduled bulk feed; requires `GREYNOISE_API_KEY` | ![Enrichment](https://img.shields.io/badge/Enrichment-6A1B9A?style=flat-square) | | EU GDPR / Swiss DSG | Security and privacy control mapping, operational checklists | ![Toolkit](https://img.shields.io/badge/Toolkit-FFD700?style=flat-square) |


--- ## ✈️ Philosophy: Not Cargo Cult > *"The first principle is that you must not fool yourself β€” and you are the easiest person to fool."* > β€” Richard Feynman | | Cargo Cult | ISMS CORE | |---|---|---| | ❌ | Impressive policies nobody reads | βœ… Controls that **actually work** | | ❌ | Made-up compliance numbers | βœ… Evidence that **proves effectiveness** | | ❌ | Security theater for audits | βœ… Metrics that **measure real security** | | ❌ | PowerPoints instead of controls | βœ… Automation that **enforces compliance** | See [PHILOSOPHY.md](PHILOSOPHY.md) for the full methodology. --- ## πŸ”¬ Quality Assurance Every control pack undergoes a structured multi-stage validation before promotion to this repository: ``` β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β” β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β” β”Œβ”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β” β”‚ Claude Code │────▢│ ISMS QA Engine │────▢│ The ISMS Core β”‚ β”‚ (Build + QA) β”‚ β”‚ Existence + Keyword + β”‚ β”‚ Project (Final) β”‚ β”‚ β”‚ β”‚ Semantic 3-layer check β”‚ β”‚ β”‚ β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜ β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜ β””β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”€β”˜ ``` All 188 Framework generators, 53 Operational policies, 21 Privacy control groups, 16 Cloud control groups (12 PII + 4 Security), and 10 AI control groups carry `QA_VERIFIED` markers confirming a full QA pass. See [CONTRIBUTING.md](CONTRIBUTING.md) for detailed QA standards. --- ## πŸ“Š Status at a Glance | Product | Control groups | Key artifacts | Languages | Version | |---------|---------------|---------------|-----------|---------| | πŸ—οΈ Framework | 53 / 53 | 376 IMPs Β· 188 generators Β· 188 workbooks | EN FR DE IT | ![v1.0](https://img.shields.io/badge/v1.0-Complete-00AA00?style=flat-square) | | ⚑ Operational | 53 / 53 | 53 OP-POL Β· 53 checklist generators | EN FR DE IT | ![v0.1](https://img.shields.io/badge/v0.1-Complete-00AA00?style=flat-square) | | πŸ”’ Privacy | 21 / 21 | 23 PRIV-POL Β· 42 IMPs Β· 21 generators | EN FR DE IT | ![v1.0](https://img.shields.io/badge/v1.0-Complete-7030A0?style=flat-square) | | ☁️ Cloud | 16 / 16 | 16 CLD-POL Β· 32 IMPs Β· 16 generators | EN FR DE IT | ![v1.0](https://img.shields.io/badge/v1.0-Complete-00897B?style=flat-square) | | πŸ€– AI | 12 / 12 | 12 AI-POL Β· 20 IMPs Β· 10 generators | EN FR DE IT | ![v1.0](https://img.shields.io/badge/v1.0-Complete-FF6B35?style=flat-square) | | πŸ–₯️ Platform | 104 total | 46 connectors Β· 29 assessments Β· 4,632 mappings / 60 axes | 8 jurisdictions | ![Live v1.3](https://img.shields.io/badge/Live-v1.3-2E8B57?style=flat-square) | --- ## πŸ“‚ Repository Structure See [STRUCTURE.md](STRUCTURE.md) for the complete repository map with per-folder and per-artifact-type explanations. --- ## πŸ“š Documentation | Document | Description | |----------|-------------| | [PARADIGM.md](PARADIGM.md) | 🧭 Product overview and paradigm shift guide β€” start here | | [PLATFORM.md](PLATFORM.md) | πŸ–₯️ Platform architecture, features, and full deployment guide (includes Docker Compose quick-start) | | [STRUCTURE.md](STRUCTURE.md) | πŸ“‚ Repository map β€” all folders and artifact types explained | | [COMPLIANCE.md](COMPLIANCE.md) | πŸ“‹ All 29 compliance assessment modules β€” coverage notes, gaps, audience | | [isms-core-framework/CONTROLS.md](isms-core-framework/CONTROLS.md) | πŸ“‹ Framework control pack index (53 packs) | | [isms-core-framework/COVERAGE.md](isms-core-framework/COVERAGE.md) | πŸ—ΊοΈ 93 Annex A controls β†’ 53 pack mapping | | [isms-core-framework/STACKING.md](isms-core-framework/STACKING.md) | πŸ”— Control grouping methodology | | [PHILOSOPHY.md](PHILOSOPHY.md) | ✈️ Anti-cargo-cult methodology | | [CONTRIBUTING.md](CONTRIBUTING.md) | πŸ”§ QA process and standards | | [SECURITY.md](SECURITY.md) | πŸ”’ Vulnerability reporting policy | | [isms-core-platform/CHANGELOG.md](isms-core-platform/CHANGELOG.md) | πŸ“ Platform release notes | | [CREDITS.md](CREDITS.md) | πŸ™ Third-party tools and open-source acknowledgements | --- ## πŸ”’ Security - **Vulnerability reporting:** Report security issues to **info@isms-core.com** (subject: "ISMS CORE Security") - **Safe usage:** Review scripts before execution. Run in a virtual environment. Treat generated artifacts as sensitive until proven otherwise. - **No secrets:** Do not commit credentials, tokens, private keys, or customer data to this repository or to generated workbooks. --- ## πŸ“œ License Two separate works, two licenses: - **Content packs** (`isms-core-framework/`, `isms-core-operational/`, `isms-core-privacy/`, `isms-core-cloud/`, `isms-core-ai/` β€” the POL/IMP/SCR compliance documents) are **dual-licensed**: - **AGPL-3.0** for open-source use β€” see [LICENSE](LICENSE) - **Commercial license** for organisations that cannot comply with AGPL obligations β€” **info@isms-core.com** - **`isms-core-platform/`** (the deployable API/engineering product) is **Apache 2.0** β€” see [isms-core-platform/LICENSE](isms-core-platform/LICENSE). Distributed as pre-built container images; no commercial license needed. --- ## πŸ“ž Contact

The ISMS Core Project

Email GitHub Website Platform Compliance Frameworks

---

Copyright Β© 2025–2026 The ISMS Core Project. All rights reserved.

Where bamboo antennas actually work. πŸŽ‹