[](https://madhuakula.com/kubernetes-goat)
## 🧰 Setting up Kubernetes Goat
* Ensure you have admin access to the Kubernetes cluster and installed `kubectl`. Refer to the [docs for installation](https://kubernetes.io/docs/tasks/tools/install-kubectl/)
* Ensure you have the `helm` package manager installed. Refer to the [docs for installation](https://helm.sh/docs/intro/install)
* To set up the Kubernetes Goat resources in your cluster, run the following commands:
```bash
git clone https://github.com/madhuakula/kubernetes-goat.git
cd kubernetes-goat
chmod +x setup-kubernetes-goat.sh
bash setup-kubernetes-goat.sh
```
* Ensure the pods are running before running the access script
```bash
kubectl get pods
```

* Access Kubernetes Goat by exposing the resources to the local system (port-forward) by the following command:
```bash
bash access-kubernetes-goat.sh
```
* Then navigate to [`http://127.0.0.1:1234`](http://127.0.0.1:1234)
> Refer to [https://madhuakula.com/kubernetes-goat/docs/how-to-run](https://madhuakula.com/kubernetes-goat/docs/how-to-run) for setting up Kubernetes Goat in various environments like GKE, EKS, AKS, K3S, KIND, etc.
## 🏆 Scenarios
1. Sensitive keys in codebases
2. DIND (docker-in-docker) exploitation
3. SSRF in the Kubernetes (K8S) world
4. Container escape to the host system
5. Docker CIS benchmarks analysis
6. Kubernetes CIS benchmarks analysis
7. Attacking private registry
8. NodePort exposed services
9. Helm v2 tiller to PwN the cluster - [Deprecated]
10. Analyzing crypto miner container
11. Kubernetes namespaces bypass
12. Gaining environment information
13. DoS the Memory/CPU resources
14. Hacker container preview
15. Hidden in layers
16. RBAC least privileges misconfiguration
17. KubeAudit - Audit Kubernetes clusters
18. Falco - Runtime security monitoring & detection
19. Popeye - A Kubernetes cluster sanitizer
20. Secure network boundaries using NSP
21. Cilium Tetragon - eBPF-based Security Observability and Runtime Enforcement
22. Securing Kubernetes Clusters using Kyverno Policy Engine
## 📖 Documentation Guide
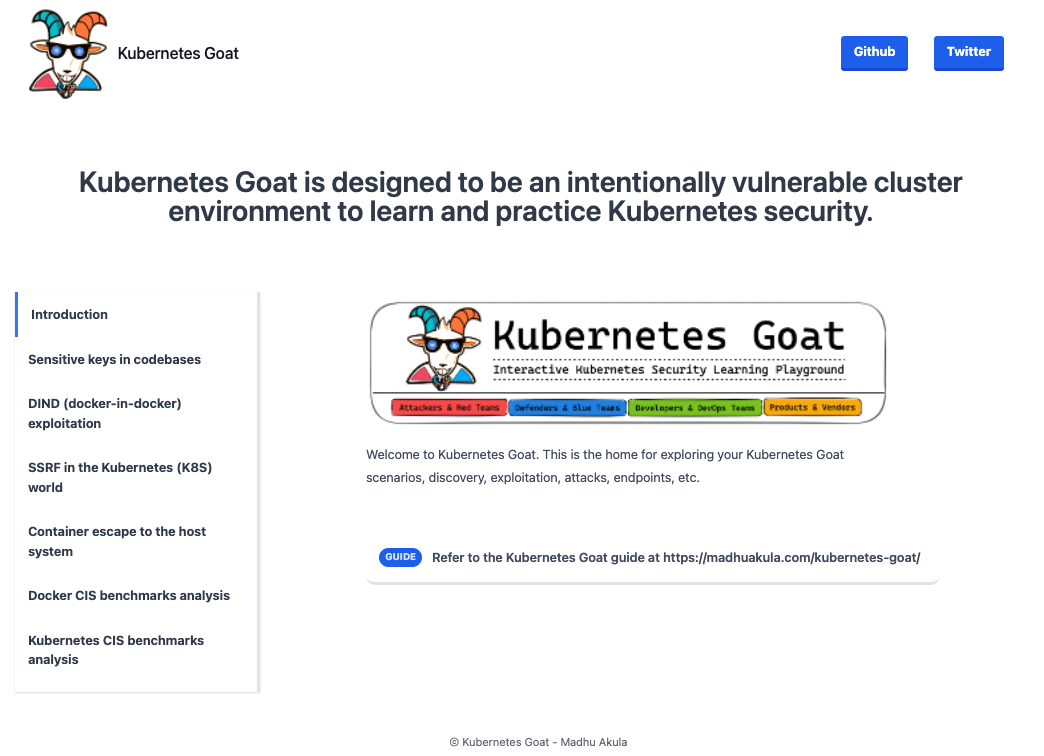
Here is the detailed step by step guide for learning and using Kubernetes Goat 🎉: [documentation guide](https://madhuakula.com/kubernetes-goat)
[](https://madhuakula.com/kubernetes-goat)
**Reference: [https://madhuakula.com/kubernetes-goat](https://madhuakula.com/kubernetes-goat)**
## ⚠️ Disclaimer
> Kubernetes Goat has intentionally created vulnerabilities, applications, and configurations to attack and gain access to your cluster and workloads. Please **DO NOT** run this alongside your production environments and infrastructure. We highly recommend running this in a safe and isolated (contained) environment.
> Kubernetes Goat is used for educational purposes only. Do not test or apply these attacks on any systems without permission. Kubernetes Goat comes with absolutely no warranties, by using it you take full responsibility for all outcomes.
## 📝 License
[MIT](https://github.com/madhuakula/kubernetes-goat/blob/master/LICENSE)
## ✨ Acknowledgements
Thanks to to these wonderful people: 🎉