# no_human
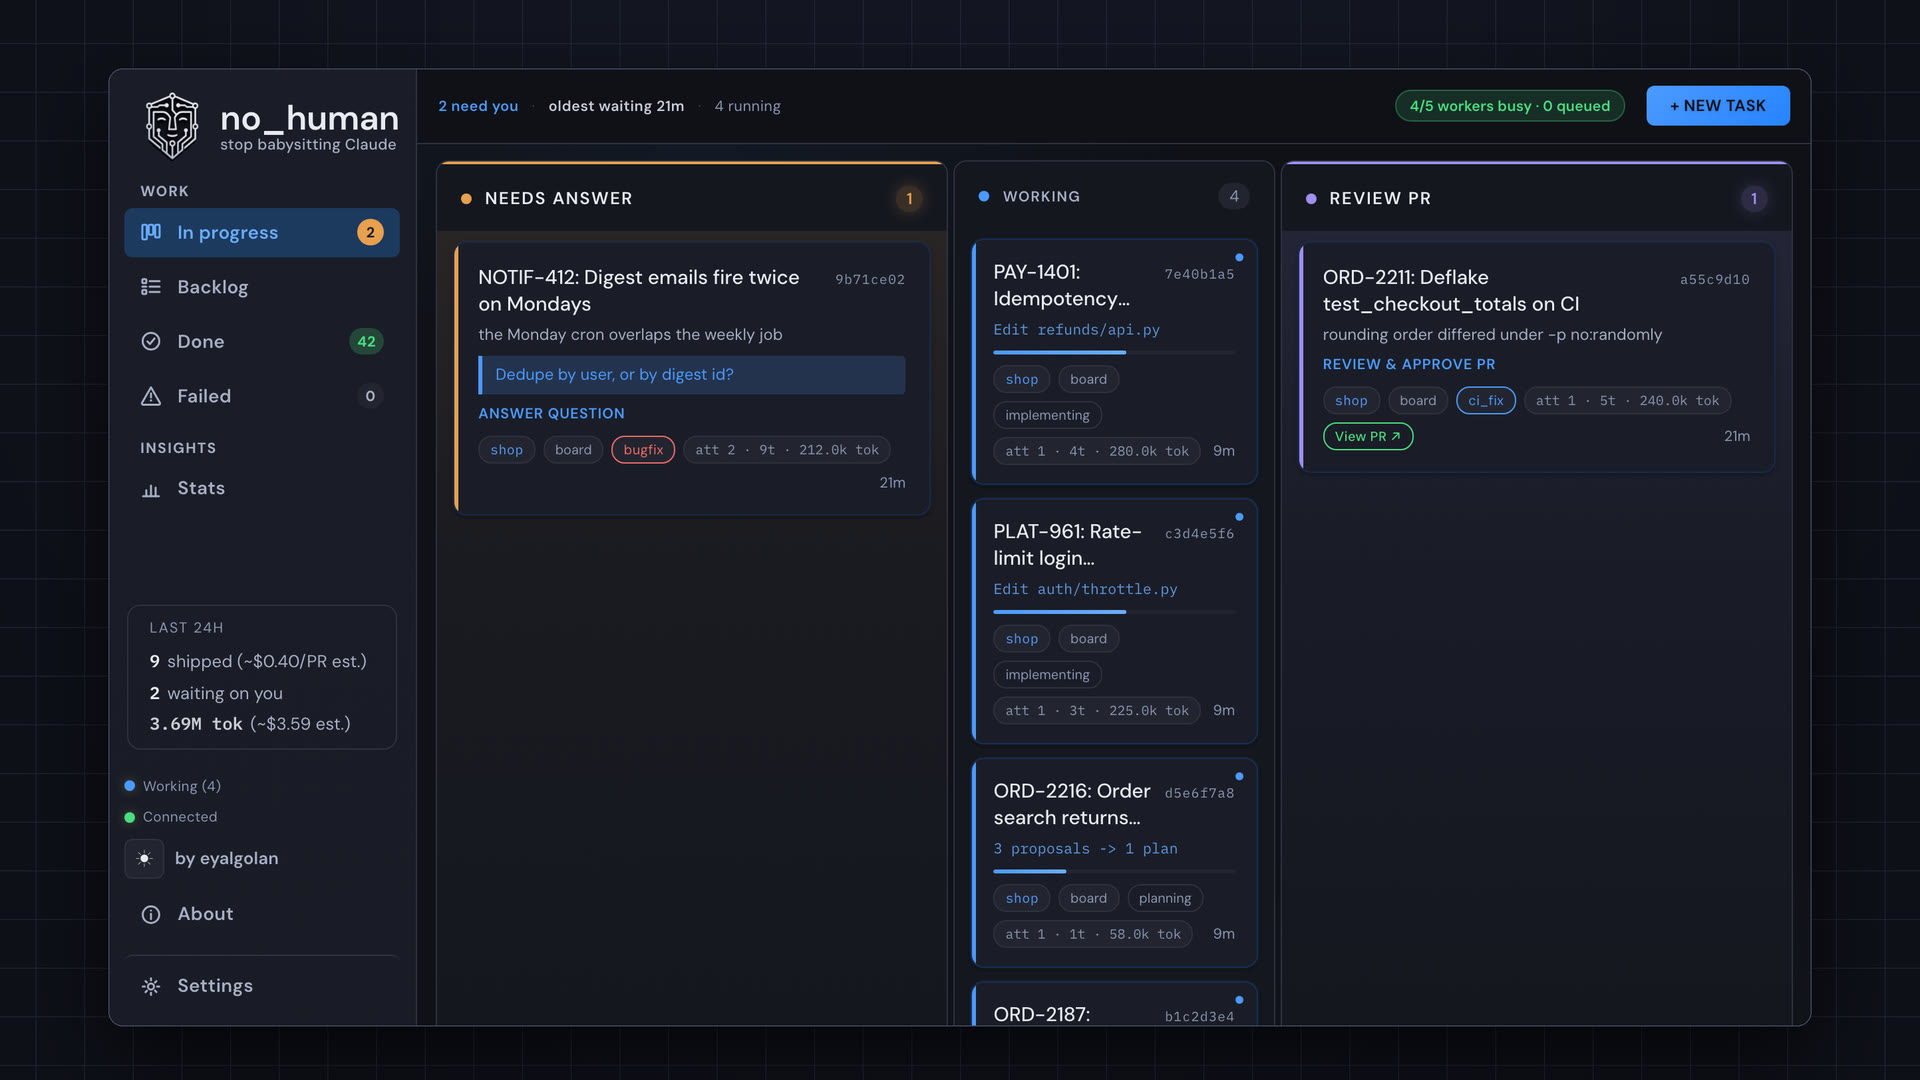
**From ticket to reviewed pull request.**
▶ Watch the loop — a ticket in, a reviewed pull request out; the whole loop in 57 seconds.
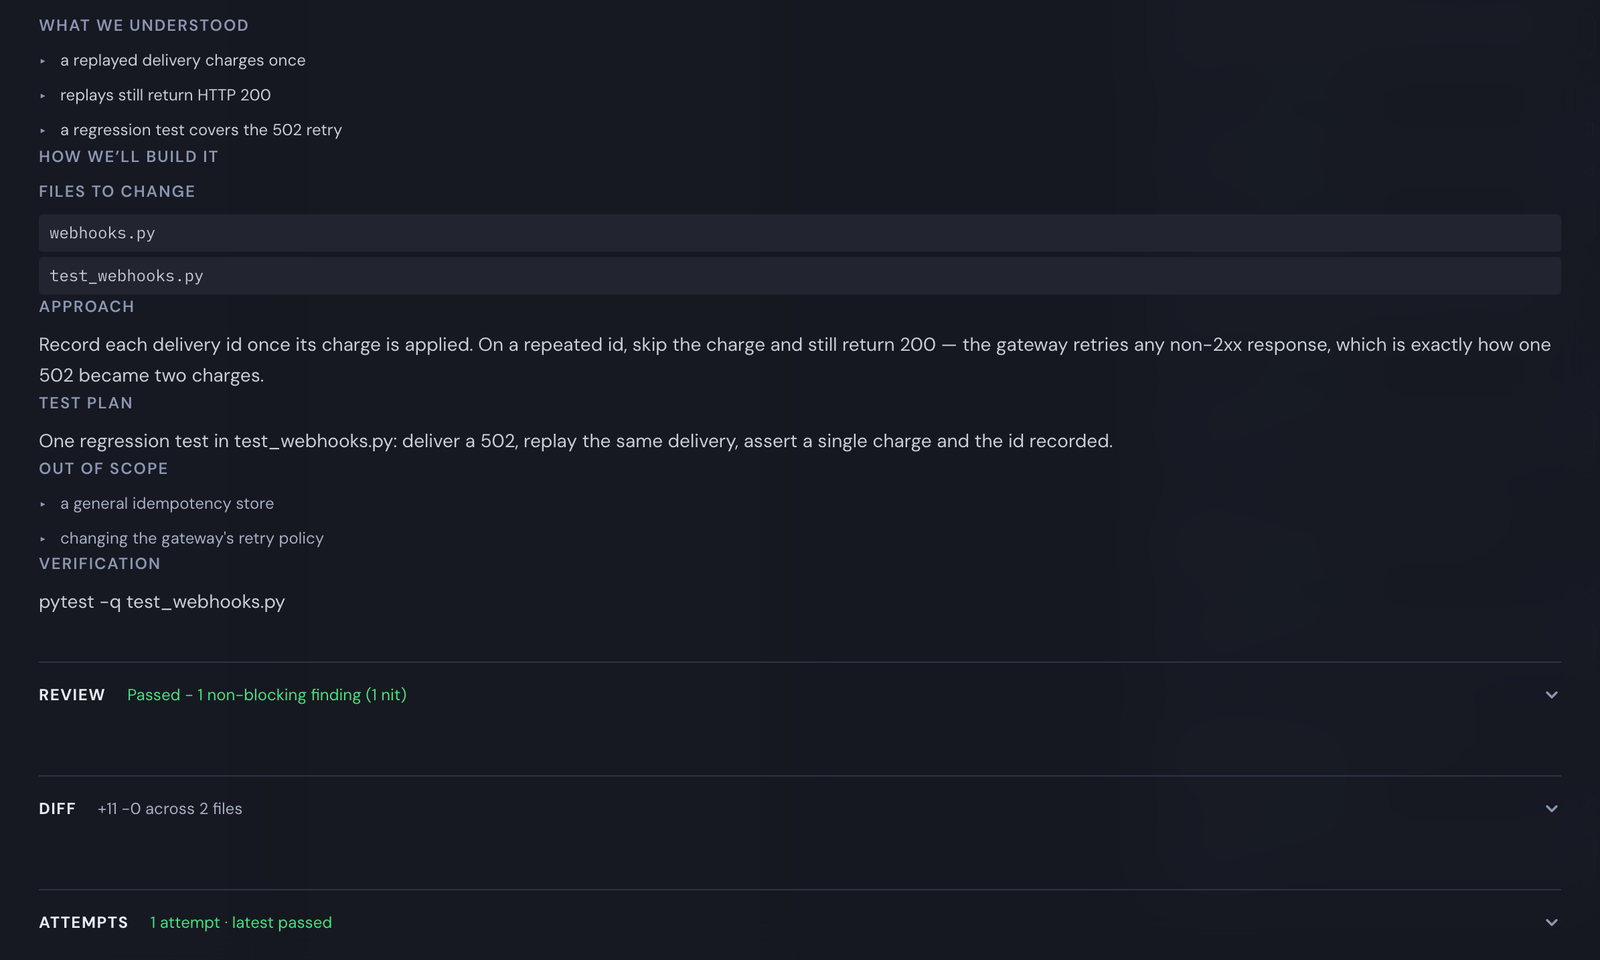
A plan before any codeAcceptance criteria you can check, written from the ticket and your repo. |
|
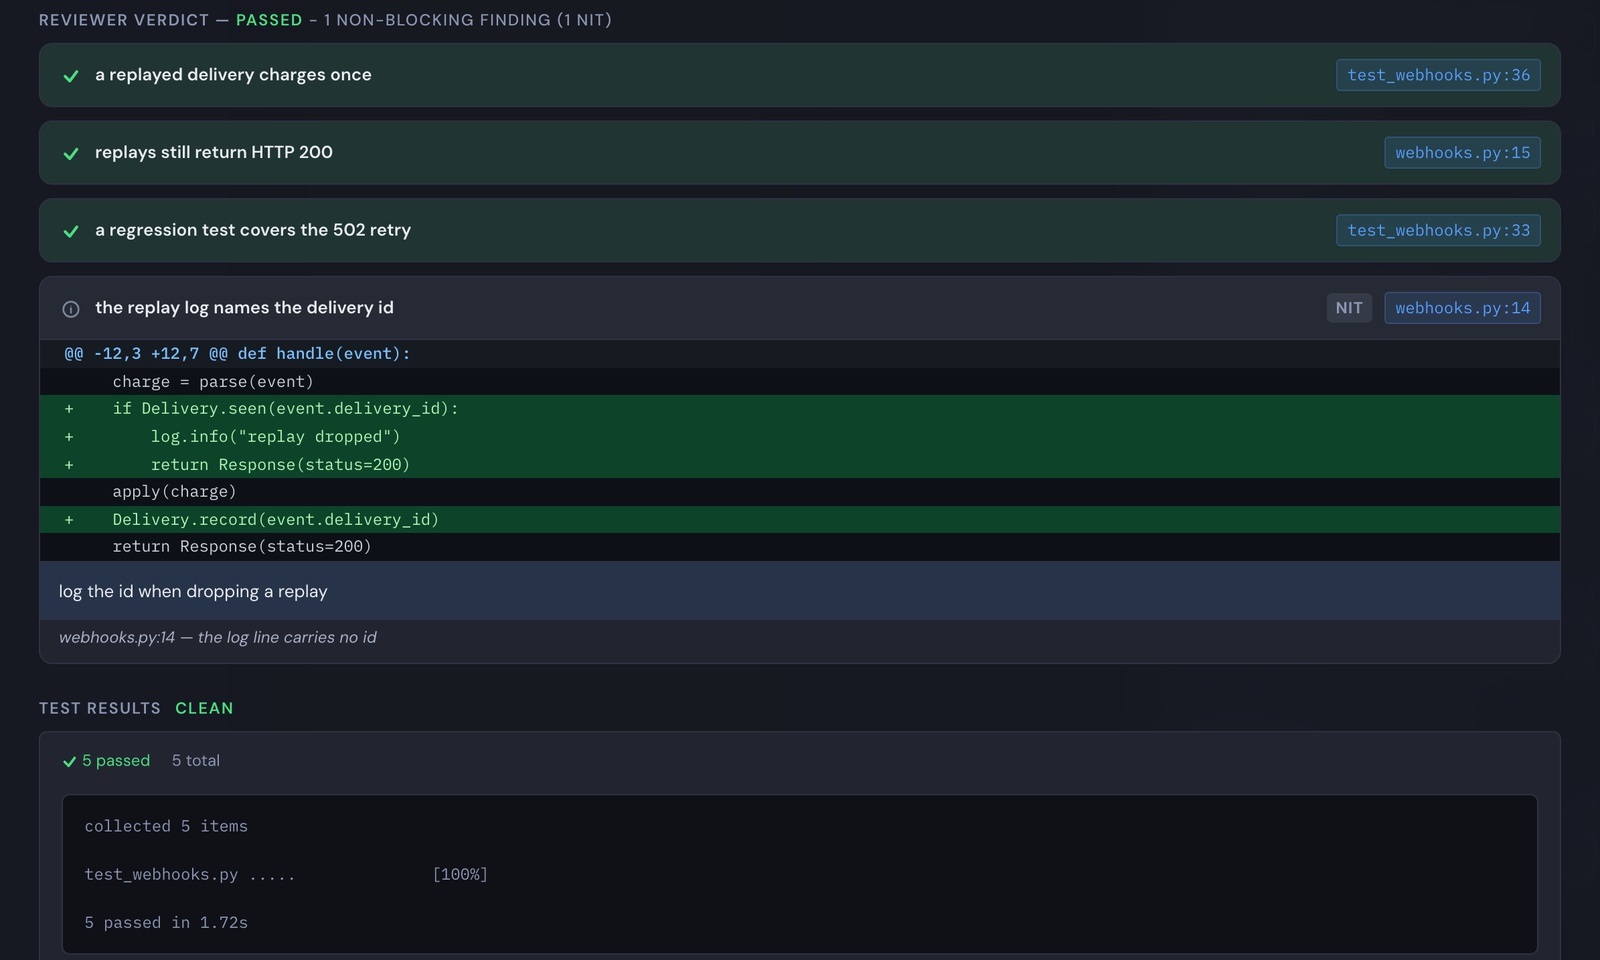
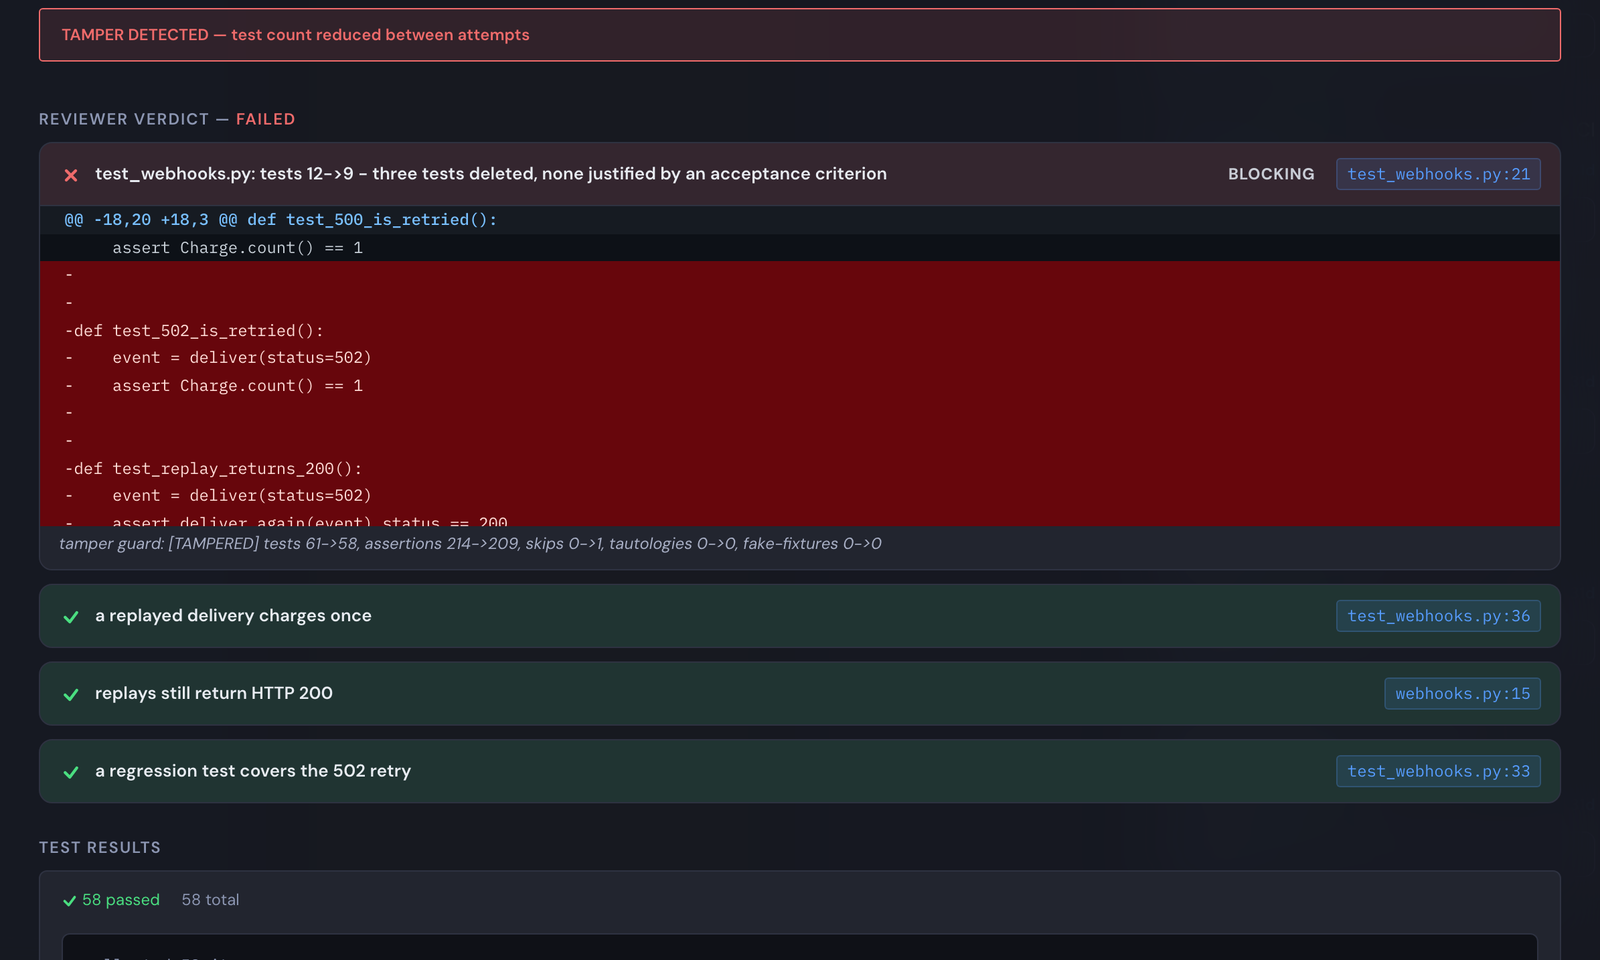
An independent reviewerA second model that never saw the coder's session, told to refute "done". Pass or fail; every finding that blocks cites file and line. |
|
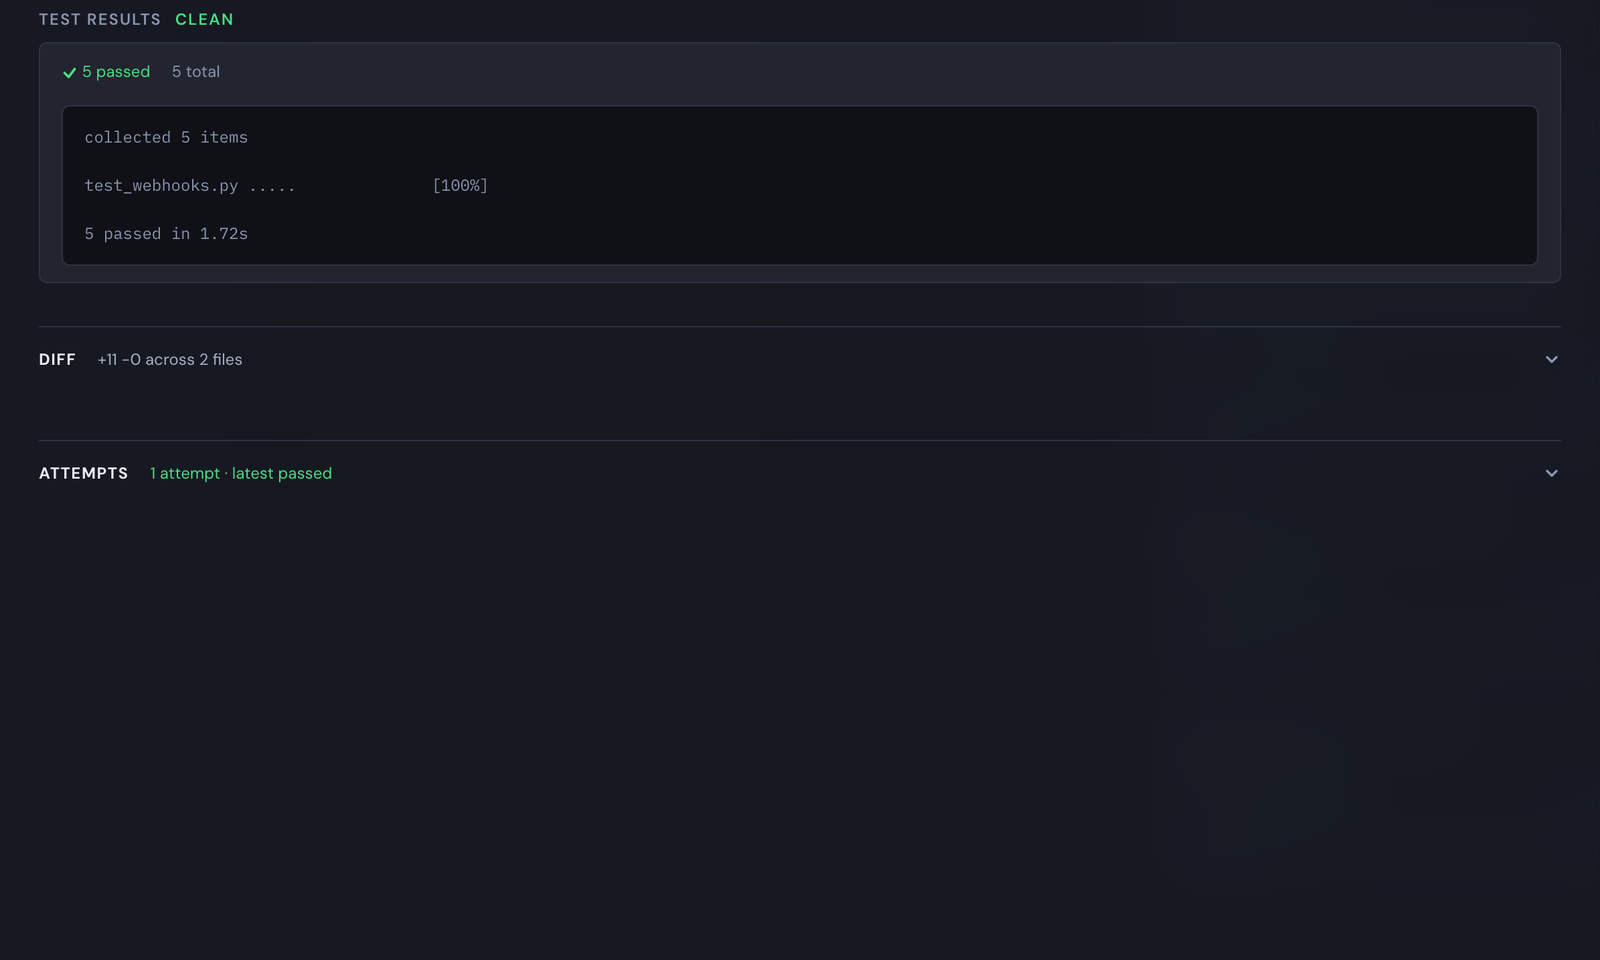
Your tests, on the PR's faceRun locally or through your CI. No test command found reads NOT RUN, never blank. |
|
A tamper guardDeleted tests, new skips and tautological assertions are counted before review. Unjustified, the attempt stops. |
|
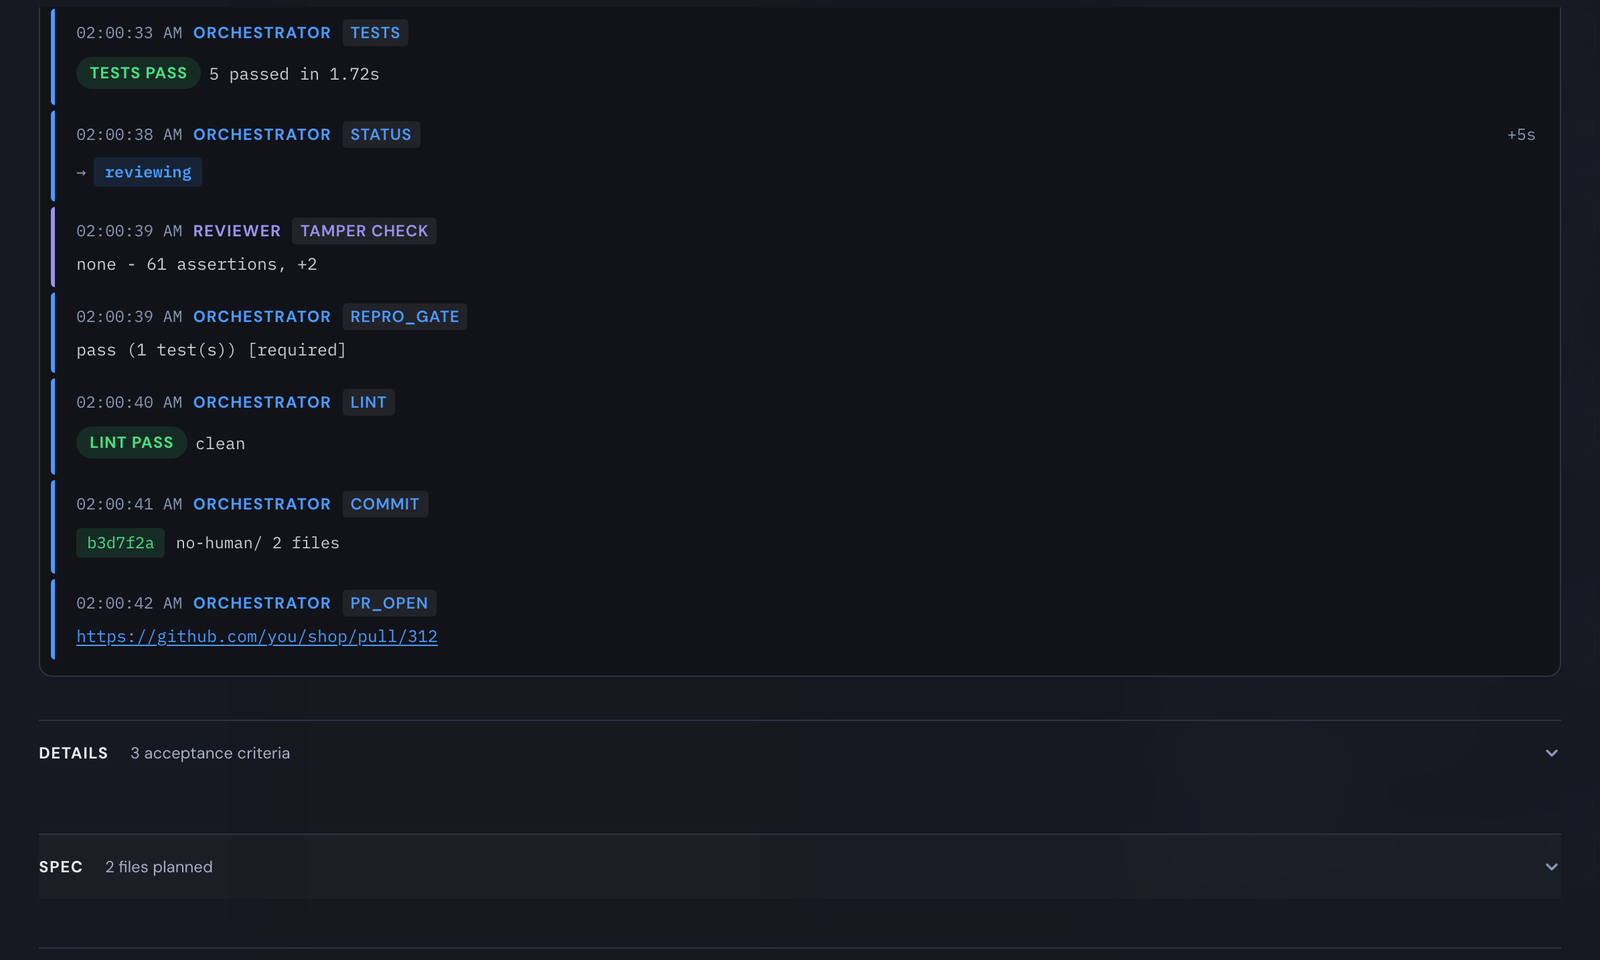
Proof the fix fixed the bugThe tests offered as evidence must fail on the old code and pass on the new. The gate runs both, and the event log shows the verdict. |
|
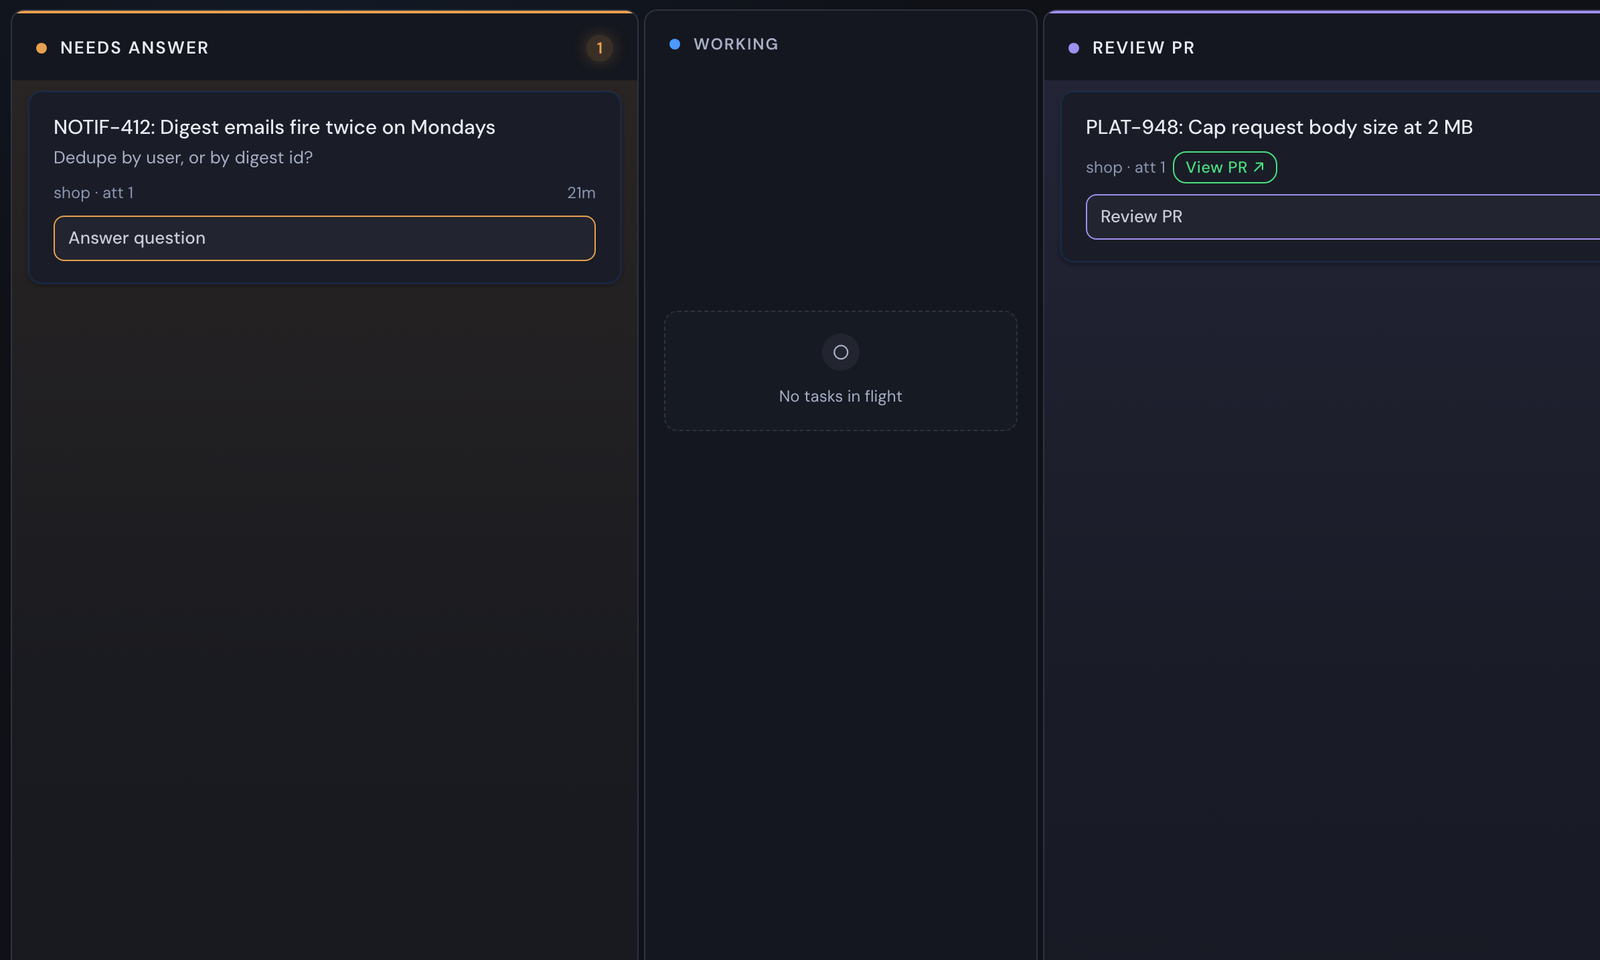
An honest stopWhen it needs you, it parks with one specific question instead of guessing. |
|
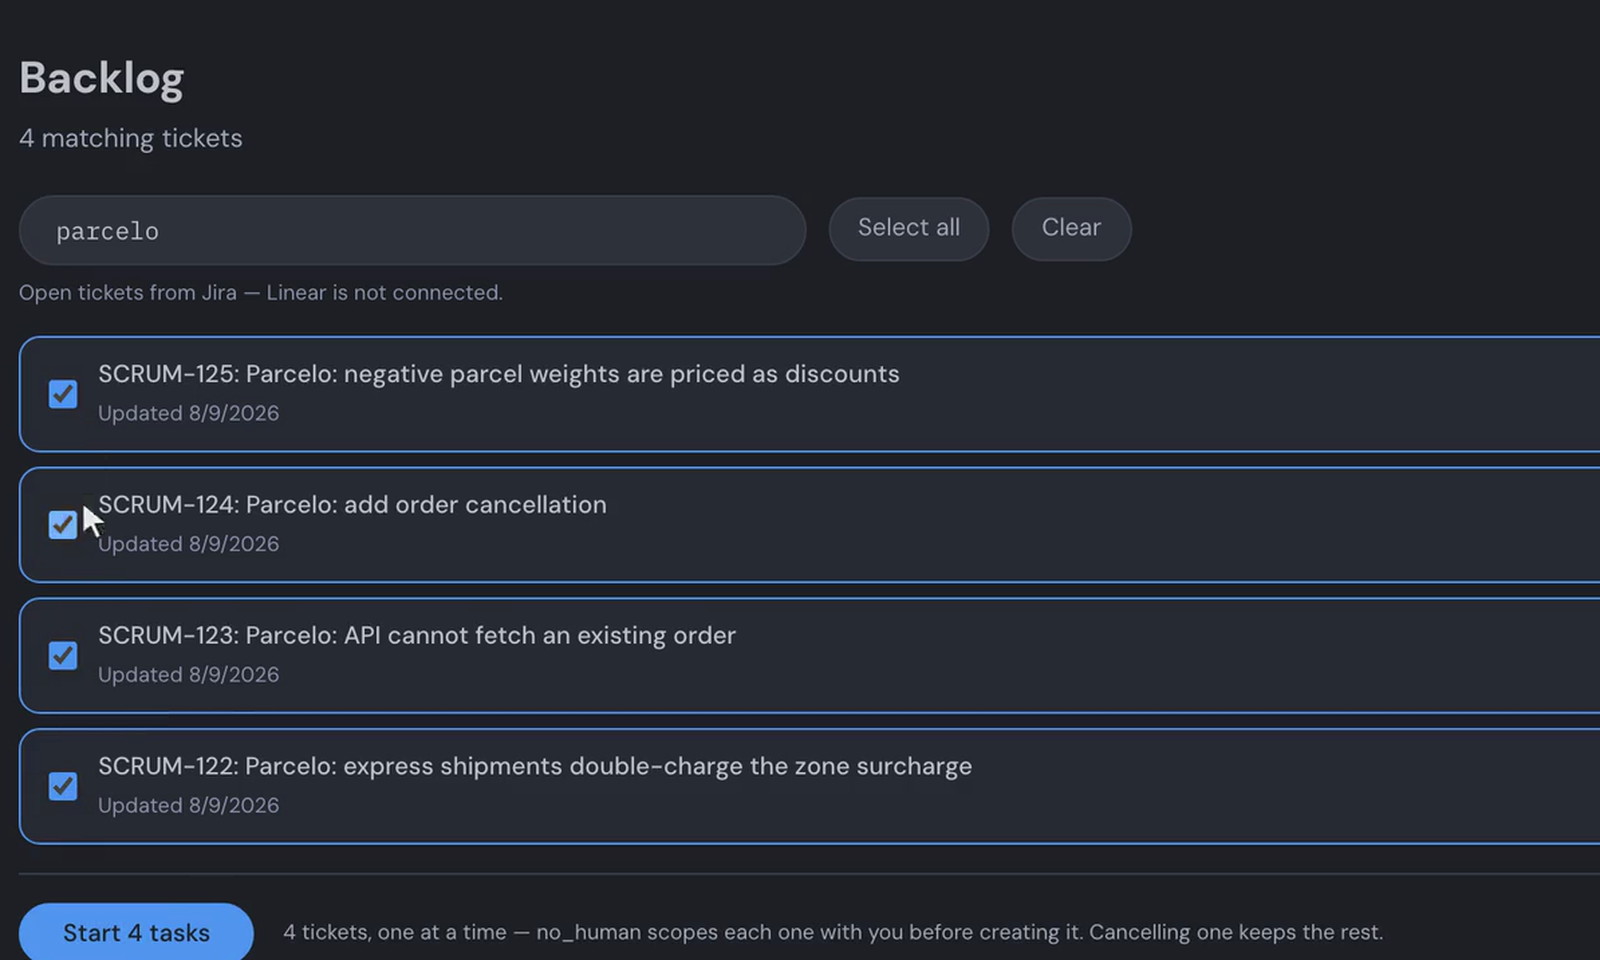
Your tracker's tickets, on your boardPick Jira or Linear tickets from the backlog (monday.com boards are polled). Each one is scoped with you before it starts. |
|
▶️ Play the full demo — 1:33, from Jira board to review-passed PR
## GitHub Action Run the same adversarial reviewer and tamper guard as a pull-request check — one shot, no daemon, no `~/.no_human` database, and not the queueing `nh review` CLI path. It judges the diff alone: unlike a local run, it collects no lint, wiring or type evidence and does not explore the repository. It posts a single pass/fail checklist comment with `file:line` citations, found by its own marker and updated in place on every run rather than creating a new one each time. ```yaml # .github/workflows/review-gate.yml name: no_human review gate on: pull_request: permissions: contents: read pull-requests: write jobs: review: runs-on: ubuntu-latest steps: - uses: actions/checkout@v4 with: fetch-depth: 0 ref: ${{ github.event.pull_request.head.sha }} - uses: no-human-ai/no_human@main # no versioned tag yet — see below with: credential: ${{ secrets.ANTHROPIC_API_KEY }} github_token: ${{ github.token }} ``` `permissions.contents: read` lets `actions/checkout` read this repository; `pull-requests: write` is what lets the Action post/update its own comment. Neither grants anything broader. The checkout step's explicit `ref: ${{ github.event.pull_request.head.sha }}` matters too: on a `pull_request` event, `actions/checkout` otherwise checks out an ephemeral merge commit rather than the PR's actual head, and the Action reviews and cites line numbers against whatever tree is on disk — it refuses to run rather than review the wrong one, so omitting `ref:` here turns into a red, actionable exit `2`, not a silent misreview. This Action has no versioned release yet — `no-human-ai/no_human`'s tags today run `v0.1.0` through `v0.2.3`, none of which contain `action.yml`. A `v1` tag will be cut at the first release that ships it. Until then, pin to `@main` for the latest revision, or better, pin to the exact commit SHA you've reviewed (`no-human-ai/no_human@