# Proofpane
**Proofpane is an AI governance platform — the evidence plane for governed AI work.**
Every AI action across coding agents (Claude Code, Cursor, Codex, Hermes, Claude
Desktop), workflow platforms (n8n, UiPath, Power Automate, Zapier, Make) and direct
LLM API calls is policy-gated **in the execution path** (allow / deny / redact /
pause for a human), cost-metered, and recorded in a SHA-256 hash-chained,
tamper-evident audit log that exports as an **Ed25519-signed Evidence Pack** an
auditor verifies **offline** — no vendor account, no trust in us required.
## The architecture
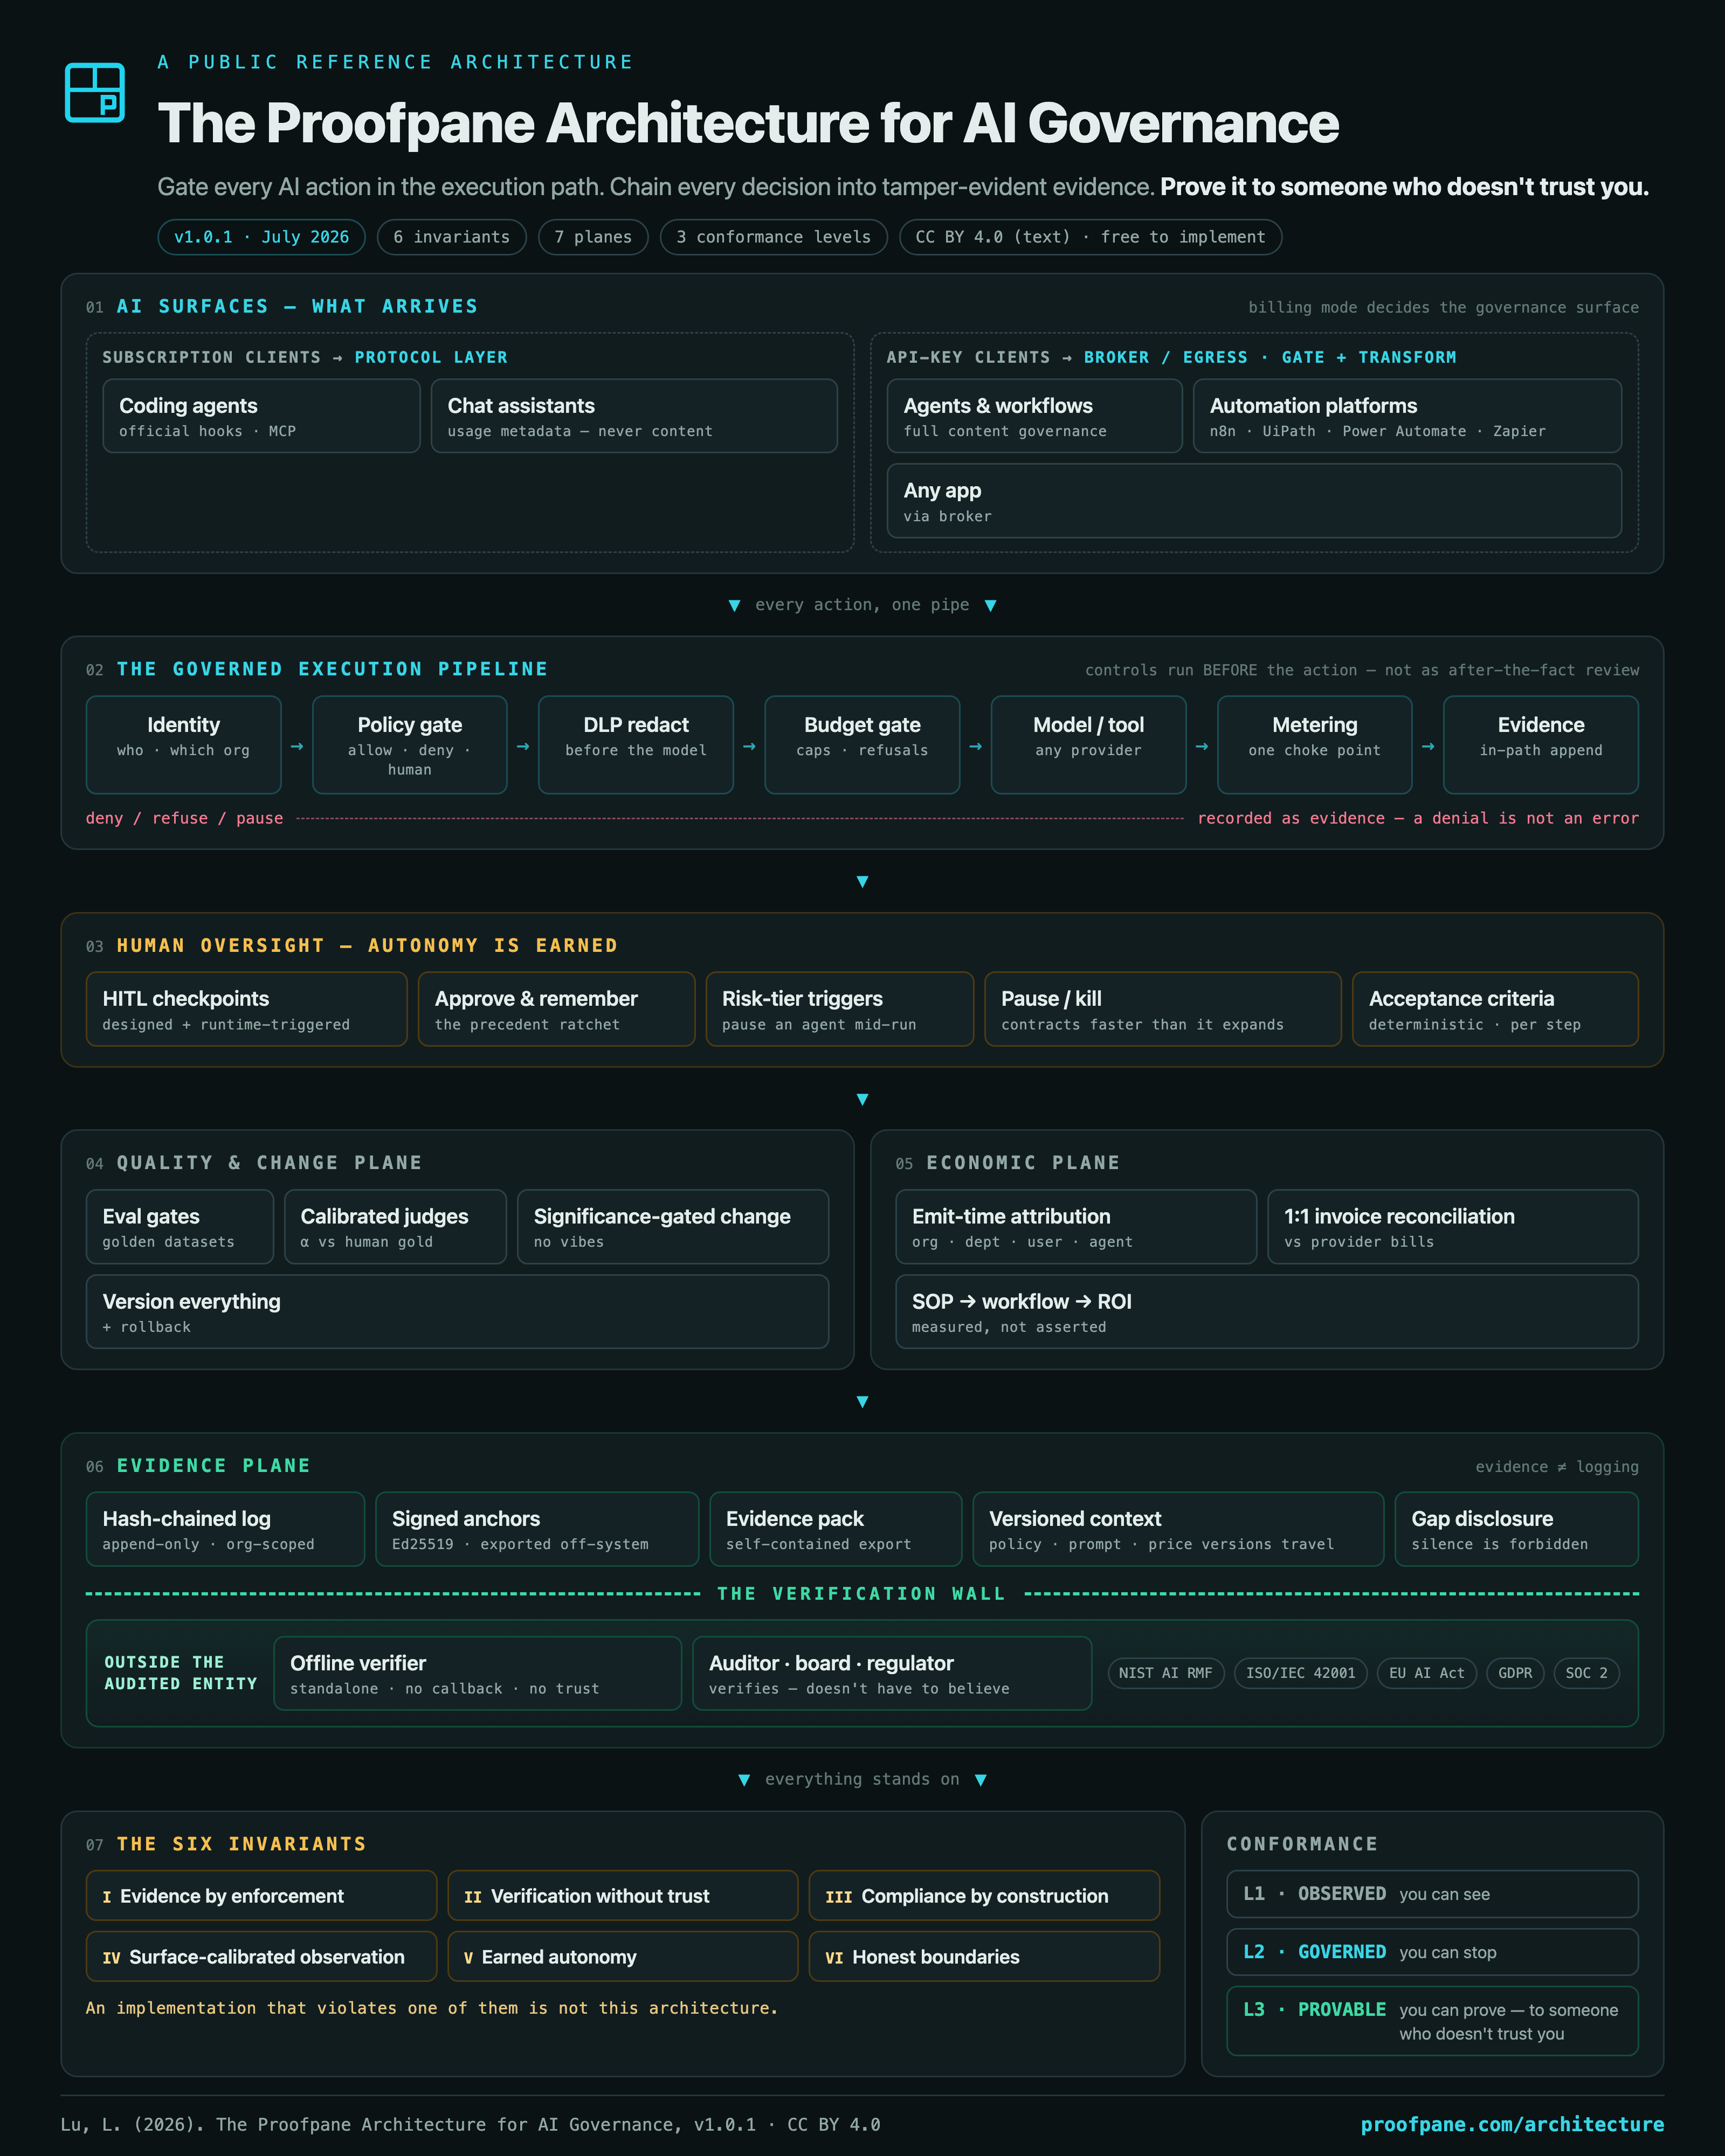
**Our claim: governance must happen at runtime, and the record it leaves must be
tamper-evident.** A policy that is checked after the fact governs nothing — by
the time a review reads the log, the secret has left, the payment has cleared,
the decision has shipped. So the gate sits **in the execution path**: the AI
action does not complete until policy has allowed it, redacted it, or paused it
for a human. And a record the operator can quietly edit proves nothing — so
every decision is appended to a **SHA-256 hash-chained, append-only log**
(DB-level immutability trigger, Ed25519 chain-head anchoring) whose export any
auditor can verify **offline, against a published rubric, without trusting the
operator or us**. Runtime enforcement produces the evidence; the evidence does
not depend on anyone's word — including ours.
The architecture is a **public, versioned reference** — not a private rubric:
- **Read it:** [proofpane.com/architecture](https://proofpane.com/architecture/) — interactive map + full Markdown spec
- **Cite it:** DOI [10.5281/zenodo.21402331](https://doi.org/10.5281/zenodo.21402331) (CC BY 4.0 — anyone may implement it)
- **Core claim:** evidence must be checkable by parties who trust *neither the operator nor the vendor* — and so must the rubric it is graded against. A standard that can quietly move is not a standard.
The MCP server below is one enforcement point of this architecture: the
on-machine gate for MCP-speaking AI clients.
## This repo
This repository mirrors Proofpane's public evidence and documentation and
preserves historical daemon release artifacts. The main Proofpane codebase is
private. The current supported binaries are served from
; the canonical version, digest and
platform-signing record is [`docs/releases.json`](docs/releases.json).
## What you can do with just the download
No account, no pairing, no talking to us first:
- **Run the MCP server** — `airgov_daemon mcp` serves 13 governed tools
(`bash`, `read`, `write`, `edit`, `glob`, `grep`, `listdir`, RAG search,
session search, skills) to any MCP client. Local policy gates and DLP
redaction are active: a secret in a file read is masked before the model
sees it, on your machine, with no cloud in the loop.
- **Scan your coverage** — `airgov_daemon coverage` reads this machine's
AI-client configs and shows which MCP servers route through governance and
which run direct (ungoverned).
- **Check the monitoring switch** — `airgov_daemon monitoring-status`, and
`disable` / `enable ` to turn per-app monitoring off and on.
- **Preview usage extraction** — `airgov_daemon usage-sync --dry-run` shows
what token/usage data WOULD sync, without sending anything.
Pairing with a Proofpane org (`airgov_daemon pair `) connects the daemon
to the server side: the cloud audit chain, human-approval gates, org-wide
policy sync, and Evidence Pack export.
## Proofpane MCP server
`airgov_daemon mcp` is a stdio [Model Context Protocol](https://modelcontextprotocol.io)
server — a governance layer that runs on the user's machine and exposes local
tools to MCP clients (Claude Desktop, Cursor, Codex, …) under policy control.
Every call is policy-gated, DLP-redacted before a model sees a secret, and
recorded on a hash-chained, offline-verifiable audit trail.
**Tools advertised** (`tools/list`, no pairing needed): `bash`, `read`, `write`,
`edit`, `glob`, `grep`, `listdir`, `search_compliance_docs`, `ingest_to_rag`,
`session_search`, `skills_list`, `skill_view`, `skill_manage`.
### Run it
```bash
airgov_daemon mcp # stdio MCP server (from a downloaded binary)
```
### Container / directory checks (e.g. Glama)
A [`Dockerfile`](./Dockerfile) is included that pulls the public prebuilt Linux
binary and runs the server in `mcp` mode, so an automated directory can start it
and introspect (`initialize` + `tools/list`) **without the private source**:
```bash
docker build -t proofpane-mcp .
docker run --rm -i proofpane-mcp # speaks stdio MCP
```
## Get the current daemon
Use the fail-closed installer at
[proofpane.com/install](https://proofpane.com/install). It selects the native
artifact, verifies its published SHA-256, and on macOS requires the exact
PROOFPANE LIMITED Developer ID (team B94QM75QNG) plus Apple's accepted
notarisation verdict before replacing an installed file.
The current channel is and its authority is
[`docs/releases.json`](docs/releases.json). The public GitHub binary archive
currently stops at daemon v1.5.19; it is preserved as history and is **not** the
current distribution channel.
## SHA-256 verification
Every current binary has a `.sha256` sibling. The installer verifies it
automatically before installation. For manual inspection, download the artifact
and its sibling from and compare them with
`shasum -a 256` (macOS) or `sha256sum` (Linux). The platform matrix and expected
digests are also recorded in [`docs/releases.json`](docs/releases.json).
## Reporting issues
For daemon issues, email Louie.Lu@proofpane.com.
## License
This mirror repo's scaffolding (this README, the `Dockerfile`, `glama.json`) is
released under the [MIT License](./LICENSE). **The Proofpane daemon it
distributes is proprietary software** — see [proofpane.com](https://proofpane.com).
The architecture reference is CC BY 4.0 via its [DOI](https://doi.org/10.5281/zenodo.21402331).