
# agent-security-scanner-mcp
**Security scanner for AI coding agents, MCP servers, prompts, and AI-suggested packages.**
Run it before Claude Code, Cursor, Windsurf, Cline, OpenCode, or another agent trusts new code, tools, prompts, or dependencies.
[](https://www.npmjs.com/package/agent-security-scanner-mcp)
[](https://www.npmjs.com/package/agent-security-scanner-mcp)
[](LICENSE)
[](https://github.com/sinewaveai/agent-security-scanner-mcp/actions/workflows/test.yml)
## Copy-Paste Start
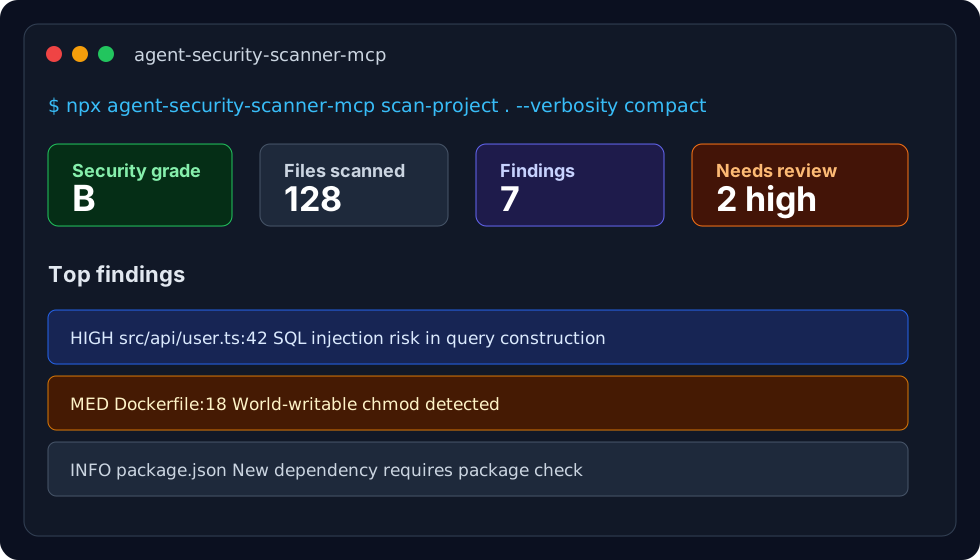
Scan any repo and get an A-F agent security grade:
```bash
npx agent-security-scanner-mcp scan-project . --verbosity compact
```
Install the scanner into your AI coding client:
```bash
npx agent-security-scanner-mcp init claude-code
```
Replace `claude-code` with `cursor`, `claude-desktop`, `windsurf`, `cline`, `kilo-code`, `opencode`, or `cody`.
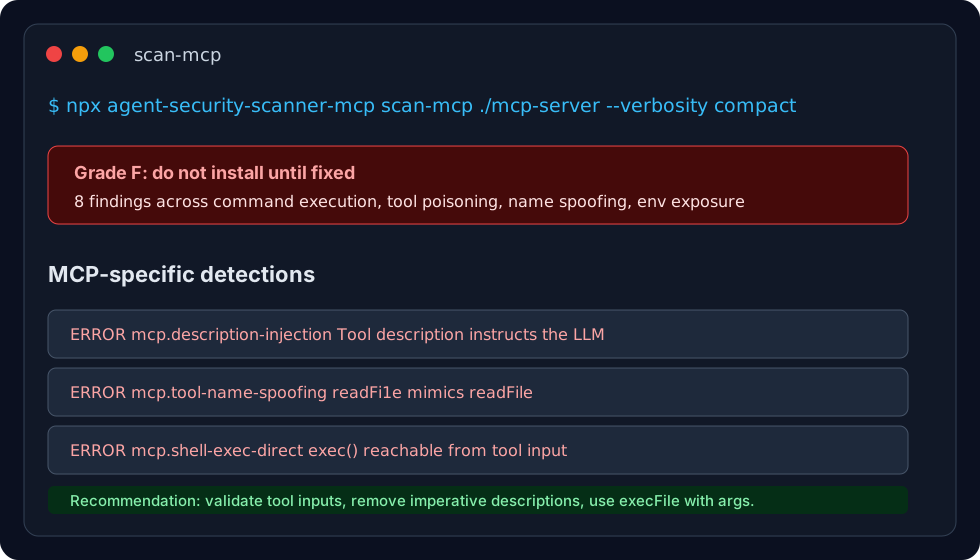
Audit an MCP server before adding it to an agent:
```bash
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
```
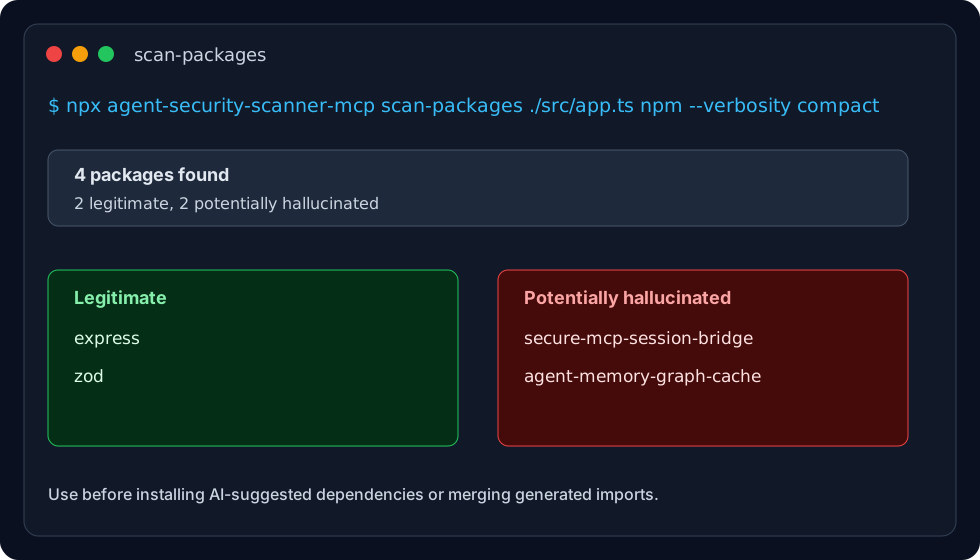
Check AI-generated imports for package hallucinations:
```bash
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
```
## What It Catches
| Risk | Why agents need it | Command |
| --- | --- | --- |
| Vulnerable generated code | Agents can introduce SQL injection, XSS, command injection, unsafe crypto, and secrets | `scan-project`, `scan-security`, `scan-diff` |
| MCP server attacks | MCP tools can poison descriptions, spoof names, exfiltrate env vars, or execute commands | `scan-mcp` |
| Prompt injection | Agents often process untrusted docs, tickets, pages, and tool output | `scan-prompt` |
| Unsafe agent actions | Catch dangerous shell/file/network actions before execution | `scan-action` |
| Hallucinated packages | AI often invents dependency names that attackers can later squat | `check-package`, `scan-packages` |
| SBOM and CVEs | Generate CycloneDX SBOMs and scan dependencies with OSV.dev | `sbom-generate`, `sbom-vulnerabilities` |
| Semantic review | LLM-powered review that uses project intent to find context-aware issues | `cr-agent` |
## Screenshots
### Project Scan
### MCP Server Audit
### Package Hallucination Detection
## Demos
Run a safe local demo that creates intentionally vulnerable fixtures, scans them, and cleans them up.
```bash
# MCP audit demo: tool poisoning, spoofed tool name, command execution, secret exposure
npx agent-security-scanner-mcp demo --type mcp --no-prompt
# Package hallucination demo: real imports mixed with fake AI-generated package names
npx agent-security-scanner-mcp demo --type packages --no-prompt
```
Expected demo shape:
```json
{
"grade": "F",
"findings_count": 8,
"findings": [
{
"rule": "mcp.description-injection",
"severity": "ERROR",
"message": "Tool description contains imperative language directed at the LLM."
},
{
"rule": "mcp.tool-name-spoofing",
"severity": "ERROR",
"message": "Tool name is close to a well-known MCP tool name."
}
]
}
```
## Install In Your Agent
```bash
npx agent-security-scanner-mcp init claude-code
```
| Client | Setup |
| --- | --- |
| Claude Code | `npx agent-security-scanner-mcp init claude-code` |
| Cursor | `npx agent-security-scanner-mcp init cursor` |
| Claude Desktop | `npx agent-security-scanner-mcp init claude-desktop` |
| Windsurf | `npx agent-security-scanner-mcp init windsurf` |
| Cline | `npx agent-security-scanner-mcp init cline` |
| Kilo Code | `npx agent-security-scanner-mcp init kilo-code` |
| OpenCode | `npx agent-security-scanner-mcp init opencode` |
| Cody | `npx agent-security-scanner-mcp init cody` |
| Interactive picker | `npx agent-security-scanner-mcp init` |
Then restart the client. Your agent can call the scanner as an MCP tool.
## Agent Playbook
Paste this into an agent task when you want it to work safely:
```text
Before trusting new code, dependencies, prompts, or MCP tools, run:
1. npx agent-security-scanner-mcp scan-project . --verbosity compact
2. npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact when imports change
3. npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact before adding MCP servers
4. npx agent-security-scanner-mcp scan-diff --base main --target HEAD before opening a PR
Fix high-confidence security findings before continuing.
```
## Common Workflows
### Before You Trust An Agent-Written PR
```bash
npx agent-security-scanner-mcp scan-diff --base main --target HEAD --verbosity compact
npx agent-security-scanner-mcp scan-packages ./src/app.ts npm --verbosity compact
```
### Before Installing An MCP Server
```bash
npx agent-security-scanner-mcp scan-mcp ./path/to/mcp-server --verbosity compact
```
### Before Adding A Dependency Suggested By AI
```bash
npx agent-security-scanner-mcp check-package express npm
npx agent-security-scanner-mcp scan-packages ./package.json npm --verbosity compact
```
### Add CI
```bash
npx agent-security-scanner-mcp init-ci github
```
### Generate Share Copy From A Real Scan
```bash
npx agent-security-scanner-mcp scan-project . --verbosity compact > scan-result.json
npx agent-security-scanner-mcp share-kit --scan-result scan-result.json --output share-kit.md
```
## CLI Reference
| Command | Use |
| --- | --- |
| `scan-project